A destructive wiper cyberattack on Russian web host Beget erased virtual private servers, cloud storage, and all binary disk-image backups. More than 1,000 physical servers face manual inspection.
MetaMask and Consensys disclosed an infrastructure breach that diverted 0.385 ETH in validator execution-layer rewards. Staked 32 ETH principal and withdrawal credentials remained safe from compromise.
Ahold Delhaize discloses that an October 2026 cyberattack will reduce Q4 net sales by €200M to €250M and cut operating income by €75M to €100M. Supply chain freezes and e-commerce shutdowns triggered full-year earnings guidance downgrades.
Chainalysis confirms universal credential and token exposure across all users following an on-path attack. Core compliance tools forced offline for up to 92.5 hours (derived) as phased restoration requires mandatory IP allowlisting.
DigiCert reveals an internal server migration exposed customer records for 513 days. Technical breakdown of the open self-registration authorization flaw, compromised passport and driver license files, 109-day triage delay, and unaffected CA root keys.
What the French banking group's two notices of 4 November state and leave out: the supplier route, the own account, possible conversion to crypto, an unconfirmed 118 million euros set against its own results, and a ranked checklist.
The 72 minutes between the disclosure's two times against its own 'about 70 minutes' and an advisory log that runs to 12:46: eight places the vendor's two notices differ, four counts that do not merge, and a ranked checklist.
What WorkOS's bulletin states and does not state: four data categories, the accessed versus provided access wording, what no evidence means, who names ARTEX, the derived dates, and a ranked checklist for customers.
What Chainstack's incident page states and does not state: the four dates and derived day counts, what was accessed versus treated as exposed, what a hash protects, the rotation documentation, the one page that names Chainstack in a campaign, and a ranked checklist.
What Michigan State's status page, student newspaper and spokesperson say, what a leak site claim and a tracker's copy say, the derived 31 day gap, what the sources do not establish, and a ranked checklist. Live incident, time stamped.
Nine status entries, 68 hours 46 minutes from disable to restore (derived), and no statement of cause, data or credentials. What Abrigo's own pages say, what they do not, and a ranked checklist for lender customers.
What Trigger.dev's own blog notice and status entry of 1 November 2026 establish, what they leave out, how they compare with the vendor's 6 October report, and a ranked checklist for customers.
Store counts by country and source, what is said about the defrost mechanism and by whom, what CERT-FR and Copeland say about the October units, what is not stated, and a ranked checklist for refrigeration and security teams.
The first government attribution of the Binance theft: what the FBI alert of 31 October states, what it leaves out, whose $6.43 billion figure is whose, what the 628 addresses cover, and a ranked checklist for virtual asset businesses.
What Northflank's status page establishes about its security incident, the dates it gives and the one it does not, what Wiz's Black October report adds and omits, four labels that are not controls, and a ranked checklist for customers.
What Chainalysis's 30 October 2026 notice states, what it does not (route, dates, count, which customers), what the phrase offensive agentic techniques can and cannot tell a reader, and a ranked checklist for customers, with questions to put to the vendor.
What Revolve's 8 K and the Texas listing state about saved card data, the four fields named, the six questions left open, the counts by state and the gap to an unknown total, with a ranked checklist.
What the FEC status page, its notices and Reuters state about the electronic filing outage of 26 to 28 October 2026, what none of them states, the 24 hour and 48 hour windows it landed on, and a ranked checklist for filers.
What the Department of Justice release of 29 October 2026 states about the 42 month sentence, the hoax post and the $136 billion figure, what it does not (plea, counts, method), the 2013 reports, and a ranked checklist.
What the Polymarket status page, Hudson Rock and the news reports establish about the DebugBear script, whose number is whose, what the script did and did not do, and a ranked checklist for sites with wallet or payment pages.
What Binance, TRM and Chainalysis say about the roughly $6.3 billion theft of 29 October 2026: the conditional laptop claim, the 20 minute sweep, what frozen means, and which part of the North Korea attribution is evidence and which is confidence.
What RIZAP's notice of 3 September 2026 and four client notices print: the fields, three counts that do not add up, the dates, the provider's relayed reply, the PPC reporting page, and a ranked checklist against shadow AI.
What the department's data breach page and release say, what they leave out, five dates kept apart, Florida's 30 day notice law, and ranked checklists for people who applied for aid and for any school or agency with a student portal.
What Belgium's FPS Finance states about the MyMinfin cyberattack, read in French and Dutch, how its wording moved in 25 hours, what is not stated, the three deadline dates, and a ranked checklist.
What iRhythm's notice, its sample letter, the HHS OCR portal and the Washington Attorney General establish about the June data theft, what they leave out, the 116 day gap and a checklist for hosted applications.
What 123 Reg's customer notice, as reported, establishes about an attack it calls AI driven and Chinese linked, and what it leaves out: the dates kept apart, the evidence for each claim, CrowdStrike's different assessment, the ICO tests and a ranked checklist.
What Sony's notice and questions page say about the So-net breach, the dates kept apart, how 2,585,481 is built, what leaked and what Sony says did not, where the news report differs, and a ranked checklist.
What GMO's fourteen notices, two brokers' own pages and the service page establish about the Onamae.com Desktop Cloud attack: the dates, the 26,739 figure, the 8 billion yen demand, the reward against the payments, and what is not stated.
What Warp's chief executive is reported to have said about a vendor exploit, why four labels for the exposed data are not defined, what Warp's own documents say it collects, and a ranked checklist for teams using an AI terminal.
What UNM's own notices say about the 26 October cyberattack on its Health Sciences Center, what they leave out, a group's claim, three wordings of the diversion, and a ranked checklist for hospital downtime. Live incident, time stamped.
What Denver Health Medical Plan's notice and the HHS breach portal entry establish about a vendor key published for 417 days, the fields listed, what the plan does not say about logs or a finder, and two ranked checklists.
What Keystone's statement, as reported, establishes about the stolen verification key, the 18,835 unsold wallets, the owners of devices delivered after 20 October, the customer data that should have been deleted, and what its own pages still say.
What the university's three dated entries state and leave out, the arithmetic behind 525,000 and 68 to 92 hours, what Datatilsynet says the 72 hour clock is, a stated and not stated table, and a ranked checklist for affected people and for organisations with identity data in test systems.
The Seoul police release read on 27 October 2026: 90 companies, 8.2 million records and 38 extortion demands alleged, 15 firms and about 900,000 records referred, and no product named for the AI tool. What it does not say, and a ranked checklist for buyers of penetration tests.
What DreamHost's own status page states and leaves out about its forced email and FTP/SFTP password resets, the clock from 23 to 25 October, the lockout that falls on account owners, and a ranked checklist for customers and agencies.
CBC's count of Canadian tips in the March 2026 hack of the P3 tip platform, what Toronto Crime Stoppers says it was told and when, and which programs have paused.
Railway’s preliminary account describes CI credentials, artifacts and a subset of decrypted environment variables. The 100,000-workspace figure is an upper bound, while the entry route, exact keys and source-code question remain unresolved.
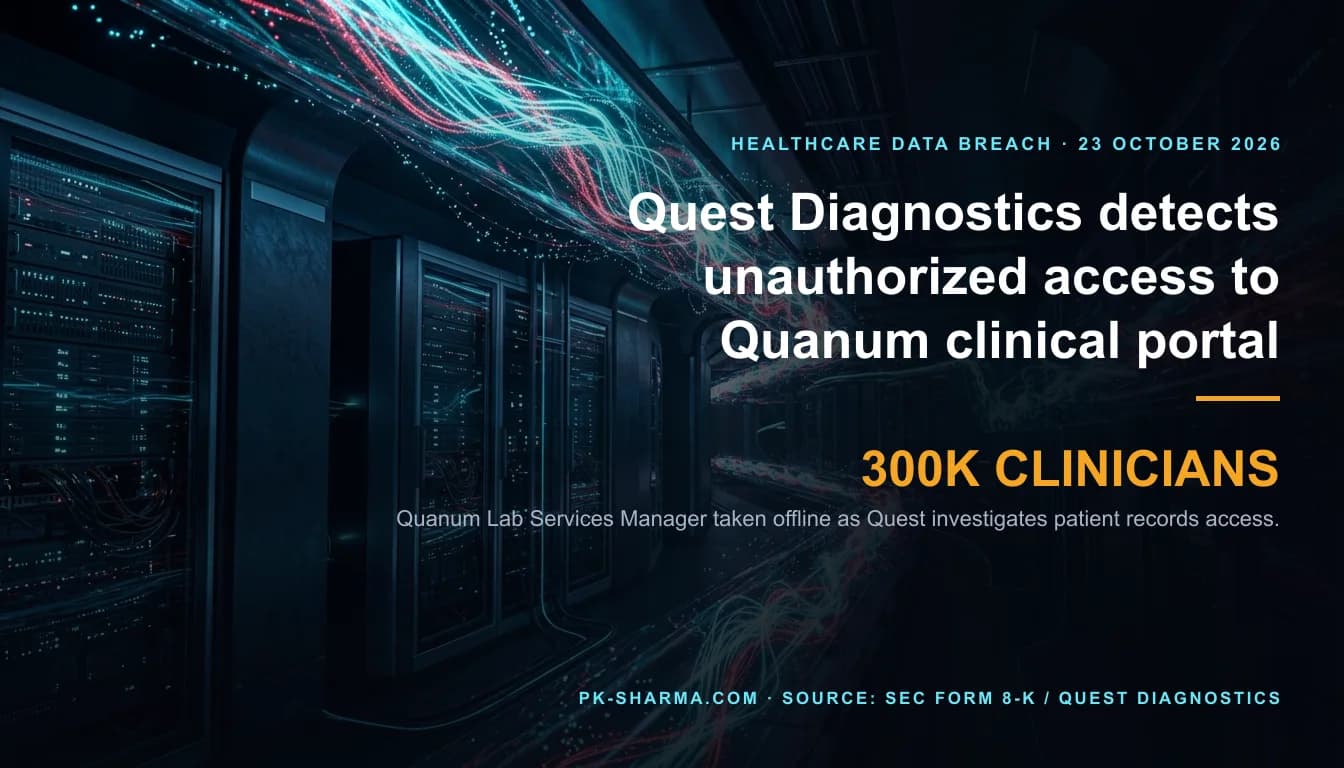
Technical analysis of Quest Diagnostics SEC Form 8-K: unauthorized intrusion into Quanum LSM clinical portal exposes patient records across healthcare network.
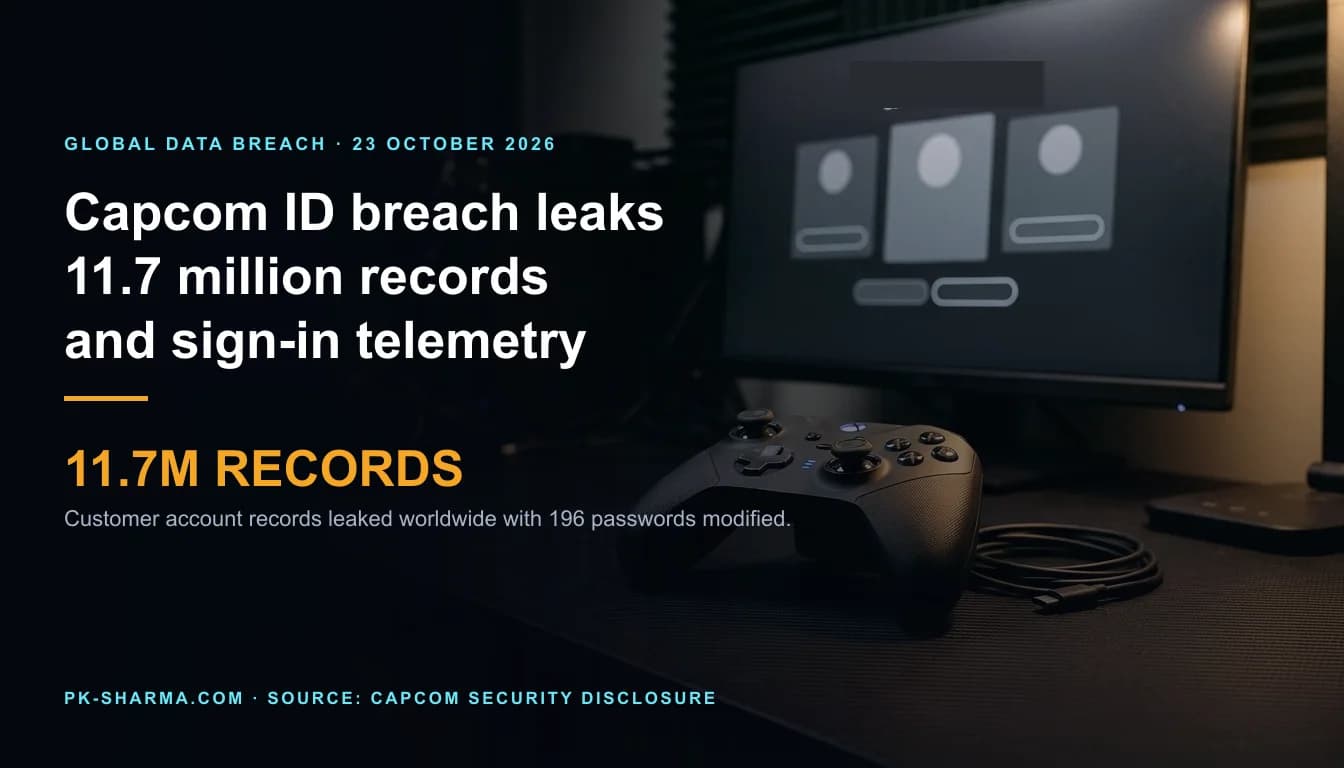
Technical breakdown of the Capcom ID data breach: 11,774,247 customer records exposed, 196 unauthorized password changes, and sign-in IP telemetry weaponization.
A validly signed remote command crossed the trust boundary into connected WordPress sites. Key revocation and removal of earlier site changes are separate tasks.
What Google's status entries say, minute by minute, what its documentation and SLAs promise when one zone fails, who said what in the UK, and what the PRA, FCA, ICO and Treasury regimes require. A developing incident, time stamped.
What Bullhorn's status page, FAQ and known limitations page state and do not state about its cyber incident, the credential changes, and what UK controllers and processors must do under the ICO and NCSC texts. Time stamped 20 October 2026.
What OpenCode's X post, docs and status page state about the Console breach as of 19 October, what they leave out, the afternoon's timestamps with derived intervals, what the providers' pages say to do, the UK position, and a ranked checklist.
What the Trust's 16 October statement establishes (34 hearing outcomes, 15 dismissals) and omits, how its own evidence says the access was found, what the ICO, NMC, GMC and NHS England pages say, and a ranked checklist for holders of health records.
What New York's agreement with BCHP and XTIUM states and leaves out: 4 days from warning to detection, 18 client systems reached and one breached, $2.7 million announced against $4 million on paper, 825,000 or 820,000 New Yorkers, and what UK suppliers should check.
What the ETS notice filed with the California Attorney General states and leaves out: 119 days between its two dates, 126 to discovery, who says 7 million, what CDE's own pages could not be read for, other regulators' lists, and what UK suppliers should check. Defender level.
What Huntress, Todyl and ConnectWise state about a stolen Cloud Backup application credential: 162, over 300 or almost 1,000 tenants, a 141-minute window, 35 h 34 min to the first advisory, and no confirmed data access. Where UK guidance and the Bill stop. Defender level.
What the Judiciary, nine courts, the bankruptcy rules, BAE's newsrooms and the UK texts establish about the BNC outage, what they leave out, the arithmetic against 14, 21 and 28 day windows, what UK buyers of outsourced systems can rely on, and three ranked checklists.
What German, Japanese and UK authorities have stated about the Qilin arrest and the Synnovis attack, what no record states, whose numbers the 4,000 and 140 million are, how the death link was established, which UK laws could apply and where each stops, and a checklist for suppliers and CISOs.
A source-led timeline, the operational split between filing and service, district-by-district orders, and the facts still missing about the BAE Systems incident.
What the Legal Aid Agency's 14 October 2026 update states about records back to 1978, what it leaves out, the arithmetic behind the moving start date, why old records were online, what UK law and policy say, and a ranked checklist. Defender level only.
What the complaint, the Justice Department and OpenAI each say about the alleged recorder in an OpenAI meeting room, where the press accounts differ, what the record does not establish, what UK guidance covers, and an ordered checklist for AI and R&D labs.
What the court record, the FBI Director's post and the RCMP statement establish about a reported arrest, the 23 days since the Dutch arrest, what is not stated, what the NCSC, ICO, OFSI and Home Office pages say about choosing a response supplier, and an ordered checklist.
What the Ombudsman's statement and its own published figures establish about a third-party incident in its case management system, what they leave out, the 72 hour clock, UK GDPR, NCSC and sponsor guidance, and ordered checklists for residents, landlords and small public bodies.
What SecurityWeek's report of Meta's statements establishes, why the 1% cannot be turned into a count of people, the 14 to 42 day gap, what GitHub's controls document, the UK GDPR, NCSC and Cyber Essentials reading, and an ordered checklist. Defender level only.
What one company has stated about its Sunday incident, by whom and when, set against what customers must infer. Also H&M's denial of a ShinyHunters claim, the UK GDPR 72 hour limit counted from Sunday (derived), and two ordered checklists.
What the group, Albert Heijn and Delhaize each state, the sentences reused from 2024, the day's disclosures to scale, the 2024 notices, what the NPSA, NCSC and ICO say, and ordered questions and actions for UK retailers and suppliers to European grocers. Defender level only.
What CERT-FR, Danfoss, the retailers, the Prime Minister's office and the Paris prosecutor have each said, the counts that do not reconcile, the dates of Danfoss's fixes against the attack, what UK rules and the FSA say, and a ranked checklist. Defender level only.
Three ccTLDs, no certificate count, no dates, no CA names. Under the Baseline Requirements a validation completed this autumn can back a certificate valid to 30 September 2027, and CAA and Certificate Transparency are the owner's tools.
The channel is confirmed and the Snowflake claim is not addressed. What the RNS says and leaves out, what UK GDPR and UK MAR say, and what to do about every platform that can message your customers.
A superseded sign-on service stayed in production because an internal system still called it. Bromcom found the breach on 6 September, posted on 24 September, and by 30 September called the central question ongoing.
Microsoft's 13-million-follower X account carried a disclaimer that told readers to trust only official channels, and Microsoft says it did not write it. The minutes, what is not stated, five routes in, and a UK checklist.
What Nikkei's notices say in Japanese and English, what they leave out, how Japanese and UK law treat the security of data held for journalism, and an ordered checklist for any organisation that holds the names of sources or whistleblowers.
A supplier to US school districts found a flaw on 14 August and was first reported notifying districts on 1 October, 48 days later. Staff Social Security numbers were taken; the product, the counts and the actor are not stated.
About 80 per cent of the register, more than the population, reached through one company's lawful access. What the ministry and Datatilsynet state, what CPR's own terms say about controls, and the checks a UK team can run.
Shinhan, KB Kookmin and Hana name about 25,000, 99 and 89 customers. The AI-tool claim rests on a vendor researcher's page-title reading and an anonymous official; on the record it is 'cannot be ruled out'. What is stated, what is not, and a UK checklist.
Four in five of DTU's up to 200,000 are former users, and the six-month deletion covers addresses, pictures and next of kin, not the CPR number. What the notice states, what it leaves out, and the checks a UK team can run.
Three provisional arrests, five servers, five domains and 110 TB, in a case led from Hamburg with one arrest in the UK. The counts do not match, and no release describes how victims will be told or what happens to files already published.
The 10.0 flaw has a CVE, a score and a fixed version. The flaw Kiteworks said it found during the shutdown has none that any record attaches to it, and no advisory in the batch says whether it is there.
The beacon chain shows 226,112 ETH of Lido stake queued to exit 6 to 12 hours before MetaMask's first notice. The notice and Lido's post name no cause, no count and no key status, and no funds lost are reported.
Ten days on, DIVD's breach has a root cause: two Zammad flaws, one with no fix on record. The evidence for an AI agent is still tempo and comments in scripts, and the Zammad finding does not add to it.
The Pentagon's personnel data centre dated its breach letter 64 days after discovering the flaw, after at least 258 days of access. What the notice states, what it leaves out, and the checks a UK team can run.
Two forensic documents published on 30 September add a longer chain, two products, a web shell and a custom withdrawal tool. SlowMist's logs start on 31 August, Mandiant dates the appliance access to 24 September, and neither names a product, vendor or CVE.
Faav's write-up counts 17,333,335,124,315 rows from metadata and describes two one-row samples. The endpoint was locked down 4 days after the report, the bounty was $5,000, and Microsoft edited the only account.
The French tax administration took 49 days to learn of a theft made with stolen staff passwords, and only from the attacker's own post. What the ANSSI report establishes, what it leaves out, and the checks a UK team can run.
The record as of 29 September: an intruder that decided each step at machine speed, explained itself in code comments and fought its own tools. The flaw, the attacker, the model and the data outcome are all unstated.
A redirect changes where a name points, and the public record shows the registration layer stayed still. What is missing is the layer that moved, the real length of the window, and anything beyond Elsevier's own "no indication".
Bitget's account moved from a compromised backend system to a flaw in an unnamed third-party security product. The two are layers of one chain, not rivals, but the wording around them keeps shifting and the report that would test it is late.
The record moved in a day: a 40 word police post became a full statement with two suspicions, a custody ruling and a statement that the man was not arrested over Odido. The FBI claim is still a claim, and nothing official links the two.
Keio's first notice named no company. The group's own pages describe failures in payments, loyalty points, bookings, commuter-pass sales and inbound mail, while trains are reported unaffected and nobody has given a restoration date.
A 55-word notice and a press release close the Kiteworks shutdown. Neither carries a CVE, a score or a fixed version, and the vendor's own advisory register has nothing newer than 27 May 2026.
Times Car's parent says about 6.6 million accounts were breached, against a membership of more than 4 million announced in August. The notices name the data and the dates, and leave cause, attacker and headcount open.
UpGuard probed about 300,000 Supabase-using domains and found 16,326 with readable tables, about 5.4 per cent. Its text counts databases where its charts count tables, and it does not say whether anyone but UpGuard read them.
Migrating away from a processor removes the future risk and leaves the historic risk exactly where it was. Storage limitation is a legal duty, and it is also the only thing that would have helped here.
Firecracker per container is the strongest isolation on the market and it was not the boundary that mattered. A flag set for performance let a 4 KiB write expose the other 60 KiB of somebody else's block.
The public release says nine hours and federal intelligence authorities. The customer email, as quoted, says six hours and law enforcement. Both cannot be the number a defender acts on.
The researcher agreed to hold publication until 17 September. He asked for an update twice and got no reply. He published on the 24th, with no CVE and no patch in existence.
A Google engineer wrote Nice catch and filed it. Eleven days later a panel called it working as intended. The case is still open at P1 and S1, and the researcher's page says it is still unpatched.
Cloudflare has fixed a cross tenant exposure in Containers and Sandboxes. The flag took six hours to change. Clearing the blocks already mapped took fifteen days.
The Gyazo breach is being read as an account leak. Gyazo indexes the text inside every capture, so the 490 million metadata records are a transcript of what was on people's screens, and the leaked image IDs are the only lock those images had.
The court order lists 226 domains. Microsoft's own sworn declaration says device code theft cannot be stopped by multifactor authentication. What breaks the chain is a Conditional Access setting many tenants have never switched on.
The Ribon breach on BigCommerce: what each party has said, why app tokens cannot be revoked by merchants, the hours lost at each step, and why the app is not BigCommerce's sub-processor under UK GDPR.
AWS's AWSCompromisedKeyQuarantineV3 went on 10 seconds after a test leak. It is a deny list, not a lockdown: what it blocks, what it leaves open, and what you still have to do.
File History can stop backing up after September's Windows updates, mostly without a true error. Entra ID retires Microsoft-provided SMS and voice on 1 February 2027. What Microsoft requires, what it only recommends, and what to do.
Gyazo confirmed exceptional metadata exposure and a list of private image files. The disclosed fields can reconstruct the context around screenshots and drive secondary compromise.
A stolen Cloudflare key let an attacker rewrite Brevo's embedded scripts at the CDN edge, so origin files and their timestamps never changed. The earliest public evidence was a certificate logged 19 days before the injection.
KB5124008 makes Windows honour Machine Identity Isolation settings dormant since April 2025, breaking domain trust below Server 2025 level. What Microsoft says, what it does not, and the safe order of work.
The system was restored on 8 September. The aviation network still had a backlog to clear. A sourced timeline and worked recovery example explain the gap.
Google reports Breeze Comet running two waves of fraudulent transactions through Brazilian payment systems. The count is a victim’s, the only money figure is in a different section, and no rail validates intent.
The 91% figure describes the vulnerability catalogue, not the cause of breaches. The only quantified entry-vector number anyone can cite is a 2016 survey of about 222 sites.
Cosmos Labs' own policy calls for private distribution before public disclosure on a network-wide risk. The advisory also never reached the global GitHub database, so no dependency scanner ever raised it.
Ransom demands are collapsing and backups are working. Average recovery cost still rose 11% to $1.7m, and JLR lost five weeks of production for a modelled £1.9bn. The money moved from the ransom to the restore.
A 72-hour clause is not a control, it is an accounting mechanism. The clock starts at the vendor's awareness, which is the one variable your contract cannot set.