Ahold Delhaize says stores are open; Albert Heijn's chief says work has stopped at some distribution centres
Ahold Delhaize's six-sentence statement gives no cause, scope or start time, and three sentences repeat its 2024 wording. Albert Heijn's page puts the start on Sunday afternoon, and its chief executive told NOS work has stopped at some distribution centres.
By Parminder Kumar Sharma · · 26 min read
Six sentences from the group, and three of them were already published in 2024
Ahold Delhaize's statement on its network incident was published at 08:29 in Amsterdam, 07:29 BST, on Monday 12 October 2026. Counted from the page text, it is six sentences and 71 words before its legal notices (derived). Three of the six appear word for word in the company's statement of 8 November 2024 about its US incident: "Our teams are taking steps to assess and mitigate the issue.", "This includes taking some systems offline to help protect them." and "We apologize for any inconvenience this issue may have caused customers and partners." That is 3 of 6, or 50 per cent (derived), and the two statements are 703 days apart (derived). Both sit on the group's own newsroom, so the comparison can be checked there.
What the reuse does not establish is that the two incidents share a cause, an actor or a method. No source read says they are related. The reuse suggests a template (inference), and a template says nothing about what happened. What differs is the part that carried facts. The 2024 statement said outside cybersecurity experts were helping, that law enforcement had been notified, that the issue was in the US network, and that it had affected certain brands and services including pharmacies and some e-commerce. The 2026 statement says none of that. It says a security issue exists within the network, teams are assessing it, some systems are offline, and stores are open.
The brands say more than the group does. Albert Heijn's own outage page, last updated at 19:00 Amsterdam (18:00 BST), says the chain has been dealing with a cybersecurity incident "since Sunday afternoon". NOS reports Albert Heijn's chief executive saying that work at some distribution centres is "completely at a standstill" because systems were switched off as a precaution. The group statement mentions neither the start nor the supply chain. Its sentence about stores is true on its own terms, since NOS and Albert Heijn's page both say stores are open and tills work. It is a statement about doors, not about shelves: NOS reports the same chief executive saying that shelves will empty if this lasts, fresh products first.
This briefing reads the group's newsroom page, Albert Heijn's outage page and the company's 2024 notices directly, and everything else through press, attributed. The group statement was first read at 20:22 BST, 12 hours 53 minutes after it was published (derived), and the sources were re-read until 20:50 BST. Dutch and Belgian reports are translated by this briefing. Nothing was filled in or submitted. US brand sites, bol, Delhaize's own site and several newspapers refused scripted access and were not worked around, so what they showed is taken from press where stated.
The day in order: who said what, and when
The table lists what each source said on the day, in the order of its time stamp, with times in BST (Amsterdam and Brussels are one hour ahead of London). At 20:40 BST the group newsroom still listed one release on the incident. Everything else below comes from brands, press or agencies.
What each source said on 12 October 2026, with the time its page was stamped (BST). Dutch and Belgian items translated by this briefing. Reuters is read in the copy carried by The Globe and Mail.
| Time and source | What it states | What it leaves out |
|---|---|---|
| 06:56 NOS and 07:17 VRT, first reports | Albert Heijn, Etos and Gall and Gall in the Netherlands have no website, app or customer service. Albert Heijn cannot deliver online orders, and shelf labels show last week's prices. Delhaize in Belgium has no customer service and cannot take orders for the week, while its site and app were reachable. | Cause. Data. |
| 07:29 Group statement (08:29 Amsterdam) | A security issue within the network. Teams assessing and mitigating. Some systems offline "to help protect them". Stores open and serving customers "at this time". An apology. A notice that the text is inside information under the EU Market Abuse Regulation. | Cause, scope, start time, data, restoration time, law enforcement, outside experts, brands, countries. |
| 12:45 Delhaize, Belgium, via Belga | Stores in Belgium and Luxembourg open. Mostly internal systems switched off as a precaution. Customer service unreachable. Delivery slots for this week disabled. The distribution centre working. | When all systems return. Whether data is affected. |
| 14:51 BleepingComputer | Stop & Shop staff cannot see schedules and pay stubs. A memo shared by Food Lion staff calls it an IT outage. A group spokesperson pointed to the statement when asked about corporate against store systems, worldwide disruption and encryption. | Anything this briefing could check about the US reports. The memo and staff reports were not seen. |
| 15:24 NOS, Albert Heijn's chief executive | Work at some distribution centres is at a standstill. Albert Heijn has seven large ones, and its chief executive would not say which still work. Shelves may empty if it lasts. The chief executive cannot yet say whether intruders got in, and the investigation continues. | Which centres, for how long, and what the investigation has found. |
| About 16:54 NOS update, relaying Reuters | A group spokesperson told Reuters there is no reason to see a link between the French and Dutch incidents. | The grounds for that view. |
| 17:07 Help Net Security | Describes this and a French refrigeration attack as two separate disruptive attacks, and says there is no indication they are connected. Its own text calls the Dutch cause an unspecified security issue. | Any evidence about the cause of either. |
| 18:00 Albert Heijn's own outage page (last update) | Since Sunday afternoon a cybersecurity incident. Some systems switched off as a precaution. Websites, apps and customer service unavailable. Stores open and tills working. Online orders refunded. Personal discounts and savings schemes not working. | The hour of onset, the cause, whether data was taken, and when services return. |
| 18:51 Reuters, via The Globe and Mail | A message in the Albert Heijn app cites a cybersecurity incident. Online orders are about 10 per cent of Albert Heijn's sales (Reuters). US brand sites showed "site temporarily down". It was unclear whether other operations were affected. | Anything beyond the sites. This briefing could not load the US brand sites from a UK address. |
| 19:41 NOS (ANP) | Jumbo and Picnic report more online orders. The supermarket trade body says there is no reason to panic. The Dutch ministry for agriculture and food calls the situation worrying. Ahold Delhaize shares fell 2.8 per cent on the day while the AEX rose about 0.4 per cent. | How long Dutch shelves can be supplied. |
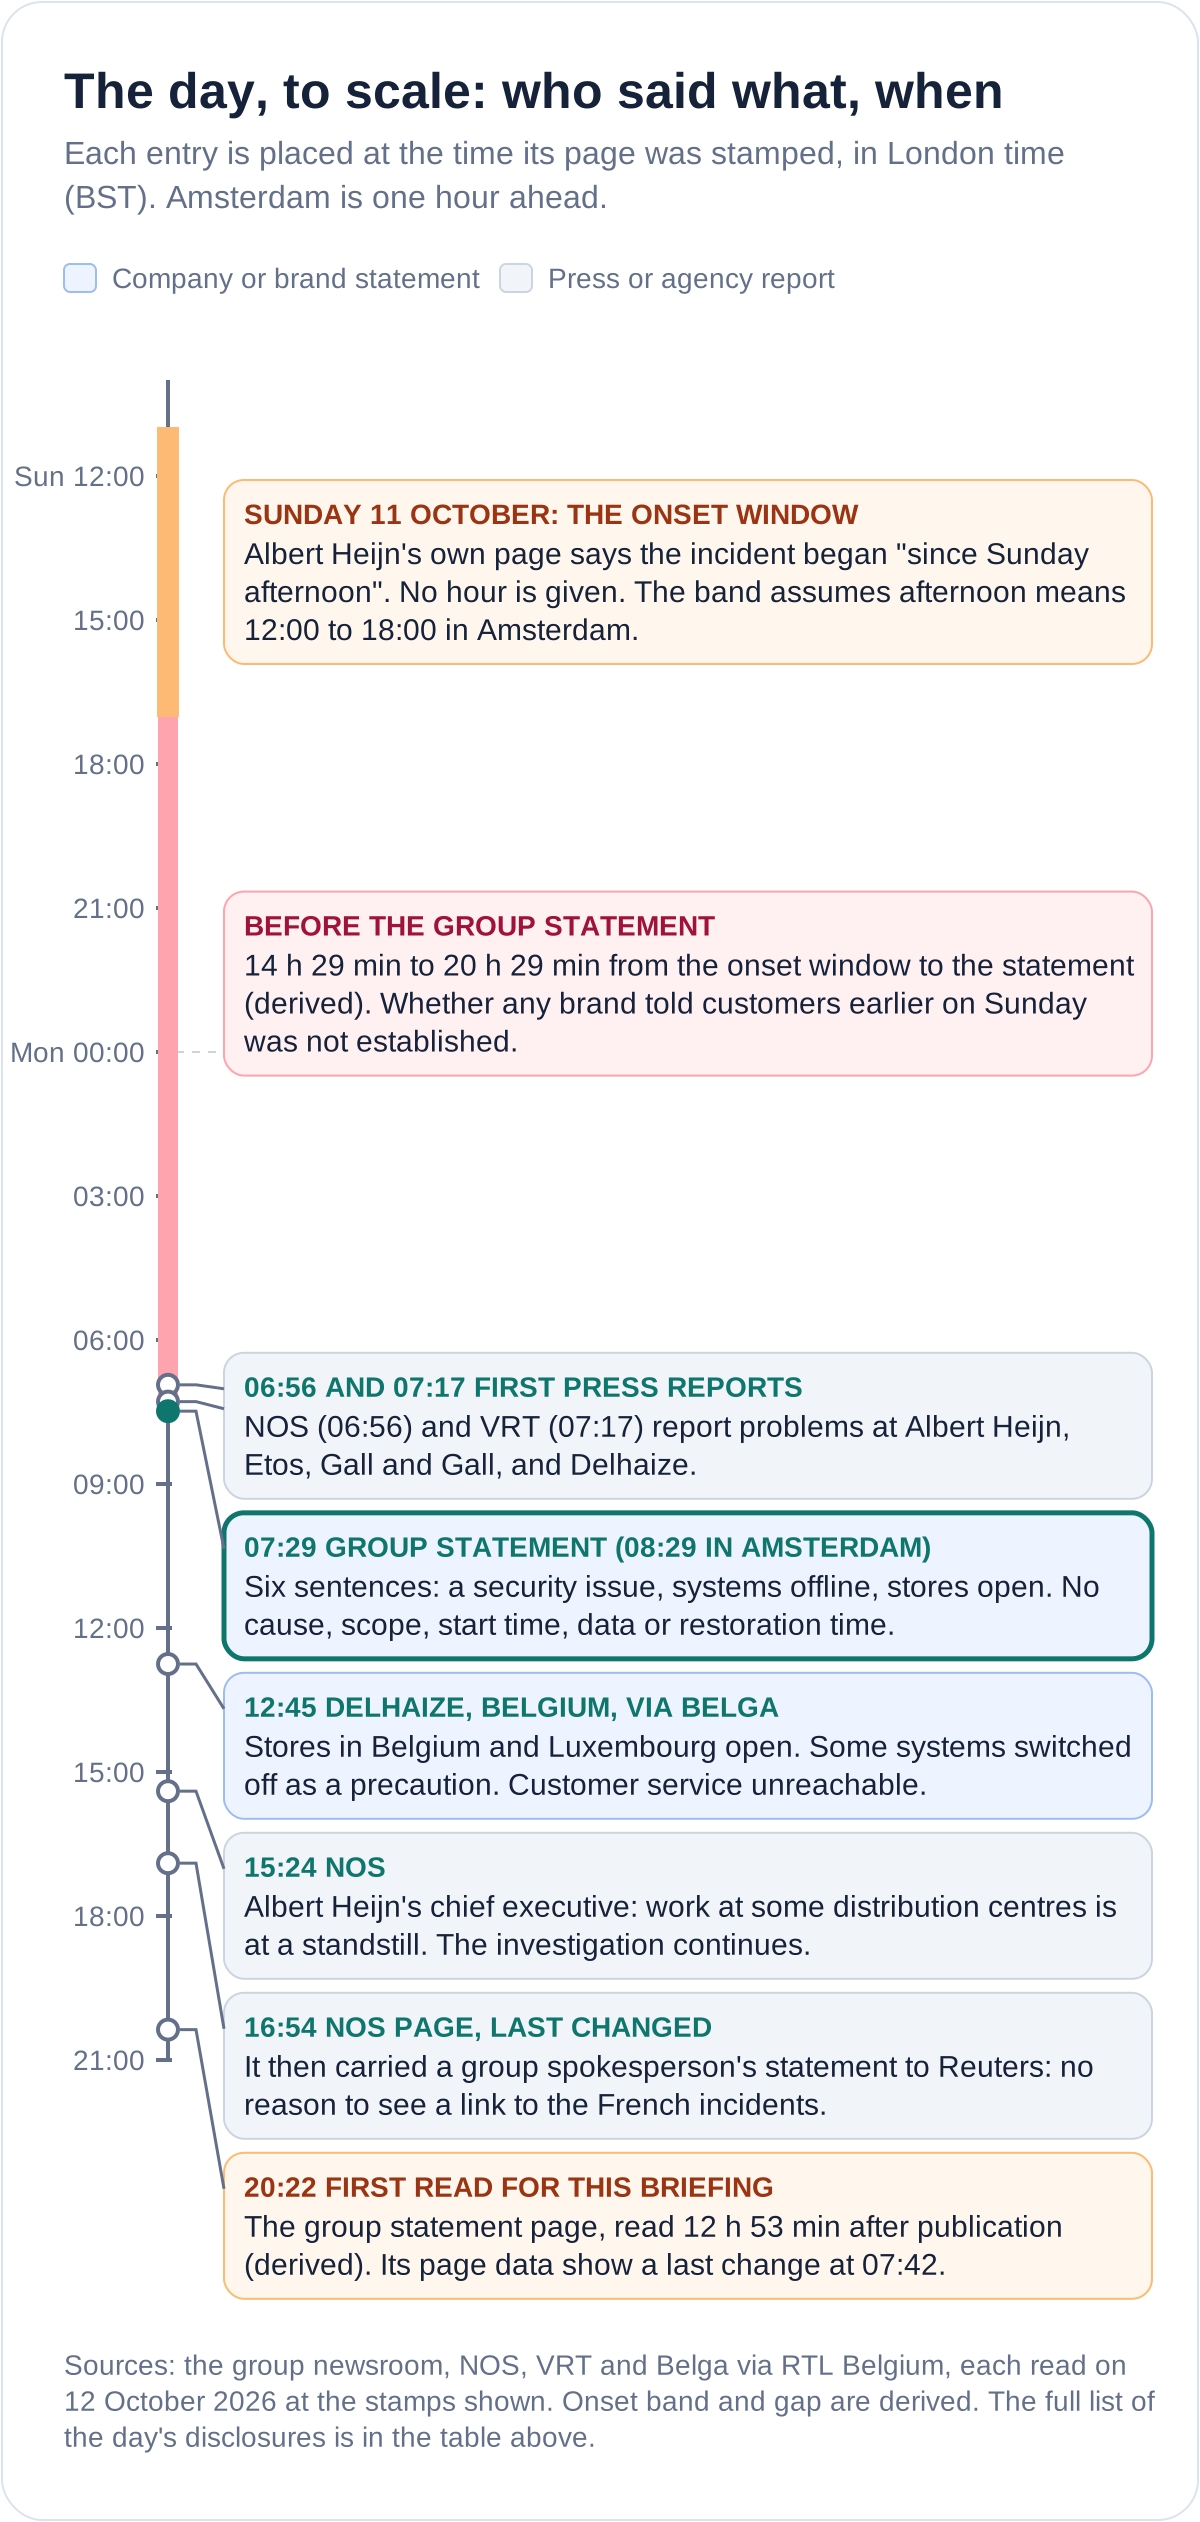
The diagram places the main items to scale. NOS published its first report at 06:56 BST, 33 minutes before the group statement, but its page was last changed at 10:38 BST, so the first version may not have carried every line seen now. The longer interval is the one before the statement. Taking Albert Heijn's "Sunday afternoon" as 12:00 to 18:00 in Amsterdam, the statement came 14 hours 29 minutes to 20 hours 29 minutes later (derived). Whether any brand told customers earlier on Sunday was not established, and the group's page gives no onset at all.
Stated and not stated: the record, question by question
"Not stated" means not found in the source named, or in any source read. It does not mean the information does not exist.
What the group, its brands and the press state on 12 October 2026, and what no source read states. Press reports are marked as such.
| The question | Stated, and by whom | Not stated |
|---|---|---|
| Cause | A "security issue" (group text) or a "cybersecurity incident" (group headline, Albert Heijn's page). Albert Heijn's chief executive told NOS the investigation continues and that it is not yet possible to say whether intruders got in. | Ransomware, intrusion, software fault, supplier failure or anything else. No source read states a cause. |
| Start | Albert Heijn's page, NOS and VRT: Sunday afternoon. | The hour. The group statement gives none. |
| Data | Albert Heijn and Delhaize both say protecting the data of customers, staff and partners is the priority. VRT says it is not clear whether customer data leaked. | Whether any data was accessed or taken. The group statement does not mention data. |
| Systems offline | "Some systems" (group). Websites, apps, customer service, logistics systems, loyalty and savings (Albert Heijn's page, DutchNews, NOS). Shelf labels showing last week's prices. | A list. Whether corporate IT, store systems and supply-chain systems are separate: a group spokesperson declined to answer that (BleepingComputer). |
| Brands and countries | Albert Heijn, Etos and Gall and Gall (Netherlands). Delhaize (Belgium, with stores in Belgium and Luxembourg open). US banner websites down (Reuters and Grocery Dive). Stop & Shop staff and a Food Lion memo (BleepingComputer, not seen). | Which countries the group counts as affected. The statement names no brand or country. |
| Stores and supply | Stores open and tills working (group, Albert Heijn's page). Work at a standstill in some of seven large Dutch distribution centres (NOS). | How many centres, which, and for how long. Whether other countries' supply chains are affected. |
| A claim of responsibility | None found in any source read. | Whether one exists elsewhere. This briefing did not look at criminal sites and does not link to them. A claim would be a claim, not a confirmation: see this site's [recount of claimed against confirmed ransomware attacks](https://www.pk-sharma.com/briefing/comparitech-q3-2026-ransomware-2627-claimed-247-confirmed). |
| Restoration | Albert Heijn, Delhaize and the US arm each say they cannot say when (Albert Heijn's page, VRT, Grocery Dive). | Any date. |
| Related to the 2024 incident | No source says so. | Any link. |
| Related to France | A group spokesperson sees no reason to link them (Reuters, via NOS). Help Net Security sees no indication of a link. | The basis for either view. |
| Market disclosure | The group statement says it contains inside information within Article 7(1) of the EU Market Abuse Regulation. | Any estimate of financial effect. |
The French incident is context only. This site's briefing on the French supermarket refrigeration attack sets out what the French retailers, the controller maker and the Paris prosecutor have said about refrigeration controllers in French stores. The Dutch reports concern IT, logistics and customer systems. The two are not shown to be related.
What suppliers are reportedly being told, and by whom
NL Times, relaying a report by the Dutch broadcaster RTL Z, says Albert Heijn asked suppliers by email to deliver only to the Zaandam centre and to agree a delivery slot in advance "so that we can keep the flow of goods manageable". NL Times also says only the Zaandam centre is still working. Neither point was read at source: the RTL Z report was not opened, and Albert Heijn's chief executive declined to tell NOS which centres operate. NL Times also quotes an Albert Heijn Instagram statement that product availability will vary by store, with shelf-stable goods "reasonably available". NOS carries the same message from Albert Heijn: shelf-stable products, bread and frozen products are expected to hold up better than fresh.
NOS also quotes a delivery driver who says all drivers were logged out of the delivery app at the same moment on Sunday and could not log back in. That is one anonymous account. It is consistent with systems being switched off, which Albert Heijn says it did, and it establishes nothing about the cause.
Six labels, no cause: what each name tells you
The group's wording, and the wording around it, uses six different names for what is reported as one outage, and two phrases that read as containment. A label that sounds like containment is not a control, and none of them says what happened.
Labels in the 12 October reports, where each appears and what the record shows.
| The label | Where it appears | What the record shows |
|---|---|---|
| "security issue" | The group statement's body text. | Names no cause. The page's own headline calls it a "cybersecurity incident". The 2024 statement used "cybersecurity issue" for an event the company's notices later describe as files obtained by an unauthorised third party. |
| "IT incident" | Albert Heijn's first release, as NOS and DutchNews report it. Belga uses the French equivalent for Delhaize. | Albert Heijn's page now says "cybersecurity incident". The label changed within the day, and the record still does not say what happened. |
| "IT outage" | A Food Lion memo, as BleepingComputer reports it. | An outage describes a failure. The memo was not seen, and whether this is a failure or an attack is not stated. |
| "technical problems" and "temporarily offline for maintenance" | A message in the Albert Heijn app (Cybernews). Etos's own site, read in a browser tab at about 20:27 BST. | Maintenance implies planned work. Whether Etos's page is the incident notice is not stated. |
| "taking some systems offline to help protect them" | The group statement, word for word from 2024. | Describes an action, not a result. NOS reports a result at the distribution centres: work stopped. Which systems and how many are not stated. |
| "stores are open and serving customers" | The group statement, qualified by "at this time". | True per NOS and Albert Heijn's page, and about doors. The chief executive says shelves will empty if the problem lasts. |
"Precautionary measures", the group's headline, describes intent. The chief executive's own words, as NOS reports them, are that systems had to be switched off, and the effect is on distribution. This site has seen the pattern before: in a Japanese rail group's ransomware notices, trains were reported unaffected while customer forms were unreadable and no restoration date was given. The statement that stores or trains are running is usually true. It answers a question the customer did not ask.
The November 2024 incident, as the company's own notices record it
The company's own pages on its 2024 US incident: its newsroom statements of 8 November 2024 and 17 April 2025, and its notice site and press release of 26 June 2025. Each is read in full.
| Date | What the company's own page says | What it does not say |
|---|---|---|
| 6 November 2024 | Notice of 26 June 2025: it "detected a cybersecurity issue involving unauthorized access to some of our internal U.S. business systems" on this date. An unauthorised third party obtained certain files from one internal US file repository between 5 and 6 November. | How access was gained. Whether any group was involved. |
| 8 November 2024, 22:00 Amsterdam | First statement: an issue in the US network, outside experts, law enforcement notified, some systems offline, pharmacies and some e-commerce affected, stores open. | Whether data had been taken. |
| 17 April 2025 | Update: "we believe certain files were taken" from some internal US systems. Law enforcement updated. Individuals to be notified. | How many people. Any group's name. |
| 26 June 2025, 16:30 US Eastern | Notice: names, contact details, dates of birth, government identification and bank account numbers, health and employment information, varying by person. Mostly current and former employees and their dependents and beneficiaries. Two years of credit monitoring. Access believed contained. No indication that customer payment or pharmacy systems were compromised. | A total number of individuals. No company page read states one. |
The count of 2,242,521 individuals, including 95,463 Maine residents, is reported by SecurityWeek and a Maine television station as figures from the company's filing with Maine's Attorney General. That filing page returned an authentication error to both a scripted fetch and a browser tab, so the count rests on press. BleepingComputer's 2025 report says over 2.2 million. BleepingComputer's 2026 report says a ransomware group stole the 2024 data. The company's notices read here name no group, and this briefing does not name one.
No source read says the 2024 incident and the 2026 one are related. The 2024 record does show how long facts took to follow a first statement. The facts arrived 162 days after detection, when the company said it believed files were taken, and 232 days after detection, in the notices (both derived). If this incident follows the same pattern, which is inference from one case, the answers to the open questions in the stated and not stated table will not arrive in a day.
The arithmetic, and what is deliberately not computed
Intervals and counts derived by this briefing from the page stamps and notice dates read on 12 October 2026. The arithmetic is in compute.py in the build folder.
| Interval or count | Value (derived) | Arithmetic and caveat |
|---|---|---|
| Group statement to this briefing's first read | 12 h 53 min | 07:29:37 BST to 20:22:45 BST on 12 October 2026. The page data give the publication time to the second. |
| Onset window to group statement | 14 h 29 min to 20 h 29 min | Albert Heijn says "Sunday afternoon". Taking that as 12:00 to 18:00 in Amsterdam, 08:29:37 on Monday minus 18:00 and 12:00 on Sunday. A different meaning of afternoon moves the range. |
| Sentences repeated from 8 November 2024 | 3 of 6 (50 per cent) | The statement body split into six sentences by this briefing. Two more are close variants, not verbatim. |
| 2024: detection to first statement | 2 days | 6 November to 8 November 2024. |
| 2024: detection to "files were taken" update | 162 days | 6 November 2024 to 17 April 2025. |
| 2024: detection to individual notices | 232 days | 6 November 2024 to 26 June 2025. |
| 2024 detection to 12 October 2026 | 705 days, or 23 months and 6 days | 6 November 2024 to 12 October 2026. The statements of 8 November 2024 and 12 October 2026 are 703 days apart. |
| Customers a week: BleepingComputer against the company | 60 million against 77 million, 17 million lower | BleepingComputer's 2026 paragraph matches the one it used in June 2025, which said over 9,400 stores, more than 393,000 people and about 60 million customers (read). The company's pages now say more. |
| Share of the 2024 population against the employee base | Not computed | No company page read states the 2024 total, and the press figure covers current and former employees, dependents, beneficiaries and others, while the 384,000 is current associates worldwide. The two are not comparable, so no ratio is given. |
The company's own figures on scale, read from its pages on 12 October 2026: its About page says 77 million customers each week, 9,551 local stores and 384,000+ associates. The CEO message in its Annual Report 2025 says "nearly 400,000 people and 17 brands that serve 77 million customers each week", and the report gives net sales of EUR 92.4 billion for 2025 against EUR 89.4 billion for 2024. The company reports in euros, and BleepingComputer's figure of over 104 billion dollars of 2024 sales was not found on the company's pages. Two other scale figures are press-sourced: Albert Heijn's share of Dutch grocery sales is about 38 per cent (NielsenIQ, via NOS), and online is about 10 per cent of Albert Heijn's sales (Reuters).
The UK: no designated food assets, what the NCSC and ICO say, and who is regulated
No source read says any UK business is affected. The group's 17 brands, as linked from its homepage, include no UK banner. UK exposure, if any, would run through suppliers, exporters, or shared service and software providers, and none has been reported.
The UK government's own position on food is in the National Protective Security Authority's page on critical national infrastructure, last updated 21 September 2026. It lists 13 sectors, names the Department for Environment, Food and Rural Affairs as lead department for food, and says "the food sector has no individual assets which are designated at CNI". It gives the reason as resilience from global sourcing, supply chain alternatives, and "commercial competition providing incentives for operators throughout the sector to step in if difficulties arise". On 12 October, NOS reported Jumbo and Picnic scaling up, and the Dutch trade body saying the market could absorb some of it but that it was early. That is the mechanism the NPSA describes (inference), at a stage too early to say whether it holds. With Albert Heijn at about 38 per cent of Dutch grocery sales, how long the others can cover is open.
The NCSC has written about retail incidents in terms that fit this one. After the UK retail incidents of 2025, its blog of 4 May 2025 said it was "not yet in a position to say if these attacks are linked", and its Annual Review 2025, published 14 October 2025, cites ransomware attacks on Marks & Spencer and the Co-op and "the sight of empty shelves". The same discipline applies here: no one has yet said whether a malicious actor was involved in the Dutch incident.
UK guidance and law read on 12 October 2026, with where each stops. Quotations are short and exact.
| UK instrument | What it says | Where it stops |
|---|---|---|
| NPSA, Critical National Infrastructure (updated 21 September 2026) | 13 CNI sectors. Food has no individual designated assets. Defra is lead department. | Says nothing about one retailer's IT. Does not mean food retail faces no other law. |
| NCSC statement (1 May 2025) and blog (4 May 2025) | On UK retail incidents: apply the ransomware guidance, deploy multi-factor authentication comprehensively, review helpdesk reset processes, watch privileged accounts. Not yet able to say whether the incidents were linked. | Written for UK retailers' own estates. Not about a European grocer's incident. |
| NCSC, Mitigating malware and ransomware attacks (version 3.0, reviewed 9 September 2021) | Plan for an attack. Keep playbooks and "contact details" available "if you do not have access to your computer systems". Exercise the plan, including how you would continue critical business services. Keep offline backups. | Nothing on a customer's or supplier's outage. |
| NCSC, Incident management (2019) | An incident response plan should link to disaster recovery, business continuity and crisis management plans. | Written for cyber security professionals and large organisations. |
| NCSC, Supply chain security guidance (reviewed 22 October 2025) | Twelve principles. Identify critical assets and any over-reliance on single suppliers, and build diversity and redundancy. Cyber Essentials as a baseline for suppliers. A right to audit. | About a supplier's security, not a customer's outage. Cyber Essentials is a baseline for a supplier's own controls, and the guidance read says nothing on a customer's portal. |
| ICO, personal data breach reporting and guide | Report a notifiable breach "within 72 hours" of becoming aware, where feasible, in phases if needed. A processor must tell the controller without undue delay. Loss of availability counts where it has a significant negative effect on individuals. The page notes the guidance is under review after the Data (Use and Access) Act 2025. | Personal data only. Says nothing about this incident or any UK duty arising from it. |
| NIS Regulations 2018, Schedule 2 | Ten subsectors: electricity, oil, gas, air transport, water transport, rail transport, road transport, healthcare, drinking water supply and distribution, and digital infrastructure. The word food does not appear. | Food retail is outside the essential-service regime. This is a statement about law, not about risk. |
A supplier to a European grocer that is a processor of the grocer's personal data should know its contract's breach clause. A UK business that has a notifiable breach of its own has 72 hours from awareness, and the NCSC's guidance on playbooks held off-system is the control that matters when the usual channels are the ones that failed. The NCSC's Annual Review also says most criminals are sector agnostic and pick victims they think are vulnerable to operational downtime. That is a general statement about ransomware and says nothing about this incident.
What a UK retailer, or a supplier to a European grocer, should ask now
These questions are for a supplier whose orders flow through a retailer's systems, or for a UK retailer whose suppliers also serve the affected group. They are best put in writing, and the answers are as useful when they are "we do not know yet" as when they are not.
Written questions for an affected customer or supplier, with the reason each matters and the UK source that supports asking.
| Ask | Why it matters | UK source |
|---|---|---|
| Which of our channels into your systems are suspended, which are safe, and who will tell us when that changes? | Portals, EDI links and shared credentials may be off or untrusted. An instruction that arrives by those channels cannot be checked by them. | NCSC: keep contact details available without access to your computers. |
| How will orders, price changes and delivery slots reach us while your systems are off, and in what form? | Albert Heijn's labels show last week's prices while tills charge this week's. A supplier working from the wrong price sheet gets disputes. | NCSC: plan how critical business services continue. |
| Who is the named person, with a phone number we already hold, who confirms any change to bank details, portals or delivery instructions? | Messages that use the incident are a standard lure. A call to a known number is the check. | NCSC: an internal and external communication strategy. |
| Do you hold or send personal data for us, or we for you, through these systems, and when will you tell us whether any was affected? | A processor must tell the controller without undue delay. The controller's 72 hours run from awareness. | ICO breach guide. |
| Which of our deliveries are being rejected, redirected or held, and who bears the cost of stock that cannot be received? | NL Times reports suppliers being asked to deliver only to one centre at agreed slots. Perishable stock is the exposure. | Contract terms, and your insurer. |
| When you restore, will you ask us to reset credentials or re-register, and how will we know the request is genuine? | Restoration is the moment a convincing fake request lands. | NCSC: act on the vendor's instruction through a verified channel. |
| For a UK retailer: which of our suppliers' stock flows through the affected group's systems, and what happens to our orders if it is diverted or withheld? | A supplier with a large customer in difficulty may favour or lose that customer. | NCSC supply chain: over-reliance on single suppliers. |
What to do, in the order worth doing
Every item below is a control that the NCSC or ICO already describes, and each is chosen because the incident's reported effects point at it. Nothing here needs the cause. Defender level only: nothing here depends on, or describes, how an attacker would act.
Take this with you
Retailer and supplier actions, in order
- Confirm out-of-band communications. Hold a phone number and a named person at each affected customer in a list kept outside the systems that may be down, and tell staff that instructions arriving only by email or portal are to be verified by phone.
- Isolate and verify supplier portals and EDI links. List every portal login, EDI or API link and shared mailbox that touches the affected group. Do not disconnect on your own if that breaks a contract duty. Ask in writing what is suspended and what is safe, and treat any order, shipping notice or remittance from those links that does not match expectation as unverified.
- Rotate credentials for a shared portal only when the vendor or customer instructs it, through a channel you have verified. Do not follow a reset link in an email. For your own accounts that reach the portal, check multi-factor authentication is on and that no login is shared.
- Watch for phishing that uses the incident: messages about delivery slots, re-registering on a new portal, changed bank details, refunds or compensation, or urgent price lists. Verify any change by calling a number you already hold.
- Set a manual fallback for ordering and pricing. Decide how an order is taken, confirmed and priced by phone, email or spreadsheet, who may approve it, which price list applies when shelf labels and tills disagree, and how it is reconciled afterwards. Set your own limits on perishable stock for depots that may not receive it.
- Keep a time-stamped log from the first hour: every instruction received, who gave it and by what channel; orders placed, changed or cancelled; loads delivered, refused or redirected; and every decision with the name of who took it. The log supports contract claims, insurers and, where personal data is involved, the ICO's 72-hour test.
- Check contracts and insurance: notification duties, payment terms and what happens to goods refused at a depot. Tell your insurer early.
- Check personal data. If you hold personal data for the affected group, or it holds yours, find the breach clause. A processor must tell the controller without undue delay, and a controller reports a notifiable breach to the ICO within 72 hours of becoming aware, where feasible. Nothing read says either applies here yet.
- Register your organisation's addresses with the NCSC's free Early Warning service, and report an incident of your own to the NCSC if you have one.
- Rehearse. Use the NCSC's Exercise in a Box to run a one-hour tabletop on the case that your largest customer's ordering systems are off for a week.
What could not be verified
- Cause, claim, data, onset hour, scope and restoration. Not stated in any source read. No claim of responsibility was found.
- US effects. The Stop & Shop staff reports and the Food Lion memo come from BleepingComputer and Help Net Security and were not seen. The US brand sites blocked access from a UK address, so Reuters's and Grocery Dive's reports that they were down were not checked.
- bol. Supermarket News lists bol among affected European sites. bol blocked scripted access and was not checked.
- Delhaize and Marketscreener. Delhaize's own site and Marketscreener refused scripted access. Delhaize's statements are read through Belga and VRT.
- Supplier email and Zaandam. Reported by NL Times citing RTL Z. RTL Z was not opened. NL Times also says RTL points to cybercriminals, and the signs are not described.
- The 2024 count of 2,242,521. The Maine filing could not be opened. The company's own pages give no total.
- Newspapers. NU.nl showed a consent gate and was not read. De Telegraaf answered scripted access with a block and only its headlines were seen. Tweakers, De Standaard and RTBF showed no article on this incident in the lists read.
- Time-stamped. Sources were read between 20:22 and 20:50 BST on 12 October 2026. A restoration notice, a claim or a regulator's statement could appear within hours.
The question that exposes the gap
If your largest customer's systems went dark on a Sunday afternoon, and its first statement arrived the next morning saying only that its stores were open, how would you know what to ship, at what price, to which depot, and whether the portal you log in to can be trusted?
Key facts
Sources
- PrimaryThe group's statement, headed 'Ahold Delhaize takes precautionary measures following cybersecurity incident', page data 12 October 2026 08:29:37 Amsterdam time, last modified 08:42:21: the six sentences, the inside-information notice, and no cause, scope, start or data. Read in fullAhold Delhaizeaccessed 2026-10-12
- PrimaryThe company's statement of 8 November 2024 at 22:00 Amsterdam time on its US incident: outside experts, law enforcement, the US network, pharmacies and e-commerce, and the three sentences repeated in 2026. Read in fullAhold Delhaizeaccessed 2026-10-12
- PrimaryThe company's update of 17 April 2025: it believes certain files were taken from some internal US systems and has updated law enforcement. Read in fullAhold Delhaizeaccessed 2026-10-12
- PrimaryThe group newsroom front page, re-read at 20:40 BST on 12 October 2026: one release on the incident, no later updateAhold Delhaizeaccessed 2026-10-12
- PrimaryAlbert Heijn's own outage page, 'Laatste update: 12 oktober 2026, 19:00 uur': since Sunday afternoon a cybersecurity incident, systems switched off as a precaution, no restoration date, refunds, shelf-label and loyalty effects. Read in Dutch and translated; the page answered with an error status as the outage pageAlbert Heijnaccessed 2026-10-12
- PrimaryThe company's notice site of 26 June 2025 with its FAQ and press release: detection on 6 November 2024, files obtained 5 to 6 November, data categories, access believed contained, no indication customer payment or pharmacy systems were compromised, mostly employees and dependentsAhold Delhaize USA Servicesaccessed 2026-10-12
- PrimaryThe consumer notice letter dated 26 June 2025 as filed with the Vermont Attorney General: the same dates and data categories as the notice site. It carries no total countOffice of the Vermont Attorney Generalaccessed 2026-10-12
- PrimaryThe company's About page: 77 million customers each week, 9,551 local stores, 384,000+ associatesAhold Delhaizeaccessed 2026-10-12
- PrimaryThe Annual Report 2025 digital edition: the CEO message line on nearly 400,000 people, 17 brands and 77 million customers each week, and net sales of EUR 92.4 billion (EUR 89.4 billion in 2024)Ahold Delhaizeaccessed 2026-10-12
- PrimaryNPSA, Critical National Infrastructure, last updated 21 September 2026: the 13 sectors, Defra as lead for food, and the statement that the food sector has no individual assets designated at CNINational Protective Security Authorityaccessed 2026-10-12
- PrimaryNCSC statement, 1 May 2025, on incidents impacting UK retailersNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC blog, 4 May 2025: recommendations for retailers, and not yet able to say whether the incidents were linkedNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC Annual Review 2025, published 14 October 2025: ransomware attacks on Marks & Spencer and the Co-op, empty shelves, and the sector-agnostic pointNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC guidance, version 3.0 reviewed 9 September 2021: plan for an attack, playbooks and contact details off-system, exercise, continue critical services, offline backupsNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC incident management collection, 2019: link the response plan to business continuity and crisis managementNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC supply chain security guidance, reviewed 22 October 2025: twelve principles, over-reliance on single suppliers, Cyber Essentials as a supplier baselineNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC supply chain principle II, establish control: identify over-reliance on single suppliers, build diversity and redundancy, and consider Cyber Essentials as the baseline for suppliersNational Cyber Security Centreaccessed 2026-10-12
- PrimaryNCSC Early Warning service: free alerts for UK organisations' addresses and domainsNational Cyber Security Centreaccessed 2026-10-12
- PrimaryICO breach reporting page: 72 hours where feasible, report early and update later, and the note that the guidance is under review after the Data (Use and Access) ActInformation Commissioner's Officeaccessed 2026-10-12
- PrimaryICO, Personal data breaches: a guide: the 72 hours, processors telling controllers without undue delay, and loss of availabilityInformation Commissioner's Officeaccessed 2026-10-12
- PrimaryNIS Regulations 2018, Schedule 2: ten subsectors, none of them foodlegislation.gov.ukaccessed 2026-10-12
- Reported byNOS, 12 October 2026 07:56 Amsterdam, updated 11:38: first report, Albert Heijn's statements, Delhaize via VRT, since Sunday afternoon. Read in Dutch and translatedNOSaccessed 2026-10-12
- Reported byNOS, 12 October 2026 16:24 Amsterdam, updated 17:54: Albert Heijn's chief executive on distribution centres at a standstill, seven large centres, the investigation, shelf prices, a delivery driver, and the group spokesperson's no-link statement to Reuters. Read in Dutch and translatedNOSaccessed 2026-10-12
- Reported byNOS, 12 October 2026 20:41 Amsterdam, updated 21:07: Jumbo and Picnic, the trade body, the 38 per cent share, the ministry's statement and the share move. Read in Dutch and translatedNOS (ANP)accessed 2026-10-12
- Reported byVRT, 12 October 2026 08:17 Amsterdam, updated 17:02: Albert Heijn and Delhaize statements, the Tilburg centre serving Belgium, Delhaize order slots, customer data unclear. Read in Dutch and translatedVRT NWSaccessed 2026-10-12
- Reported byBelga via RTL Belgium, 12 October 2026 13:45 Amsterdam: Delhaize's statement and spokesperson on internal systems, the distribution centre and order slots. Read in French and translatedRTL Belgium (Belga)accessed 2026-10-12
- Reported byDutchNews: Albert Heijn's first release calling it an IT incident, with the loyalty and shelf-label effectsDutchNewsaccessed 2026-10-12
- Reported byBleepingComputer, 12 October 2026 09:51 US Eastern, updated 13:33: the US effects, the Food Lion memo, the spokesperson who declined to say whether corporate and store systems were hit, and its scale paragraph. Read in a browser tabBleepingComputeraccessed 2026-10-12
- Reported byBleepingComputer, 27 June 2025: the over 2.2 million figure and the scale paragraph it reused in 2026BleepingComputeraccessed 2026-10-12
- Reported byHelp Net Security, 12 October 2026 16:07 UTC: two separate attacks, an unspecified security issue, no indication they are connectedHelp Net Securityaccessed 2026-10-12
- Reported byReuters text carried by The Globe and Mail, 12 October 2026 17:51 UTC: the app message, online at about 10 per cent of Albert Heijn sales, US sites showing site temporarily downThe Globe and Mail (Reuters)accessed 2026-10-12
- Reported byA syndicated copy of Reuters's 'Ahold says no reason to see link in French, Dutch cyber issues', stamped 22:06 IST on 12 October 2026Devdiscourse (Reuters)accessed 2026-10-12
- Reported byGrocery Dive, 12 October 2026: the five US banner websites down on Monday morning, and the US arm saying it has no further statement and no timelineGrocery Diveaccessed 2026-10-12
- Reported bySupermarket News, 12 October 2026: US and European sites reported down, including bol, which was not checkedSupermarket Newsaccessed 2026-10-12
- Reported byNL Times, 12 October 2026 18:40 Amsterdam: the supplier email and Zaandam point citing RTL Z, and Albert Heijn's Instagram statement. Used only for what it relays, flagged as not read at sourceNL Timesaccessed 2026-10-12
- Reported byCybernews, 12 October 2026 12:05 UTC: the app's technical-problems message and no stated cause or data finding. No claim of responsibility in the text. Read in a browser tabCybernewsaccessed 2026-10-12
- Reported bySecurityWeek, 30 June 2025: the 2,242,521 figure as told to Maine's Attorney General. The Maine filing itself could not be openedSecurityWeekaccessed 2026-10-12
- Reported byWABI, 27 June 2025: the 95,463 Maine residents figure from the filing, as reportedWABIaccessed 2026-10-12