Times Car confirms 6.6 million breached accounts, at most 1.65 times the 4 million members it announced in August
Park24 says a third party acquired information from about 6.6 million Times Car accounts, including driver's licence images. The company counts accounts, not people, and has not said when the intruder got in, how, or who they were.
By Parminder Kumar Sharma · · 12 min read
The breach count is larger than the membership
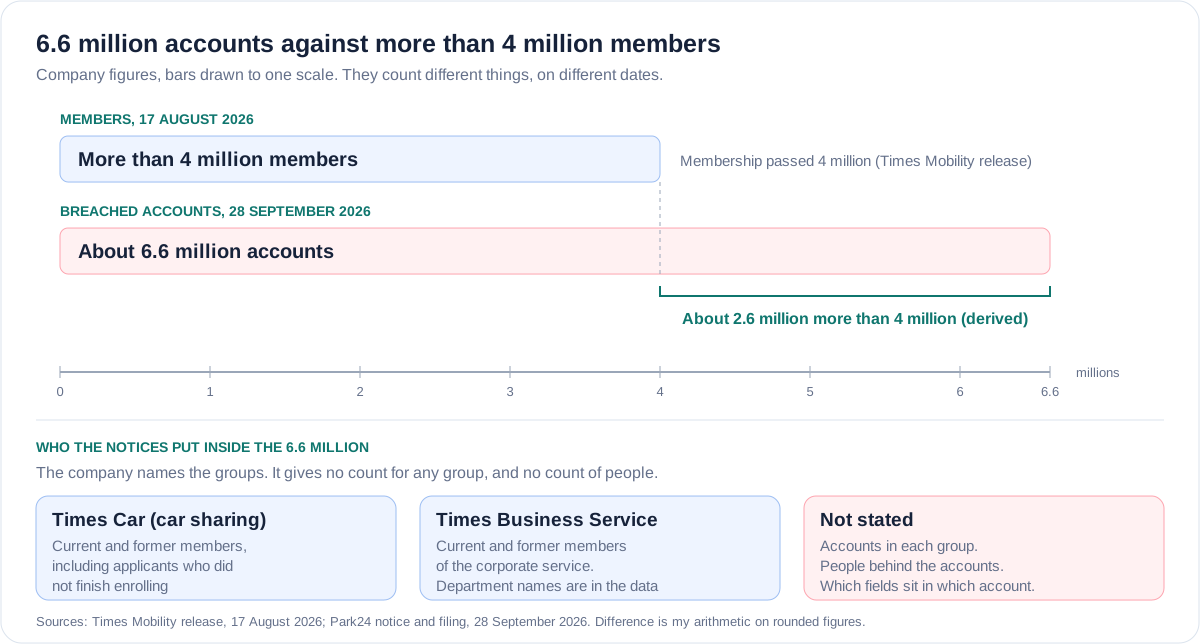
On 17 August 2026 Times Mobility announced that its car-sharing service in Japan, Times Car, had passed 4 million members. On 28 September its parent company, Park24, said that a third party had acquired information from about 6.6 million Times Car accounts. Divide the second number by the first and the answer is at most 1.65. That ratio is my own arithmetic on two rounded company figures, and the 4 million is a floor, so 1.65 is a ceiling, not a measurement.
The ratio shows that the breach total cannot be current members alone. It does not establish how many people are affected, because the company counts accounts and says they include former members, applicants who never completed enrolment, and members of its corporate service. It does not establish that every account lost every field, when the intruder first got in, how, who they were, or whether anything has been misused. On 28 September the company said it had found no misuse.
The company notices are in Japanese. Where I quote them I give my own translation and say so. Park24 also published an English version of its stock exchange filing of 28 September, and I quote that where marked. I read the Japanese and English filings against each other. BleepingComputer, which prompted this piece, is a secondary source: where it differs from the company, the company wins, and the differences are listed near the end.
What the company has stated, and what it has not
Three company documents carry the facts: a first notice on 25 September, a second notice on 28 September, and a filing to the Tokyo Stock Exchange the same day. The first notice came on the day the intrusion was detected. The count and the data list followed three days later. The table sets what the documents state against what they leave blank.
Park24 and Times Mobility notices of 25 and 28 September 2026 and the stock exchange filing of 28 September. Wording is my translation of the Japanese, checked against Park24's English filing.
| Item | Stated | Not stated |
|---|---|---|
| Detection | 09:07 on Friday 25 September 2026. | When the intruder first got in, or how. |
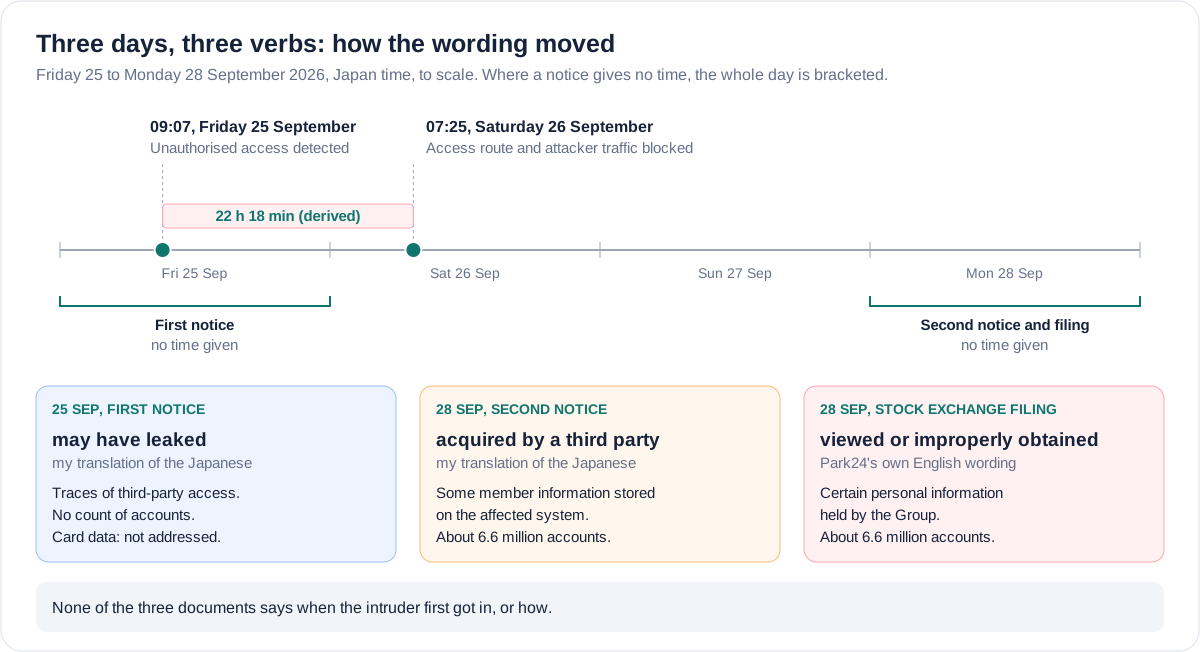
| Containment | Access route and attacker traffic blocked by 07:25 on 26 September, 22 hours 18 minutes after detection (derived). | What the route was. |
| Accounts | About 6.6 million: current and former Times Car members, unfinished applicants, current and former Times Business Service members. | How many people. The split between groups. |
| Data | Name, department (corporate members), address, birth date, phone, email, licence information, ID document information including licence images, password, IDs of linked services. It varies by person. | Which fields sit in which accounts. Which documents besides licences. |
| Passwords | Stored in a form that cannot be restored. | The method, or how many accounts it covers. |
| Card data | Confirmed not breached. | How that was confirmed. |
| Misuse | No publication or misuse confirmed as of 28 September. | What was checked to reach that conclusion. |
| Cause and attacker | Forensic investigation with an external specialist. Regulator and police told. | Cause, entry route, attacker, any claim of responsibility. |
The company says it will publish its prevention measures, with a timetable, in a further notice, and that it is still assessing the effect on its financial results. Both are open items, not findings.
Three verbs in one week
The wording moved. The first notice, on 25 September, said member information may have leaked and that there were traces of third-party access. It gave no count. The second notice, on 28 September, said a third party had acquired some of the member information stored on the affected system. The stock exchange filing the same day says the third party "viewed or improperly obtained" certain personal information, which is Park24's own English wording. "Acquired" and "obtained" describe taking. "Viewed or" widens the statement to include looking, and nothing in the documents says which applies to which accounts. By 29 September the front page of the Times Car site carried a banner saying a leak "has occurred", in my translation.
These are a listed company's disclosures, written for a regulator and a market as well as for members. Careful wording is what that produces. It is not evidence of bad faith, and I do not suggest it is. It does mean a reader should take each phrase at its narrowest.
One detail is easy to miss. The Times Car login page asks for a member number and a password. The first notice listed member number among the fields that might have leaked. The second notice's list does not include it, and does not say whether that is because it was not taken or because the list varies by person. Neither notice tells members to change their password. Times Car's own notice of 22 April 2026, about a separate attempt to log in to member pages, did tell members to change any password shared with another service. JR West, whose WESTER ID is one of the nine linked services, says its own password was not exposed and suggests a different password if the same one is used elsewhere.
Whose accounts, and how old
The count includes former members. Times Car's own FAQ says personal information is kept for about seven years after a member leaves, because of a legal duty to keep transaction records. It does not say that identity document images are kept that long, and the notices do not say what was still stored for people who left or never finished joining. That is the gap that matters, because a licence image cannot be changed the way a password can. We have made the general point before: Revolut stopped sending customer data to a provider up to 33 months ago, and the records were still there.
Times Business Service is described on its own site as a service for companies that manages parking and car-sharing use together. The data list includes the department name of corporate members. A department name is the kind of detail that would make a fake message about a company car or an expense charge believable. That is my inference, not something the company says.
A separate event came first. Times Car's notice of 22 April 2026 said it had seen attempts in March to log in to member pages, that it could not rule out access to some accounts, and that from 14 May it would add two-step verification for individual members viewing or changing registered details. It said that event was not an intrusion into its database or a leak. Nothing in the September notices links the two, or says whether two-step verification played any part. The April notice also says licence and card information is not shown on those pages, and the September data includes licence information and images. My inference, not the company's statement, is that the September data came from storage behind the site rather than from logging in to accounts one by one. The second notice's phrase, information "stored on the affected system", fits that reading.
What a UK reader should take from it
Start with scope, because the premise that this is a travel account is doubtful. Times Car is a car-sharing service, and its own FAQ says overseas driving licences and international driving permits are not accepted for membership. A visitor with a UK licence and an international permit hires through Times CAR RENTAL, a separate service with its own site, which carries the same company's copyright notice and whose English page describes hire against a passport and a permit. The September notices name the car-sharing web system and its members. They do not mention the rental service, and whether the two share any system is not stated.
Who might hold an affected account, from the company's FAQ pages and the notices of 25 and 28 September 2026. The middle column is what the record supports; the last is what it leaves open.
| Reader | What the record supports | What it does not establish |
|---|---|---|
| UK visitor who hired a car on a passport and permit | Car-share membership needs a Japanese licence. Rental is a separate service. | That the rental service is outside the incident. The notices do not mention it. |
| UK national living in Japan with a Japanese licence | Could hold a car-share account. Licence images are among the data. | That the account is one of the 6.6 million. Notices are going out in stages. |
| UK group with staff in Japan using Times Business Service | Corporate members and department names are in the data. | Which companies or how many staff. |
The notices name Japan's Personal Information Protection Commission and the police as the bodies told. They name no UK regulator, and they do not address whether UK data protection law applies to anyone UK-linked. I have not tried to decide that.
What to do, in order
Take this with you
Practical method for a reader who may be affected
- Work out whether you are in scope. Search your mail for Times Car and Times Business Service, and remember the company is writing to affected people in stages, so silence does not clear you.
- If you hold an account, change its password, and change any other account that shares it, to a unique password from a password manager. The company has not asked for this. It is a precaution against offline guessing and reuse.
- Treat a message that quotes your real name, address, birth date or phone number as unproven. All of those are in the data. JR West says the same about messages that quote a WESTER ID.
- Open Times Car through its app or a bookmark you already had, never through a link in a message. The company says it never asks for passwords or card details by email, text or phone.
- Do not type a password or an authentication code into a page reached from a message, and do not open attachments claiming to come from Times Car.
- If licence images were yours, expect identity-check pretexts for as long as the image exists, and refuse unsolicited requests to re-verify. The notices offer no remedy for the images.
- For a UK group with a Japanese office, ask that office whether staff use Times Business Service, warn them that department names are in the data, and log this as a supplier incident.
- Read the company's next notice for the cause, the prevention measures and the timetable it has promised, and revisit this list then.
Where the reports and the company differ
The company's own documents are the source for this piece. Where a report differs from them, I follow the company and say so.
BleepingComputer, 28 September 2026, and Response.jp, 29 September 2026, set against the company documents read for this piece.
| Report says | Company documents say | Handling here |
|---|---|---|
| The intruder accessed systems at the beginning of the month (BleepingComputer). | No first-access date in any document I read. Detection is 09:07 on 25 September. | Not repeated. Unverified. |
| 4 million active members as of August 2026 (BleepingComputer). | Times Mobility says membership passed 4 million. It does not say active. | This piece says members. |
| 84,000 vehicles (BleepingComputer). | The 17 August release says 68,000 vehicles and 29,000 stations. | Not used. I could not find 84,000 in company documents. |
| Passwords were encrypted or hashed (BleepingComputer's gloss). | Stored in a form that cannot be restored. No method named. | Encryption is reversible by design, so the wording points away from it. Method not stated. |
| No evidence the data was distributed online (BleepingComputer). | No confirmed fact of the data being made public to an unspecified audience. | Publication only. Silent on private holding or sale. |
| Student ID images are among the identity documents (Response.jp, citing newspapers). | Images of driver's licences, and similar. | Follows the company. Student ID unconfirmed. |
The question that matters
The company has said how many accounts, and what kinds of data. It has not said how many of those accounts belong to people who had left, or who never finished joining, or what was still stored for them. That is the number a regulator, an insurer and every affected member will want first, and the one the notices leave out. Which of the 6.6 million accounts belong to people who had left or never finished joining, and what was still stored for them?
Key facts
Sources
- PrimarySecond report on the Times Car web system intrusion, 28 September 2026 (Japanese), read in full: the count of about 6.6 million accounts, the groups, the data list, the password and card statements, the timingsPark24 Co., Ltd.accessed 2026-09-29
- PrimaryFirst report on the possible leak of personal information from the Times Car website, 25 September 2026 (Japanese), read in full: detection time, the possible-leak wording, the first data listPark24 Co., Ltd.accessed 2026-09-29
- PrimaryNotice Regarding Unauthorized Access at a Consolidated Subsidiary's System and Personal Data Breach, 28 September 2026 (the company's English version of its stock exchange filing), read in full: the viewed or improperly obtained wording and the password footnotePark24 Co., Ltd.accessed 2026-09-29
- PrimaryJapanese original of the 28 September 2026 stock exchange filing, read in full and compared with the English versionPark24 Co., Ltd. (TDnet)accessed 2026-09-29
- PrimaryRelease of 17 August 2026 (Japanese) saying Times Car membership passed 4 million, used for the membership figure and the growth historyTimes Mobility Co., Ltd.accessed 2026-09-29
- PrimaryTimes Car FAQ on international driving permits (Japanese): overseas licences and international permits are not accepted for membershipTimes Mobility Co., Ltd. (Times Car)accessed 2026-09-29
- PrimaryTimes Car FAQ on what happens to personal information after leaving (Japanese): kept about seven years because of a legal duty to keep transaction recordsTimes Mobility Co., Ltd. (Times Car)accessed 2026-09-29
- PrimaryTimes Car notice of 22 April 2026 on security strengthening (Japanese): the March login attempts, two-step verification from 14 May, the password adviceTimes Mobility Co., Ltd. (Times Car)accessed 2026-09-29
- PrimaryTimes Car front page as fetched on 29 September 2026 (Japanese): the banner saying a leak has occurred, and the login form asking for a member number and a passwordTimes Mobility Co., Ltd. (Times Car)accessed 2026-09-29
- PrimaryJR West notice of 25 September 2026 on the Times Car incident (Japanese): its own systems not accessed, WESTER password not exposed, advice on reused passwordsWest Japan Railway Company (WESTER)accessed 2026-09-29
- PrimaryTimes Business Service home page (Japanese), used for what the corporate service isTimes Mobility Co., Ltd. (Times Business Service)accessed 2026-09-29
- PrimaryTimes CAR RENTAL English page on driver's licences: a passport and an international driving permit are accepted for hire, a separate service from Times CarTimes Mobility Co., Ltd. (Times CAR RENTAL)accessed 2026-09-29
- Reported byTimes Car confirms data breach affecting 6.6 million user accounts, 28 September 2026, the pointer for this piece; used only for the points where it differs from the companyBleepingComputeraccessed 2026-09-29
- Reported byJapanese press digest of 29 September 2026 citing newspaper coverage, used only for the student ID images claim that the company notices do not makeResponse.jpaccessed 2026-09-29