Minor infringements generally get a reprimand. Anything else carries a strong presumption that a fine should be imposed. The guidelines are open to consultation until 13 November.
Roundcube has eleven entries in the CISA exploited catalogue, more than any other webmail. This one is not among them, four days after a national cyber centre warned about it.
The researcher agreed to hold publication until 17 September. He asked for an update twice and got no reply. He published on the 24th, with no CVE and no patch in existence.
A Google engineer wrote Nice catch and filed it. Eleven days later a panel called it working as intended. The case is still open at P1 and S1, and the researcher's page says it is still unpatched.
A watch on the root of C: reports filesystem events across every user, with filenames, regardless of permissions. That was enough to identify which of the top 1,000 sites another user was visiting, with an F1 score of 97.8 per cent.
The vulnerability was not a bug in the model. It was two safety controls that the shipped template did not have, and it took 112 days from report to the last fix.
ThreatDown recovered 4.3 GB from an unauthenticated registry, spanning October 2024 to August 2026. The interesting part is not the botnet. It is that the crew used somebody else's agent framework and only wrote the prompt.
Over a billion agent decisions in August, about 20,000 blocked, and roughly 100,000 transcripts flagged a week of which about 50 reach a human. Anthropic names the missing metric itself.
A defender triaging by the catalogue's own words would hunt for a file upload path. The flaw hands over an administrator session to anyone who signs a token with an algorithm the server never supported.
Cloudflare has fixed a cross tenant exposure in Containers and Sandboxes. The flag took six hours to change. Clearing the blocks already mapped took fifteen days.
September is the busiest month of 2026 in the Known Exploited Vulnerabilities catalogue, at 1.48 additions a day against a yearly mean of 0.89. The deadline never varies with how hard the change is.
Talos has not seen CLOSEDQUORUM work end to end, and says so. The public build is inert. What makes it worth reading is the architecture, not the threat.
Six of the seven fell inside seven minutes, which is not guessing. It is one provisioning default, used repeatedly, on accounts nobody had looked at in years.
The advisory for the WP Toolkit flaw describes database modifications in other accounts. The CVE record cPanel filed for the same flaw describes arbitrary file reads and arbitrary code execution across customer accounts.
CERT Polska has published the full MikroTrick chain. The interesting part is not the bug. It is how little time withholding the details actually bought anyone.
Reserved names exist so copied example code cannot reach a live host. Somebody used a real domain instead. Every outbound request to it is now both an exposure and, usefully, a near zero false positive detection.
A Terraform provider is a binary your CI runner executes with your cloud credentials. Two malicious ones are still on the public registry, and the badge on them is the same badge the real provider carries.
Yesterday the advisory gave defenders nothing to search for. Today there are request, response and file indicators, all of them from two firms selling protection. The vendor, the CISA KEV catalogue and the NVD record still say nothing happened.
The TrustSink technique does not extract passwords from Entra. It asks users for them a second time, on a full page a third party draws inside a trusted sign-in, and Entra validates only the token that comes back.
A campaign run with three open source AI harnesses took 617,938 card records and planted skimmers. Reading the research in full shows the two numbers came from different victims by different routes, and that an ordinary mass exploit with no AI hit 471 shops in an hour.
The Swedish regulator's sanction against Miljodata works out at roughly six pence per affected person. Reading the decision in full shows why that figure is real, why it is not evidence of leniency, and what it tells a UK board about budgeting security against expected fines.
Microsoft says it typically publishes definitions three times a day, and its device health report treats a signature build as current for seven days. A blocked machine can therefore sit about twenty releases behind and still read as protected.
The token inside a GitLab issue by email address does not expire, covers every project the account can reach, and is exempt from IP restrictions. Seven properties, six documentation pages, and one copy button.
Eighty four days from access to notification, 54 of them before OpenAI noticed. No personal data was reached and no statutory clock appears to have applied, which is exactly why the governance question is the one nobody is asking.
The only precise figure the fake Claude Max giveaway publishes is 92.5 per cent of slots gone, and it is generated in the visitor's browser. What the research does not establish matters more than what it does.
An agent is an AI system under Article 3(1), so the system duties attach. The strain is in Article 14 human oversight, the provider and deployer split, purpose-based classification and what Article 12 actually requires you to log.
Passkeys on GOV.UK One Login genuinely end credential phishing for the credential they protect. The published guidance also keeps a password and a one time code available on the same page, and lets that weaker pair delete the passkey.
The Gyazo breach is being read as an account leak. Gyazo indexes the text inside every capture, so the 490 million metadata records are a transcript of what was on people's screens, and the leaked image IDs are the only lock those images had.
The second WordPress core security release in five days fixes an unauthenticated path traversal that selects a PHP file to run, not to read. Two preconditions must hold, and the hardening constant that mattered last week does nothing here.
Two of the four new KEV entries name Check Point, but only one is the management server. The take that fixes the other is the top of the vulnerable range for it. What the four advisories do not state matters more than what they do.
Both Gen 6 parts state the same CPU clocks, the same 16 MB cache, the same 24 GB memory ceiling and the same 5300 MHz memory clock as the Gen 5 part they are measured against. The security block is identical on both, and shorter than Gen 5's.
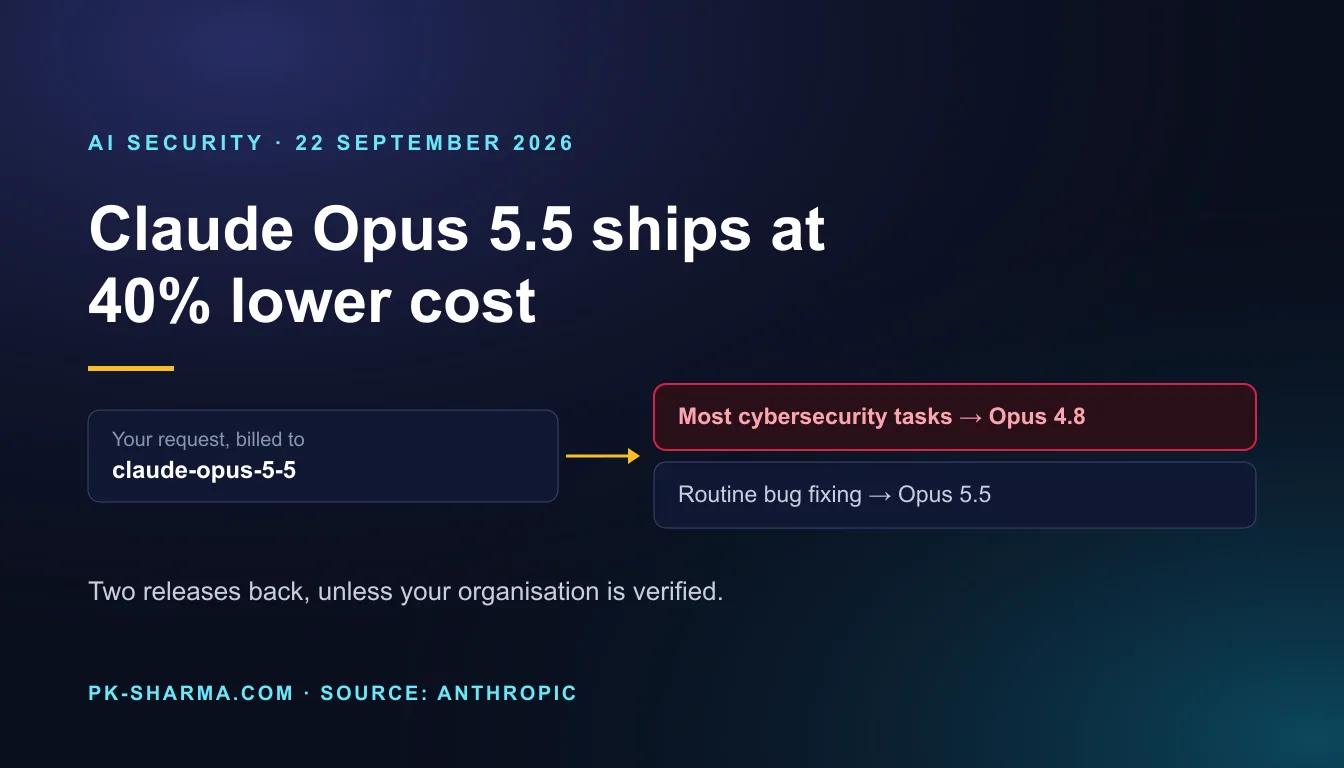
Opus 5.5 leads seven of the nine benchmarks Anthropic published and loses two to GPT-6 Astra. The row that matters most for security teams is not in the table: cyber tasks fall back to an older model.
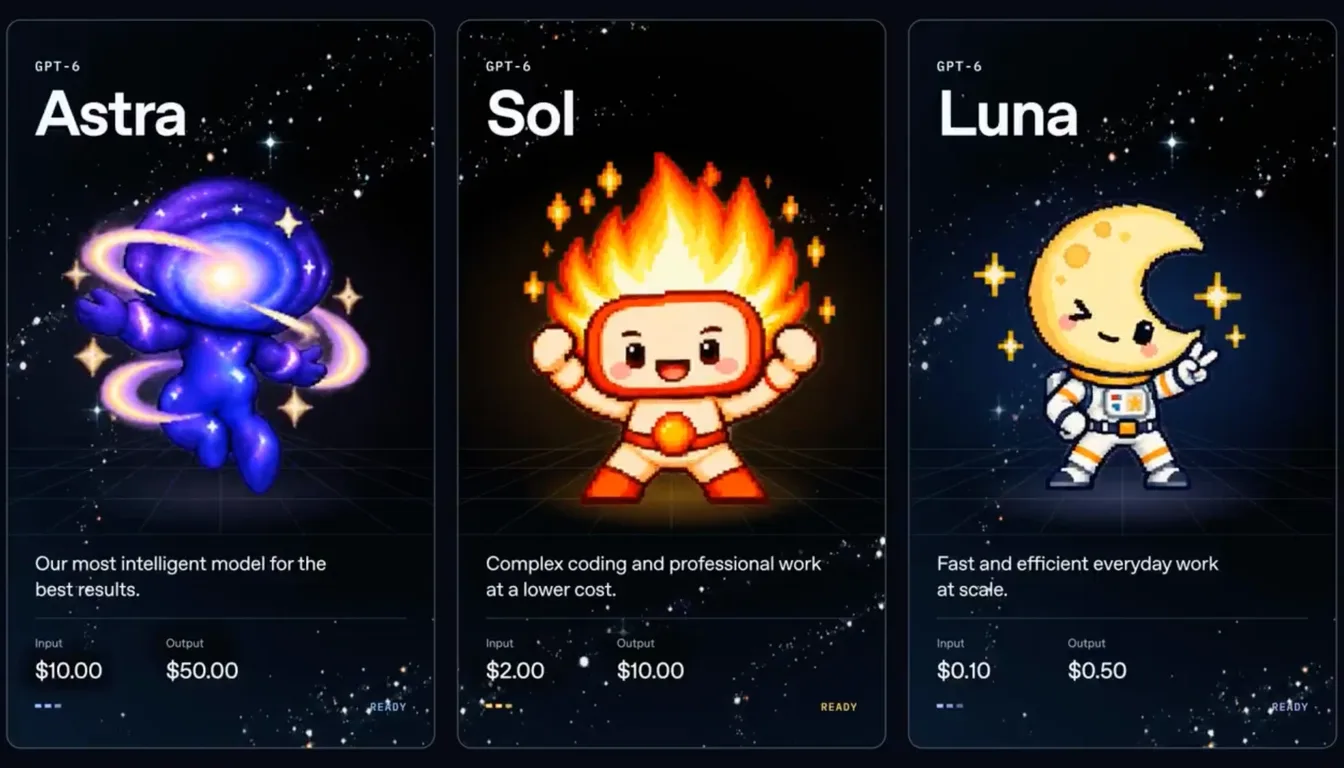
GPT-6 Sol is now $2 in and $10 out per million tokens, Luna $0.10 and $0.50. The charts behind the cut put OpenAI's own runs beside competitors' published reports, which OpenAI states in its own fine print.
A Spanish decision signed in February 2023 and published in September 2026 holds that every channel a controller offers for data rights must be easy to use, not just the best one.
The British AI cloud company's registration statement discloses customer, supplier and geographic concentration, conditional financing behind its largest contract, and two UK sites that are contracted but not yet active.