What Fortinet's announcement, change logs and policy establish about its hardening release: the 17 fixed versions, the 19 day gap, what the release notes list, and the upgrade steps to take before the advisories arrive.
What the Dutch police release states about the NFC card scan fraud, what it leaves out, the arithmetic behind 380,000 euros and 170 victims, where SecurityWeek differs from the primary, how NFC relay works at defender level, and a ranked checklist for customers and bank fraud teams.
What the honeypot report establishes about PHP2Shell exploitation and what it does not, the claims retracted before it, the fixed versions, defender detections as printed, and a ranked checklist.
What the Tailworm report, Tailscale, headscale and their repositories print about eleven claimed flaws: the chain at defender level, the dated record, the friendly names, the technical artifacts and a ranked checklist.
CISA's advisory ICSA-26-293-03 lists two Moxa AIG-302 flaws fixed in firmware 1.4.1: a shared hardcoded root CA private key (CVSS 4.0 8.6) and a missing authorization check (6.9). Adjacent network access is required.
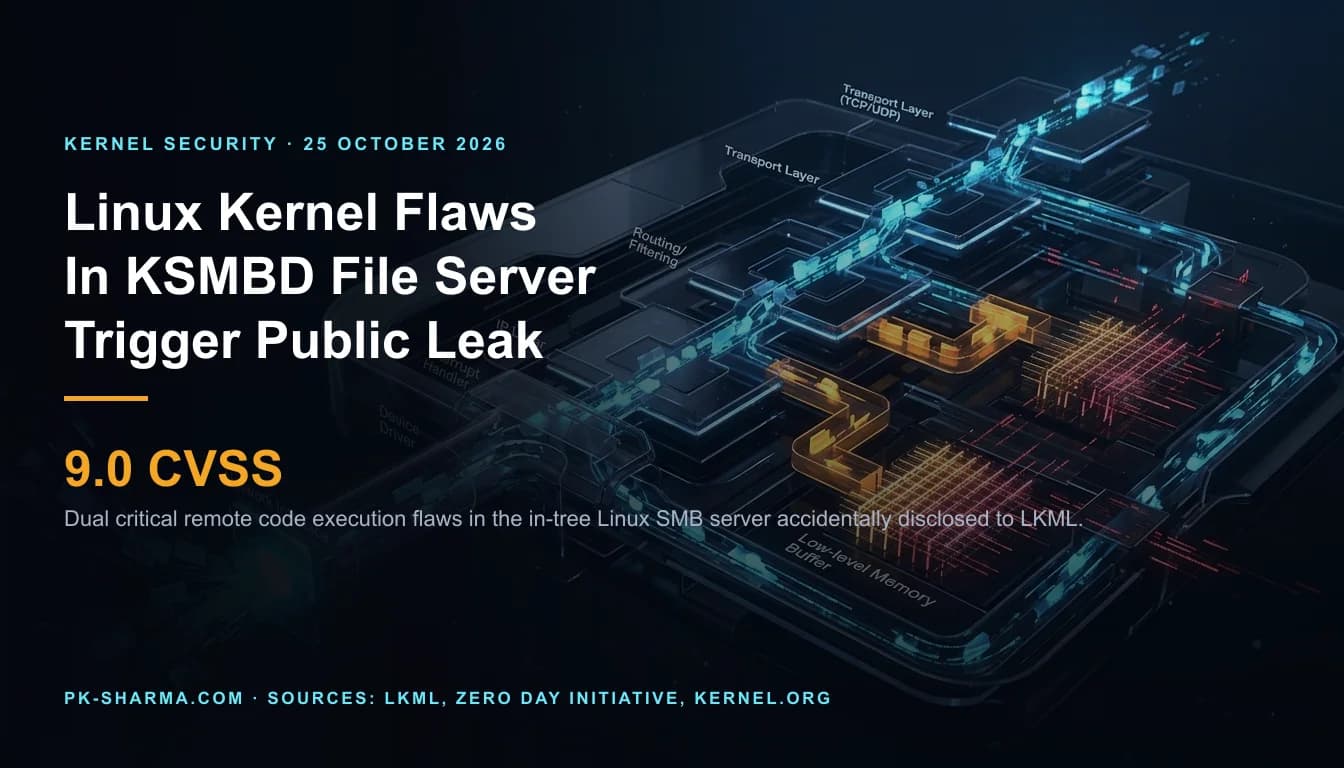
Dual CVSS 9.0 remote code execution vulnerabilities in the Linux kernel in-tree SMB server KSMBD leaked to public mailing lists, exposing hosts to pre-auth protocol confusion and heap memory corruption.
Cisco discloses CVE-2026-76466, a critical CVSS 9.8 remote code execution flaw in Expressway-C and Expressway-E clustered database services allowing unauthenticated root OS control with no workarounds.
What Eye Security reported at Hack.lu on 22 October 2026 about Operation IXIM: how it found the abandoned Time4Popcorn updater (CVE-2026-30612), what its update did and did not do, why a download count is not a device count, and what defenders should check.