Microsoft releases build 11.2609.401.0 fixing Paint RCE CVE-2026-83844, but Windows Update will not deliver it. Decoupled Store servicing, per-user AppX package isolation, and a 24-day catalog delay leave enterprise fleets unpatched.
OpenSSH sshole vulnerability (CVE-2026-123158) exploited in the wild within nine hours of disclosure. Honeypot telemetry confirms root compromises via 257-byte payloads as scanners execute automated discovery commands.
Layer3 Intel discloses 236 residential proxy exits originating from the White House network AS2650 across 26 of 30 days. Technical analysis of Infatica SDK bundling, diurnal evening clustering, attribution spoofing, and lateral movement risks.
Threat actors deploy CWPdoor, a passive Linux backdoor hidden inside Control Web Panel web servers across 340,000 exposed systems. Technical analysis of RSA-signed HTTP triggers, Unix socket IPC, in-memory log suppression, and Brazil telemetry.
CISA and the FBI issue an urgent advisory on industrial refrigeration cyberattacks. Analysis of 11-nation European retail spoilage, French blood bank tampering, DoD commissary investigations, and unpatched PLC defrost manipulation.
An architectural collision between OpenSSH, musl libc, and 1980s BSD shadow conventions allows attackers to log into locked accounts with a 257-byte password. The 46-year timeline, agent swarm discovery, cloud exposure, and OpenSSH's warning on AI bug discovery.
An APK requiring zero permissions and containing zero code plunges Android into an infinite crash loop. What Bitdefender found in wild banking samples, the ZIP parser gap in libandroidfw, the SIGBUS fault in system_server, Google's response, and what defenders must know.
Zyxel's own November table lists every June fixed release as affected by CVE-2026-107441. What Zyxel, Binarly, GreyNoise, the CVE records and CISA's KEV catalogue say, the dated gaps, what nobody has established, and a ranked checklist for GS1900 owners.
What ESET's report establishes about the SlippyNunchucks operation against Sogou Input Method users: the icon request, the forged DNS answer, the two files, the fix in 16.10, the China-aligned label, what is not stated, indicators and a ranked checklist.
What SonicWall's advisory and the CVE records state and leave out: no fix, no workaround, no exploitation recorded on 3 November, a score whose critical label rests on availability, and a checklist for anyone still running GMS.
What Sekoia's post of 4 November 2026 says about three routes, one profiling script and three exploit chains, the dates and the attribution, where BleepingComputer differs, a fix gap on iOS 16.7, the indicators it prints, and a ranked checklist.
What Google's bulletin states and leaves out: the two patch levels, 23 Critical rows counted from its tables, one Framework flaw rated most severe, no word on exploitation, and a checklist for what the date string on a phone does and does not tell you.
The 213 lines counted by severity, credit and bounty field, SecurityWeek's figures checked against Google's post, what the post does not state, and a ranked checklist for updating.
What the NCSC assessment, news release and annual review pages state about AI and ransomware on UK CNI: the yardstick ranges, all four key judgements, three scenarios that are not predictions, what is not stated, and a ranked checklist.
What Bitdefender's post on a 3AM attack against a UK school estate establishes about the three claims inside AI ransomware, the retry timing, the 10 to 19 September timeline, the conventional parts, the detection advice and the indicators it prints, and what it leaves unsaid.
What Kaspersky's Securelist post of 2 November 2026 says about CyberStrikeAI, the one incident's durations, the evidence for a model, the attribution clues, the indicators it prints, what it leaves out, and a ranked checklist.
What ESET's blog post and Virus Bulletin white paper establish about Gorbag, the chain from a macro spreadsheet to a WinRAR archive, the target split, the self removal, the initial access broker hypothesis, what is not stated, and a ranked checklist.
What Siemens, the CVE record, VulnCheck and the Node-RED documentation establish about CVE-2026-58115: one Siemens device on the record, a wider class in the post, what a canary sighting shows, and a ranked checklist.
What Absolute's two CVE records and its 14.61 advisory establish about CVE-2026-116769 and CVE-2026-97718, the four day gap between fix and record, the versions, what is not stated, and a ranked checklist for self hosted Secure Access operators.
What Google's XCPE post states and does not: the claim that the maker sold access, how the firmware backdoor works, what Google did, why certification did not stop it, the indicators as printed, and a ranked checklist.
What the three CWP CVE records, GitHub's advisories, VulnCheck and the vendor changelog state, where GitHub's wording differs from the CVE records, what 1.12 to 1.15 means, the dates, exploitation checks, and a ranked checklist.
What Barracuda's page, the CVE record, Mandiant's advisory file, NVD and CISA say about CVE-2026-116606, where they disagree on authentication, the companion command injection, the dates, what is not stated, and a ranked checklist.
What BTCPay Server's own posts and release notes state about the hot wallet thefts, the 85 day gap from the 2.4.2 fix to the first drain, what they leave out, and a ranked checklist for operators.
What Synology's warning of 29 October 2026 states and leaves out, the fixed DSM build per branch, what the three CVEs are, why the December 2024 date fits only DSM 6.2, what the public reports add, and a ranked checklist for NAS owners.
What Sophos's Aur0ra report establishes about AI agents doing the middle of a ransomware intrusion, how the operators talked past guardrails, what is not stated, the artifacts as printed, and a ranked checklist.
A CVSS 9.4 broken access control flaw in WSO2 API Manager, Open Banking and four other products reached the CVE list 280 days after WSO2's advisory. Who can reach the System REST APIs, what the Gateway sentence covers, the fix levels, and a ranked checklist.
CVE-2026-78403, CVSS 9.8: what the CVE record says about Thales Sentinel Keys Server, why owners may not know they run it, the 1.3.7.0 public bundle, a KEV check that predates the CVE, what is not stated, and a ranked checklist.
What the 15 pgAdmin CVE records establish: 13 score 7.0 or more, 14 need a login, most bite in server mode. How a backslash beat the Import/Export check twice, what 9.19 breaks on first start, and a ranked checklist.
CVE-2026-112816, CVSS 10: what Canonical's advisory and CVE record say about the leaf versus chain flaw in LXD and MicroCloud, who meets the two preconditions, the fixed snaps by channel, the Incus fix, what the score does not establish, and a ranked checklist.
What the researcher, Google's October bulletin and public fix commit, and the CVE Program show about the Android SMS of Death crash: which claims conflict, which versions are affected, what the fix changes, and a ranked checklist.
What Cisco Talos's VOLTA report establishes about a stealer that asks a model to rank victims, the three model chain, what is not stated, the artifacts as printed, and a ranked checklist for defenders.
Cloudflare says about 160 of 22,000 weak key handshakes stood out and none was interception, and that its 50 million probes show unpatched clients on large networks. What the post states, and what it leaves out.
What Cloudflare's DDoS Threat Report 2026 Q3 counts and compares: 18.2 million network layer attacks, the 208 and 38 percent changes, 251 giants against swarms, the takedown claim, and a ranked operator checklist.
What Microsoft's post of 30 October 2026 states about ESC1 in one intrusion and PetitPotam with ESC8 in the other, what the excluded account cost, what it leaves out, the queries it prints, and a ranked checklist.
What CISA's two Ivanti Connect Secure entries print, how they connect to the October chain, why one gets three days and the other fourteen, where Ivanti, MITRE and CISA disagree, and what the listing does not establish.
What Apple's support page and CyberScoop's quotation say about the 99 country batch, what neither states, why 110 and 99 cannot be added, what no notice does not mean, the helpline's limit, and a ranked checklist for recipients, at risk people and newsrooms.
What CrowdStrike's post of 29 October 2026 states about VAPOR PANDA, ARTEX, DeepSeek and BLOODALCHEMY, what each number counts, what it leaves out, the indicators it prints, and a ranked checklist.
What the Justice Department and Treasury releases state about the plea and the 11 designations, what only CyberScoop reports from court records, what neither release says about a link, the printed crypto addresses, and a ranked checklist for employers hiring remote staff.
What Cequence's post of 28 October 2026 measured, how it says it spotted the impostor, why a user agent proves nothing, a ranked checklist for site owners, and what the vendor does not say.
What Wordfence, WordPress and the 7.1.4 source files establish about the unauthenticated update race condition: the first match, the 18,500 requests, the fixed versions, why automatic updates are not a clean answer, and a ranked checklist.
The infection chain step by step, which parts were legitimate, the indicators as printed, what Kaspersky infers about a supply chain route, and what the report leaves open: delivery, country, scale and actor.
The CVE, the affected and fixed builds, what the attacker needs, the stand in behind Remedio's code execution demonstration, where the pages disagree, and a ranked checklist for help desks and managed service providers.
What the Talos Q3 post counts and does not, which claims sit only in Help Net Security's Q and A, which way the calls went, the controls named by Talos and Microsoft, and a ranked checklist.
What the Drupal advisory states and leaves out about CVE-2026-118539, the arithmetic behind 21 out of 25, the six advisories fixed in 3.3.13 and 8.x-2.41, the branch it does not name, and a ranked checklist for store owners.
What ASD is reported to have done to an Amadey controller, what the 180,000 may and may not count, how Amadey is rented out in 53 clusters, and what a defender should check. Read 29 October 2026.
What CISA's KEV entry for GitLab CVE-2026-97229 says and does not say, what BOD 26-04 changes against BOD 22-01, why the fixed version it points to is not the newest, and a ranked checklist with evidence first.
What the CVE record, Ubuntu, Red Hat, SUSE, Debian, Oracle and Amazon print for CVE-2026-98432: the bug, four distinct scores and the one letter that separates them, who has a fixed kernel, exploitation status, the artifacts and a ranked checklist.
What Check Point's Yoba report says about fake ChatGPT and Claude apps on GitHub: what the signature on the genuine file covers, the 85 seconds between the DLL build and the upload, what is not stated, hunting artifacts and a ranked checklist.
What the Justice Department release on the Virtualine seizure states and leaves out, the registry record, TRM Labs' one fifth figure and the dollar base it does not print, who said ransomware, and a ranked defender checklist.
What Palo Alto's PHP2Shell advisory now says about PAN-OS and Panorama, how its wording and score changed, the fixed hotfixes, the four conditions behind its signature mitigation, and what it leaves out.
What Cisco Talos's NIK C2 report establishes about the implant's OpenAI call, whose key pays, what is not stated, how it differs from Microsoft's SesameOp, the indicators as printed, and a ranked checklist.
What Talos's KeyDrift report establishes about PolyFlame, LittleFilch and the keys they target, what it leaves out, who links it to Volt Typhoon and how far, the CVE-2026-20127 record, and a ranked checklist with every path Talos prints.
What Cisco's advisory and data file state about CVE-2026-76418: the three conditions, the tunnel group checks, the fixed builds, the August flaw it follows, what is not stated, and a ranked checklist.
What CISA, Broadcom's CVE record and FAQ, and CrowdStrike state about CVE-2026-41709, the dates, what exploited and forensic triage mean in CISA's rules, the other four flaws in the advisory, the build traps, and a ranked checklist.
What ZDI's three advisories and its 27 October blog say about CVE-2026-35273, how the three bugs line up with Mandiant's account (our reading), what Oracle's alert leaves unsaid, dates with derived durations, and a ranked checklist.
The Edge chain, step by step from the researcher's own account: what ZDI paid, what Microsoft's notes and three CVE records show was fixed on 15 May, and what the public record does not say.
What the TianoCore advisory and CVE record state about the EDK II PXE network boot flaw, where the 16 year age comes from, who the sources say can send the packet, six stages of a fix, the maintainers' patch, and a ranked checklist. Defender level only.
What Lumen's report on Volt Typhoon's Silent Train framework states and leaves out, the five platforms and CVE ids checked against CVE.org and CISA, the ports and hunting advice it prints, and a ranked checklist for management platform owners.
Eight Adobe Campaign Classic CVE records, scored 9.1 to 10.0 by Adobe, and the ladder of 44 records and eight fix builds since June. What is stated, what is not, a ranked checklist.
What Dream's incident report states and leaves out: the 19,000 to 25 funnel, the PHP 8.0.30 branch, the unknown vendor, what was done inside one network, and how far the China and AI evidence goes.
What Oracle, CVE.org, NVD, CISA and Horizon3.ai state about CVE-2026-101767: affected versions, the 9.8 score, the 7 days from patch to a decoy hit, what is not stated, the 30 other unauthenticated fixes, and a ranked checklist.
What ANY.RUN's SkyW4lker report counts and does not, how the device code flow is abused, the Gabagool link, the Conditional Access setting that blocks it, and the indicators as printed.
What Microsoft's 26 October post and eight KB pages state about the eMudhra root removal, the Catalog only delivery, the gap between its six roots and the three the tracker lists, what the other root programs did and when, and a ranked checklist.
What CISA's KEV entry, the CVE record and Adobe's bulletin establish about CVE-2026-48356, where they disagree, what the entry leaves out, the 10 November federal deadline and the table behind it, and a ranked checklist with Sansec's published checks.
What the GoAhead 6.1.1 advisories establish about revoked client certificates and session decryption, the conditions each needs, the arithmetic of the one byte prime, what is not stated, the 71 day gap between device builders and publication, and a ranked checklist.
What Sansec's report on the Convertr analytics script establishes, what it leaves out, the arithmetic of the exposure window, the CVE that names a library, why the 953 stores story is a separate finding, the indicators, and ranked checklists.
What Wiz's post of 25 October 2026 and GitHub's own documentation establish about Gheist, a stolen token campaign. The hold covers public repositories only, so private ones are outside it. Indicators, audit log events and a ranked checklist.
What Apple's pages, the CVE record and CISA's KEV file establish about the CoreGraphics fix on iOS 18, how the 286 count is built, which devices have a fix and which have none listed, and a ranked checklist.
What Arctic Wolf's 26 October report counts and does not, the chain it describes, Microsoft's Teams external access settings by exact name, a conflict between two recommendations, hunting queries and a ranked checklist.
What CISA's catalogue entries, alert and directive state about the two PHP2Shell flaws, the clock from the fix to the 29 October due date, what the listing does not establish, and a ranked checklist for defenders.
What Microsoft's advisory, the CVE record and Enclave's research post state about CVE-2026-80097 in Microsoft Authenticator for Android: the fixed build, the score, the user step the two sources describe differently, what is not established, and a ranked checklist.
What Microsoft, PHP and the CVE record state about the Brotli decoder flaw on 26 October 2026: the scores and severity labels, the fixed .NET, PowerShell and PHP Windows versions, who coined HTTP2Shell, Node2Shell and Broccoli2Shell, and a ranked checklist.
What Kali's 2026.3 post states and leaves out: six tools listed only under the everything metapackage, a screenshot dated 24 September, images built 9 October, and how Kali says to verify a download.
What Fortinet's announcement, change logs and policy establish about its hardening release: the 17 fixed versions, the 19 day gap, what the release notes list, and the upgrade steps to take before the advisories arrive.
What the Dutch police release states about the NFC card scan fraud, what it leaves out, the arithmetic behind 380,000 euros and 170 victims, where SecurityWeek differs from the primary, how NFC relay works at defender level, and a ranked checklist for customers and bank fraud teams.
What the honeypot report establishes about PHP2Shell exploitation and what it does not, the claims retracted before it, the fixed versions, defender detections as printed, and a ranked checklist.
What the Tailworm report, Tailscale, headscale and their repositories print about eleven claimed flaws: the chain at defender level, the dated record, the friendly names, the technical artifacts and a ranked checklist.
CISA's advisory ICSA-26-293-03 lists two Moxa AIG-302 flaws fixed in firmware 1.4.1: a shared hardcoded root CA private key (CVSS 4.0 8.6) and a missing authorization check (6.9). Adjacent network access is required.
Dual CVSS 9.0 remote code execution vulnerabilities in the Linux kernel in-tree SMB server KSMBD leaked to public mailing lists, exposing hosts to pre-auth protocol confusion and heap memory corruption.
Cisco discloses CVE-2026-76466, a critical CVSS 9.8 remote code execution flaw in Expressway-C and Expressway-E clustered database services allowing unauthenticated root OS control with no workarounds.
What Eye Security reported at Hack.lu on 22 October 2026 about Operation IXIM: how it found the abandoned Time4Popcorn updater (CVE-2026-30612), what its update did and did not do, why a download count is not a device count, and what defenders should check.
What Kaspersky GReAT reports about BlackX, a UEFI bootkit that exploits Baton Drop (CVE-2022-21894) to install custom Machine Owner Keys on fully patched Windows machines, what it does not state, and which Microsoft revocation steps defenders have to run themselves.
What Microsoft says Storm-0940 did with the ARTEX AI framework after the ConnectWise Cloud Backup compromise: sign-in attempts to more than 2,250 tenants, a password spray that peaked at 2,900 failures a minute, and what is not established.
LiteLLM version 1.107.0 compromised on PyPI and Docker Hub via stolen GitHub CLI OAuth tokens, injecting a Python startup backdoor and credential stealer.
Group-IB and NyxLab expose threat actor k0t compromising Fortinet and Palo Alto firewalls to harvest 70,000 credentials feeding Qilin and The Gentlemen ransomware.
ESET's account of an intrusion at a Ukrainian grain logistics company: UAC-0099 initial access, a Go backdoor with its command server inside the Yggdrasil mesh, and a Sandworm wipe two months later.
What Huntress reported on 22 October 2026: a ten-week Microsoft 365 token-spraying campaign, at least 497 successful sign-ins at 79 organisations, rogue Entra devices, replaced MFA methods and hidden inbox rules, and what Huntress advises defenders to do.
What PHP's informational advisory on CVE-2026-115560 says and leaves out: the conditions it names, the one-line setting it suggests, the missing versions, severity score and release date, and what The Register, The Hacker News and Cloudflare add.
What Arista's CVE record and CISA's catalogue state about CVE-2026-114625: affected and fixed releases, the minimum role, the two earlier exploited VeloCloud Orchestrator flaws, and what the record leaves out.
What Mozilla, Google, Apple, CERT-In and eMudhra state about eight eMudhra intermediate CA keys below 256, what each has blocked, and what non-browser software must still update.
Technical analysis of Signal RingRTC CVE-2026-113380: FSM queue saturation, decoupling of UI dismissal from WebRTC audio hardware teardown, and the 2.72.0 fail-forward patch.
What INTERPOL's release says about Operation Serengeti III: 1,462 arrests, 10,909 disrupted networks, more than USD 105 million recovered, the cases it names in Uganda, Angola, Nigeria, Tanzania and Gabon, and what it does not state.
What the Securelist report on Operation FlashHole says about ML-KEM-1024 in LPEClient, the infection chain, victims and indicators, checked against the report, the Kaspersky release and NIST FIPS 203.
What PHP's advisory, the NCSC and CISA say about the PHP2Shell flaws: the four fixed releases, the stopgaps PHP prints, who is affected, and a corrected update checklist.
Two PHP 9.2 flaws can lead to unauthenticated code execution. The official advisories distinguish mod_php and FPM exploit evidence, fixed versions and interim controls.
The joint SafePay warning identifies at least 600 victims and two distinct access families. Here is how to test each exposure without treating the campaign as one fixed attack chain.
In Talos's samples, the sender passed checks while a fake support number appeared in shipping or billing fields. We trace that boundary, the 1,400-message denominator and two related notification routes.
The 333 measured SSH redirects, the 377 policy matches, the Ebury case on one operator's servers and the exact point at which a host-key warning matters.
Mozilla found eight recoverable eMudhra intermediate keys. Firefox blocked them; root distrust now puts about 30,000 certificates into migration, according to eMudhra.
What Siemens's advisory, blog and CVE records state about CVE-2026-110936, the four days before exploitation was noted, two scores, what Romulus is, what UK guidance reads, and a ranked defender checklist. Defender level only.
The labels on five NGINX flaws (nginx.org medium, F5 CVSS 4.0 critical for three), what each flaw needs, which press claims the records support, what the distribution trackers showed on 19 October, and the UK 5 day and 14 day clocks.
What Plex's release notes, the CVE records, CISA and the two researchers' pages establish about Plex2Shell as of 19 October: the dates to scale, four scores that miss the chain, the build that is actually fixed, what UK guidance requires, and a ranked checklist. Defender level only.
A computed diff of MITRE's version 19.2 and 20.0 STIX data: nine new Enterprise entries, six detection strategies, SecurityWeek's claims checked, the water and Mexico campaigns against their cited sources, how NCSC pages use ATT&CK, and a ranked checklist.
What the researcher's write-up, slides and project page state about the Broadcom WPS flaw, what Broadcom and the CVE records do not, the dated 90 days, and what the UK's PSTI regime, Telecoms Security Code and Cyber Essentials require and do not. Defender level only.
What the CVE record, the kernel changelogs and each distributor's own page say is fixed and where, why one flaw carries 9.3 and 8.8, what is and is not established about exposure and exploitation, the UK guidance as read, and a ranked checklist. Defender level only.
What Unit 42's report on CL-UNK-1211 states and does not, the AI claim rung by rung, the labels that carry it, the planted red-team markers, what NCSC guidance and Cyber Essentials cover and where they stop, and a ranked checklist. Defender level only.
The dates behind the BeyondTrust Remote Support zero-day, what the record does not establish (victims, Privileged Remote Access, the patch), nine labels read against the primaries, four UK clocks, and ordered checklists for a service desk, an MSP and a CISO. Defender level only.
How the fake yyay package used a valid source archive as cover, what the .install script changed, what is confirmed about removal, and practical checks for Arch users.
A precise before-and-after comparison, affected versions, NTLM event IDs 4024 and 4025, a scoped temporary exception and the migration path for Wi-Fi, Ethernet and VPN.
What happened, which Remote Support versions need BT26-05-RS, the observed SAWFLY and BARECLAW tradecraft, and where defenders should look when on-device logs have been erased.
What Symantec's report establishes about Aoki and AI assistant credentials, what it leaves out, the dated record, vendor statements on storage, lifetime and revocation, what UK guidance covers, and ordered checklists. Defender level only.
What Citizen Lab's AdFection report and Confiant's post establish, what they leave out, why the 45 devices and the 441,954,291 impressions cannot be divided, what the ad platforms said, what UK guidance covers and where it stops, and three ordered checklists. Defender level only.
What the Drupal Security Team's advisory and release notes state and do not state about CVE-2026-108097, the arithmetic behind 28.5 per cent, the May exploitation precedent, UK controls and where they stop, and a ranked checklist for three kinds of owner. Defender level only.
What Unit 42's PEERSTITCH report states and leaves out, the fix dates for four Fortinet flaws, why patching the FortiManager does not return stolen keys, what the NCSC, Cyber Essentials and the ICO say, and a ranked checklist. Defender level only.
What Palo Alto's advisory, CISA's entry and the NCSC's pages establish about CVE-2026-0322: a 3-day window against Cyber Essentials' 14, which PAN-OS builds are fixed, ten open questions, UK controls and an ordered checklist. Defender level only.
What the DOJ releases and the 58-page indictment state about the 40-plus Texas residences, the 14 charged, the $3 million and the 70-plus companies, where five news stories count differently, what UK law asks of an employer hiring remote developers, and an ordered checklist.
What the kernel commit, the CVE record and the vendor trackers establish about Vghost, what found by AI does and does not say, how seven raters score it from 6.4 to 8.8, which of 26 releases have a fix, the UK clocks and a ranked checklist. Defender level only.
The arithmetic behind curl's High flaw, what its advisory states and leaves out, where libcurl hides, what the distributions had fixed on 14 October, the UK patch clocks as read, and a ranked checklist. Defender level only.
What Cisco's 14 October advisory for CVE-2026-76519 states and leaves out, the two conditions and the scanner update that fixes it, the 16.0 gap, what Shadowserver's count can and cannot say, what NCSC, Cyber Essentials and the ICO say as read, and an ordered checklist. Defender level only.
What Microsoft's announcement, its sworn declarations and the court order actually count: 34 names moved, a billion messages with no stated method, 1.1 million dollars traced against tens of millions claimed, and what UK organisations should do.
What Adobe's 11 bulletin pages establish and do not, why 176 is 177 entries and 175 ids, how priority 2 and 3 compare with the Cyber Essentials and NCSC clocks, the Commerce hotfix beside a no exploits line, and a ranked checklist. Defender level only.
Which rule produces each outlet's total and Critical count, what zero-day did and did not mean, what Microsoft states about the exploited Windows Shell bug, why its risk cohorts omit it, and the UK clocks and an ordered checklist, and September's release set beside it.
What Wordfence's post establishes about a Ghostscript PDF flaw, where BleepingComputer's wording departs from it, what 0 of 10,240 does and does not say, which distributions have a fix, the UK patching clocks, and a ranked checklist. Defender level only.
What Ivanti, Volexity, NVD and CISA each state about the Connect Secure chain, the fixed builds and their dates, what the record does not establish, the UK clocks and duties, and an ordered checklist. Defender level only.
What SAP's 13 October overview and GitHub advisory state about the 10.0 OAuth2 SSRF in the Cloud SDK for Python, the 22 rows counted, who acts on each Critical row, the UK clocks to 27 October and an ordered checklist. Defender level only.
What Cisco's 14 advisories state and do not: the count by product and score, what a 'hardening release' is, five critical NX-OS flaws gated by features, fixed releases per train, the UK 14-day clock to 21 October, and an ordered checklist. Defender level only.
What Progress's bulletin, release notes and CVE records establish about 31 MarkLogic flaws, what they leave out, the arithmetic behind 32 days, the Cyber Essentials clock, UK guidance and an ordered checklist. Defender level only.
What Veeam's advisories establish about the Backup Viewer flaw and the Cloud Connect file read, what they leave out, the fixed build for each version line, the evidence on exploitation, what UK guidance and Cyber Essentials say, and a ranked checklist. Defender level only.
What Apache's bulletins, the CVE records and CISA's catalogue establish about CVE-2026-104711 and its three companions, the version-line matrix, the end-of-life dates, what they leave out, UK controls and a ranked checklist. Defender level only.
What Check Point's analysis of the Luna Moth Files establishes, what it leaves open, the arithmetic behind it, what the NCSC, Cyber Essentials v3.3 and the ICO say, and a ranked checklist for a group that steals data without encrypting it. Defender level only.
One CVSS metric separates 12 October's critical from the two regex criticals of 23 September: the attacker no longer needs an account. What GitLab states, what it leaves out, the count checked, CISA and the NVD at 14:52 BST, the UK 14 day clocks and an ordered checklist.
A computed gap, 149 days, from Palo Alto's advisory to ReliaQuest's warning; the fixed versions per train; four scores for one flaw; what no source establishes; UK controls; and an ordered checklist. Defender level only.
What SOCRadar's CyberXero report establishes, what it does not, the arithmetic behind 32 shells in 61 seconds and 564,073 of 628,000 records, the public fixes and CISA KEV status for the named CVEs, what the model's maker has said, UK controls, and a ranked checklist. Defender level only.
What the primary records establish about CVE-2026-85097: the first attempt, a fix date nobody publishes, three flaws in five weeks on one database's dates, a spray of 56 requests from 44 addresses, UK controls and an ordered checklist. Defender level only.
What Google's and Microsoft's own pages say about the default, which settings stop a calendar lure and which do not, the number behind "exponential", what no source establishes, UK reach of the NCSC and Cyber Essentials, and a ranked checklist. No lure is printed.
What Modat's pages, Reuters and others establish about 8,547 exposed wind and solar systems, the arithmetic behind the percentages, why the UK is outside the count, what the NIS Regulations and the NCSC say, and a ranked checklist. Nothing identifying a site is printed.
What the researchers' write-up and Chromium's own source establish about two characters that pass the browser's lookalike checks, what is not stated, why a list fails open for a letter or a brand it does not hold, UK controls and a ranked checklist. No lookalike domain is printed.
What iVerify, Google, Lookout, Censys, Report URI and Apple establish about P7 DarkSword: the six flaws and their fixes, which iPhones are exposed, what is not stated, UK controls and a ranked checklist. No indicators are printed.
What Push Security and BleepingComputer establish about the Adception campaign: the four stops, the cloaking gates, the swapped clipboard command, what is not stated, UK controls for Macs and a ranked checklist. No attacker addresses are printed.
What AnyDesk's changelogs, its post on X, the researchers' post, NVD, CVE.org and CISA's catalogue establish about the AnyDesk Linux flaw: dates, scope, the relay dispute, the UK timescales and a ranked checklist.
Recounting Comparitech's Q3 2026 ransomware record from its own tables: 247 of 2,627 confirmed, a Q2 that was a dip, 517 of the 597 extra claims from strains with no Q2 claims, and two other trackers that agree on direction and not size.
A computed gap, one build that two vendors described in opposite ways until the vendor changed its answer, and a backup console that MSPs expose to clients. What the record, Huntress and Ahsay state, what is not stated, UK clocks for MSPs and the order of actions.
Three NetScaler bulletins in 11 days, ten CVEs, and a new SAML flaw whose affected range ends at the previous fix build. What Citrix states and leaves out, the UK patching clocks and what to check.
OpenAI says it banned two influence operations that used ChatGPT and rates their reach Category 5 and 4 of 6. What the page states and omits, how Anthropic's reports compare, and what UK publishers and security teams can check.
What the 8 October seizure papers, the 58-page joint advisory and the NCSC's own item establish: two alleged breaches, six scan targets not said to be breached, 20 universities or six, and a UK checklist.
Of 83 CVEs in Splunk's five 7 October advisories, three Splunk Enterprise flaws score 9.0 or more. One is explained. Two are a weakness class and a score, and the October affected ranges end at August's fix builds.
What CrowdStrike's 7 October post establishes and what it leaves out: AI tooling from the actor's files, no named bank, no victim count, no Anthropic model named, a stack 3 to 63 days old, and a UK checklist.
What Talos's 8 October post on UAT-11985 establishes and what it leaves out: three emails behind the AI-assisted label, a relay that forwards typed codes and taps, no victim count, and what UK organisations on Google can do.
What the 14 AI credits establish and do not, SecurityWeek's figures checked against the notes, how 247 compares with earlier Chrome releases, the bounty column, and a UK checklist.
The build that fixed September's exploited SMA1000 flaws is still affected by the 6 October 10.0 flaw. Both earlier advisories that reported exploitation reached CISA's catalogue within a day, and this one is not listed in the version read, which predates it.
Lumen's report on the PoeLLM botnet gives its victim count as more than 3,400 in one place and almost 2,200 in two others. The poem hides a command address; the doors are exposed AI services and a LiteLLM flaw that had a fix for 177 days.
What the 10.6 notes state about AI-found reports and release cadence, the 11 CVE records and who scored them, the ML-DSA signature versus key exchange, Debian, Ubuntu and Red Hat status, and a UK checklist in the order worth doing.
Patchstack recorded the first attempt on Ninja Forms CVE-2026-94504 on 5 October, 14 days after the 3.15.4 fix. The campaign leaves four ways back in, only one visible in the dashboard, and two figures in circulation, 600,000 and 3,600, belong to other things.
FBI and USSS advisory JCSA-20261006-01: no CVE, a count credited to SOCRadar (30,791 on 17 June, 86,644 a day later), lockouts and ransomware reporting without numbers. What it does not establish, the UK position, and a checklist.
The window is drawn, the address bar is copied and a typed code is relayed live. Island reports hundreds of submissions, but states no victim count, loss, operator or UK reach.
Reports rose 34 per cent but victims reporting a loss rose 10.3 times, and no document says how the accounts were taken. A passkey closes one door; recovery and fallback sign-in are others.
The LibreOffice fix shipped on 24 July and the advisory on 5 October. OpenOffice still has no released fix and a public proof of concept has existed since 5 October. What each project documents, and what to do first.
Eight Atlassian Data Center products, 19 fixed builds, a 9.3 that computes to 8.7 without its downstream assumptions, and a CVE record whose Crowd and Bamboo builds disagree with the bulletin. What the sources state, and what they do not.
Divide Treasury's headline loss by its own attack count and the average is at most about $27,000. The DOJ, FBI and ATM makers all put the real control at the cabinet door, the keys, the alarm response and the disk, not at the arrest.
At least 476 days between the CVE record and the incident, three AnyDesk download attempts, eight days between two reports on one endpoint. What Huntress states, what it does not, and the order of checks for signage servers.
A Linux botnet dresses its command traffic as STUN, the NAT-traversal protocol behind video calls, but it gets in through flaws first recorded between 2015 and 2026. The disguise is the news; the doors are the part a UK security lead can still control.
The lead flaw is scored Network with no privileges, so it is not a local escalation by Dell's own scoring, but all five need user interaction Dell never explains. One fix, no workaround, nothing on exploitation.
Google's accessibility restriction needs three things at once: Android 17, Advanced Protection switched on, and an app that is not a verified accessibility tool. Only the first has a published figure, and it is a third party's estimate.
A research technique, not an exploited flaw: what the write-up states, how Kettle's 2020 paper named the same bug class, what five vendors' documents say about how keys are joined, and a UK checklist for cached personalised pages.
The first September update is listed as affected, one of nine CVEs is rated Exploitation More Likely, and the cloud fix has no date. What the record states, what it leaves out, and a UK checklist.
A third NetScaler flaw in seven days, scored 8.7 against 9.5 for the first two. What the record states, what it leaves out, why denial of service is not the mild category on a gateway, and where the word patched stops being true.
The SConnect token middleware was fixed in the browser stores on 7 August and given a CVE on 1 October. SWIFT's notice says the extension updates itself but the desktop host does not. CISA's coordinator recorded no exploitation on 2 October.
The advisory page for BoKS CVE-2026-79901 names no affected version and no fix. The CVE record names both, says the update leaves existing AD service-account passwords unsafe, and gives no 8.1 fix. What is stated, what is not, and what UK teams should do.
Rapid7's 2 October report lists 12 hashes for Linux implants that imitate Korean and Taiwanese mail security appliances, with a payload file that exists for ten seconds. Entry route, victims, first-seen dates and UK exposure are not stated.
A fake Zoom disk image runs its backdoor on a password the victim types. Jamf names no vulnerability, victim, actor or delivery route, and never saw the cloudsyncd daemon in use.
The headline speed claim cannot be checked from the report. Its other pages give 5.3 hours, single-digit days, about five days and 30 to 60 days for other clocks, and CISA's catalogue gives a median of 3 days for new flaws, 1 day lately.
The fix is 80 days old, six CVEs shipped with it, CISA's catalogue does not list the flaw, and the exploitation evidence is one firm's sensors. What the record establishes, what it leaves open, and what UK teams running HFS should do.
By Talos’s intervals one Antino implant makes about 10,080 Graph requests a day, to hostnames enterprises commonly allow. What the report states, what it leaves out, and which controls fit a channel whose mailbox the actor owns.
Warlock's latest victims include a water utility and a telecom provider. The report names only the 2025 ToolShell flaws, so a build number and a hunt for stolen machine keys matter more than any CVE list.
The two 10.0 flaws are unauthenticated and sit in CSM Authorization, the proxy that holds the array credentials. Root on nodes is a different 9.9 in the operator. Dell names one fix, 1.18.0, and says nothing on exploitation.
No FortiMail build named in the advisory's four branches is fixed on the page as read on 3 October. Fortinet's own records disagree on which builds are affected, and the advisory page lost its file indicators without a revision note.
All three attacker sender addresses in Proofpoint's July list are consumer webmail. A reading of its 1 October report on TA419: what it states, what it leaves out, why MFA and DMARC miss the chain, and an ordered checklist for UK organisations.
The alert is one page and about 470 words. It asserts the funding chain at both ends, says nothing about what UK work gave China's MSS, and asks institutions to establish a funder that NPSA's own collaboration checklist never asks about.
Eight files, a database row, a shared-memory segment and scheduled tasks: eleven places in Sucuri's own account of a WordPress backdoor that returns within seconds. What the report states, what it leaves out, and the order to clear it.
One signed MSP360 installer, five example filenames, a second remote tool, and 60 to 90 days between Microsoft's July sightings and its post. The signer was real; whether you approved it is the control.
Five flaws, one fixed build, zero days between release and bulletin. A client updated in August is still listed as affected, and for UK organisations the Cyber Essentials 14-day clock on these fixes ends on 13 October.
Six vendor reports describe four disguises for a NetScaler web shell, and LevelBlue's is the newest. What it states, what it leaves out, why one vendor's file names will not find another's, and what an update does not do.
From mid-October 2026 the Entra sign-in page will run only Microsoft scripts. Users can still sign in, so a failing tool raises no outage, and Microsoft describes no tenant report. The policy also guards one page only.
A public CoreGraphics crash test is not proof of exploitation, and the WhatsApp path rests on a line the researchers removed. CISA had already moved to active a day earlier. What UK teams should do about iPhones and Macs.
The dates, the score and the versions checked against Zimbra, NVD, CISA and Microsoft. What a patch does not remove from a hit mail server, the one victim count that exists, and a defender checklist.
CVE-2026-84411 is new, scored 9.8 and not reported exploited. CISA now names 7.24 as the fix, above the newest long-term build 7.23.7, and MikroTik has published no advisory.
CISA set a federal deadline of Saturday 3 October. What Cisco states and does not, the fix table set against its May one, four names for one flaw, what the UK record says, and a defender checklist.
What the Truffle Security count establishes, what its dates probably mean, and the gap it names itself: GitHub can block some secrets at push time, but only the issuer can make a leaked key stop working.
A count of Microsoft's own timeline, an invitation with nothing to scan, and six labels that reassure without controlling anything: what the RedFlick report establishes about Star Blizzard, and what it leaves open.
VUSec and Sant'Anna's Branch Target Reuse attack read a root hash at 8 bytes per second on two Intel chips. Stale predictor entries were reusable on AMD and Arm too, but nothing leaked there. The kernel fix dates from July.
Mandiant, eSentire and GreyNoise now date NetScaler exploitation to before the 27 September bulletin. What Mandiant observed and what it did not, how the exploited pair compares with briefing 143, and what to hunt and harden.
A DTLS retransmission bug can send OpenSSL heap memory to the other side or crash the process. Fixes are public for four branches, premium-only for three and absent for 3.1 to 3.3. No exploitation is reported and no leak size is stated.
A confirmed share of at most 5 per cent, four comforting labels and one command the person ran themselves: what Huntress's 28 September report establishes about custom GPTs used as ClickFix lures, and what it leaves open.
Apple's exploitation notice for CVE-2026-86950 is one 29-word sentence about iOS, repeated on both macOS advisories. Older iOS and macOS lines have no listed fix, and Lockdown Mode cannot be set by MDM.
Microsoft's earliest dated NeedyMantis sample was first seen on 3 October 2025, 187 days before DAEMON Tools installers were trojanised. The malware hard-codes a Firefox 21 user agent, a browser released in May 2013.
Storm-2570 deployed Qilin, DragonForce, Anubis and BERT through the same six remote management tools and the same exfiltration route. The brand on the ransom note is the part that changes.
A store takedown is a distribution control, not remediation. CERT Polska's toll fraud analysis shows the billing server outliving the Google Play removal, and why a UK premium rate bar may not cover the route this operation used.
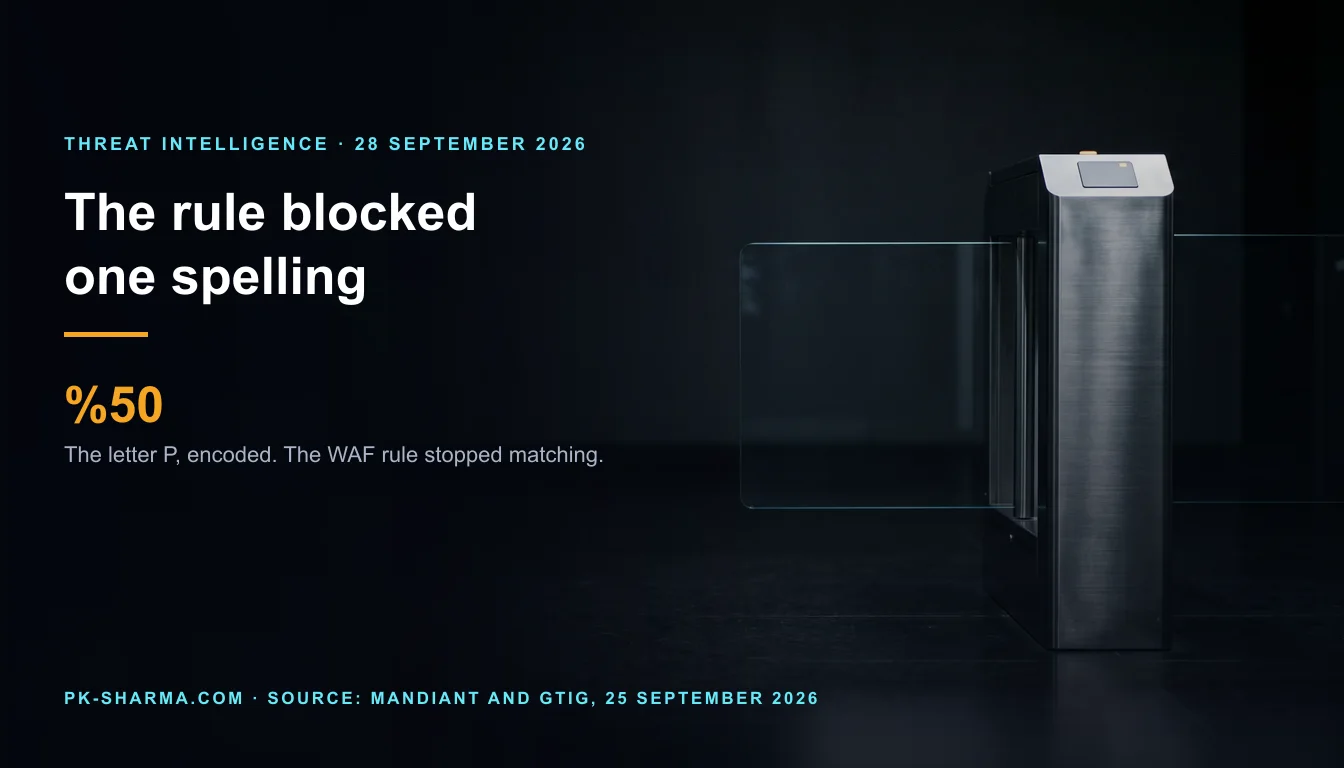
A rule that matches the text of a path is a control on one spelling of an endpoint, not on the endpoint. The attackers read the published guidance and aimed at the organisations that followed half of it.
KEV is a list of what is exploited, not a ranking of what is worst, and a three-day deadline makes it very easy to forget that. The Citrix bulletin of 27 September is a clean example of the difference.
CISA is not retiring the bulletin because it failed. It is retiring a faithful record of a model that stopped working, and the final edition shows exactly where it stopped.
There is no malware in this chain and nothing on the computer is affected. The product being manufactured is panic, and the delivery is ordinary paid advertising through uncompromised publishers.
A listing is not a sale and a registered account is not a customer. The Rydox court record contains both measures, and the gap between them is the story that the word marketplace hides.
A clean result from an automated check is not an observation about the site. It is a decision the operator made about the checker, and this chain makes that decision at three independent points.
The impersonated products do not exist: none of the three payroll platforms ships a desktop app. Allure Security counted 291 downloads and said plainly that some of them were researchers.
Nobody in this story was slow. The flaw is a CSRF check that skips validation whenever a literal string appears anywhere in the request URI, and the query string is written by whoever composes the link.
What eventually forced the backport was a ransomware gang's leak site being defaced. Grav shipped a 1.7 fix the day after the details became public, 144 days after the advisory.
The flaw that gains the most, 8.1 to 9.2, is a firmware verification weakness on a dashcam with no fix, from a vendor that has not responded to CISA. A robot vacuum is filed under Information Technology.
The structured data is right and the prose is wrong, which is the failure mode of every hand-written label sitting beside machine-readable fields. A team triaging by name goes hunting for the wrong thing.
Anything that caches on the version saw no change. The third entry is a WordPress Core remote file inclusion flagged for forensic triage, and a day later the trade press was still reporting two.
Two allied national cyber bodies, one CVE, three days apart, opposite conclusions. Neither is reading a sensor. Both are reasoning over the same thin public record, which is the part worth understanding.
A fake verification page that verifies nothing, measured by a panel that counts interface progress and labels it execution. The gap between an event and the thing it is named after is the entire story.
Two controls are not implemented at all, one is a stub that reports success without reading anything, and the self destruct does not uninstall or undo the damage. Your own device management console is read exactly the same way.
An indicator of compromise is a retrospective artefact. Publishing one says compromise is possible and checkable. Every tool that triages on the exploitation field saw nothing for 47 days.
Neither vendor says they are the same thing, and a shared builder sold as a service would explain it too. Either way, a defender reading one report and not the other is missing half the indicators.
Shadowserver counts about 160 exposed TeamCity servers still unpatched, down from roughly 700. The remaining ones hold build credentials and sign artefacts.
September now stands at 38 additions to the catalogue, 30 of them on a three day clock. The clock starts when CISA notices, not when the flaw became dangerous.
Roundcube has eleven entries in the CISA exploited catalogue, more than any other webmail. This one is not among them, four days after a national cyber centre warned about it.
A watch on the root of C: reports filesystem events across every user, with filenames, regardless of permissions. That was enough to identify which of the top 1,000 sites another user was visiting, with an F1 score of 97.8 per cent.
A defender triaging by the catalogue's own words would hunt for a file upload path. The flaw hands over an administrator session to anyone who signs a token with an algorithm the server never supported.
September is the busiest month of 2026 in the Known Exploited Vulnerabilities catalogue, at 1.48 additions a day against a yearly mean of 0.89. The deadline never varies with how hard the change is.
Six of the seven fell inside seven minutes, which is not guessing. It is one provisioning default, used repeatedly, on accounts nobody had looked at in years.
CERT Polska has published the full MikroTrick chain. The interesting part is not the bug. It is how little time withholding the details actually bought anyone.
Reserved names exist so copied example code cannot reach a live host. Somebody used a real domain instead. Every outbound request to it is now both an exposure and, usefully, a near zero false positive detection.
Yesterday the advisory gave defenders nothing to search for. Today there are request, response and file indicators, all of them from two firms selling protection. The vendor, the CISA KEV catalogue and the NVD record still say nothing happened.
The TrustSink technique does not extract passwords from Entra. It asks users for them a second time, on a full page a third party draws inside a trusted sign-in, and Entra validates only the token that comes back.
Microsoft says it typically publishes definitions three times a day, and its device health report treats a signature build as current for seven days. A blocked machine can therefore sit about twenty releases behind and still read as protected.
The token inside a GitLab issue by email address does not expire, covers every project the account can reach, and is exempt from IP restrictions. Seven properties, six documentation pages, and one copy button.
The only precise figure the fake Claude Max giveaway publishes is 92.5 per cent of slots gone, and it is generated in the visitor's browser. What the research does not establish matters more than what it does.
The second WordPress core security release in five days fixes an unauthenticated path traversal that selects a PHP file to run, not to read. Two preconditions must hold, and the hardening constant that mattered last week does nothing here.
Two of the four new KEV entries name Check Point, but only one is the management server. The take that fixes the other is the top of the vulnerable range for it. What the four advisories do not state matters more than what they do.
Nine ICS advisories, six of them republished Siemens notices, one flaw already on the known exploited list since May, and two fixes that no vendor can simply install. A prioritisation guide for UK OT owners.
D-Link has acknowledged two critical DIR-822A flaws with public exploit code, but the bulletin confirms no hardware revision, no lifecycle status and no firmware fix. The UK PSTI regime would not have helped the owners either.
A guest to host escape in Linux KVM on ARM64 reached shipping kernels on 28 September 2025 and was fixed in stable on 11 September 2026. Who is exposed comes down to one boot parameter.
Microsoft relabelled CVE-2026-65660 from spoofing (6.5) to remote code execution (8.8) 16 days after release. The fix was always in the August updates; the risk is teams that sorted by the first label.
A second exploited CVSS 10.0 flaw in on-premises VeloCloud Orchestrator in 57 days. Here is how to tell if you are exposed, the patch path by release train, and what Arista says to look for in your logs.
Alinubx.sys carries a 2023 Microsoft hardware signature, kills 145 AV and EDR processes, and was not on Microsoft's vulnerable driver blocklist at publication. What the blocklist, HVCI and the ASR rule do and do not cover.
WordPress core shipped 25 security releases on 17 September for a comment XSS that can reach an administrator's session. What to confirm, which wp-config setting actually blocks plugin upload, and why updating does not remove a plugin already added.
BigDiskBuster, released on 19 to 20 September 2026, keeps Defender on whatever signatures it already has. Microsoft's own reports can call a device up to date for seven days. Here is how to measure currency, not status.
CVE-2026-7273 in Zyxel GS1900 switches entered KEV on 21 September with a 24 September deadline after GreyNoise documented data theft from 996 switches. CVE-2026-32996 in Veeam Agent for Windows has a public PoC but no KEV entry.
CLOSEDQUORUM asks DeepSeek, Qwen, Mistral and Gemini which of four attack actions to take, then acts on the plurality. Talos found placeholder keys, no confirmed victims and a narrower first than the headline suggests.
A COM class that points at a DLL that does not exist is not harmless. Project Zero shows how a dangling registration in a writable path becomes SYSTEM, and how to audit your estate for the same pattern.
Rust maintainers are being lured onto video calls to install a fake audio codec or paste a command. The arrayref release of 20 August, downloaded 2,285 times in 86 minutes, shows why their accounts are the prize.
ChainScript turns a pasted Win+R command into a per-user MSI, a hidden Node.js agent and a C2 address stored on the Polygon blockchain. Here is the chain step by step, why the pointer survives takedown, and the controls that still work.
The same two Jade Sleet backdoors that helped take 292 million dollars from KelpDAO turned up on an Indian IT provider with no crypto ties. What the vendor established, what it did not, and what UK firms that outsource to Indian MSPs should ask this week.
TeamPCP stole more than 500,000 credentials but, by Google's estimate, made only tens of thousands of dollars. What an undercover analyst saw, what rests only on one researcher's account, and what UK engineering teams should change.
TASK#STOMP relies almost entirely on wscript, PowerShell, Task Scheduler and the .NET compiler, so it leaves no conventional executable to catch. It also leaves a script block log, a task creation event and an AMSI scan behind at every step. The report does not name a victim, sector or attacker.
Two GPOs, six settings, no Windows malware: how PAYLOAD used Group Policy for domain-wide extortion, what Kaspersky could not establish, and the Microsoft audit events that would have seen it.
The Clop defacement is confirmed at the presentation layer. The evidence does not yet establish server root, victim-data access or control of the onion identity.
A joint advisory of 18 September 2026 puts at least 30,000 exploited PCs and over 7,000 drained cryptocurrency wallets behind a fake recruitment campaign. The arithmetic says the access, not the crypto, was the product. No UK victim is named.
Fake GitHub organisations impersonating LastPass Authenticator ranked in search and delivered an infostealer behind a Microsoft signed driver that terminates 145 security products. The repositories are gone. Most of the delivery chain is not.
About 170 private CrowdSec repositories were cloned in nine minutes and four seconds on 22 May 2026, using the account of a developer who had just left. GitHub's own documentation explains why the organisation audit log was empty.
The forced theme install is real, the chain to code execution is real, and both run on an administrator's session. Here is what WordPress fixed, in which versions, and what its own release notes do not say.
Three Linux kernel CVEs entered CISA's KEV catalogue on 18 September 2026 and four others got public local root exploits the same day. No CVE appears on both lists, and the patch state differs sharply between them.
CVE-2026-58138 lets anyone who can reach an unpatched Conductor server run operating system commands on it. The open-source build has no authentication to bypass, and the orchestrator holds credentials for everything it orchestrates.
WeaselBiscuit executed on import rather than install, so the standard ignore-scripts control sat at the wrong gate. Every package is now gone from npm, median takedown under 13 hours. Here is what it could actually reach.
CVE-2026-91843 lets an unauthenticated attacker run code as root on Check Point Security Management, Multi-Domain and Log Servers. The advisory names eleven affected version bands and offers four packages. No exploitation is reported and one indicator is published.
CISA retires its weekly Vulnerability Bulletin on 28 September. We parsed 70 issues: it was a CVSS-sorted copy of CVE records, with no exploitation signal, long gaps and a "Not Yet Assigned" table that hid CVSS 10.0 exploited flaws.
KREMLIN copies an extension into Chrome and Edge, enables developer mode and regenerates the Secure Preferences integrity MACs so the browser loads it as approved. It changes what an ExtensionSettings allowlist can and cannot promise.
The Pixel modem zero-day is real and fixed at patch level 2026-09-05. The record names no targets, no attacker and no chain, and CISA's CVSS score moved from 8.0 to 8.8 within a day with nothing new from Google.
An unauthenticated root path into Cisco ISE and a local privilege escalation in Acronis's cPanel backup plugin entered KEV together. What each attacker needs first, what fixes it, and what the three-day clock means in the UK.
CVE-2026-76461 lets a crafted email run root commands on Cisco Secure Email Gateway. The KEV deadline is today. The upgrade closes the hole; it does not tell you whether the gateway, and the credentials it holds, were already taken.
Read from the joint advisory in full. A unique Telegram bot per victim removes the pivot defenders rely on, and the escalation to personal devices lands outside every control on the asset register.
A careful reading of Anthropic's targeting and conventional-weapons evaluations, including the 37 km geolocation result, simulated strike rates, limitations and practical controls.
Read from Microsoft's own CVRF. Nothing is publicly disclosed, the 1,170 figure is a month's accumulation, and the field to check is Customer Action Required.
Read from Adobe's own bulletin, the NVD record and CISA's catalogue. A fully patched store was still taken, and the catalogue has not moved since Friday.
MikroTrick, the indicators of compromise, and the methodology section almost nobody quoted. The vendor's own detection marker does not prove a device is clean, and CERT Polska say so.
The most consequential sentence in the IOS XR advisory is the one about how the flaws were found, and almost every write-up removed it. What follows from it is a counting problem.
A directive reported as reducing the patching burden coincides with the most aggressive tier becoming the default on three quarters of new entries. Two opposite errors are circulating about it.
AS62390 announced a Hetzner /24 for 33 hours, diverting Softaculous update traffic. Let's Encrypt issued a valid certificate because its own domain validation was routed through the hijack.
Exploit code for an unpatched local privilege escalation in CrowdStrike Falcon Sensor appeared at 02:48 UTC. The README contains two qualifications the coverage has dropped.
Kestra, LiteLLM and Starlette joined the KEV catalogue at 16:54 UTC with no coverage at all. All three were months old, and the titles misdescribe two of them.
Check Point Research documents Gambling Goblin compromising Brazilian government web servers since mid-2025. The module reverse-proxies three hardcoded prefixes and strips their Content-Security-Policy.
Read from the KEV feed and the NVD API on 2 September 2026: three loud exploitation claims, none catalogued, and a substitution trap where searching KEV by product name clears the wrong identifier.
Thirteen trojanised theme packages were pulled after Socket published. Checked by hand today: a sibling package Socket named as a sleeper is still installable, and the malicious jQuery is still on GitHub.
Kaspersky documents a recruitment lure whose README bans AI code review, declares the trojanised file bug-free, and ships a malicious package inside the archive so no scanner ever sees it.
CVE-2026-82329 lets an unauthenticated attacker reach admin on Artifactory. JFrog fixed it the same day it was published, its advisory misstates the 7.146 fix, and the exploitation claim rests on one firm.
ESET disclosed an inert comment block designed to make AI analysis refuse. The whole primary source is three posts on X, nobody tested it, and Endor Labs documented the same trick in June.
Every stage uses documented Windows behaviour, so there is no patch, no KEV deadline and no scanner finding. The controls that reach it had to be set before the lure arrived.
Black Hat 2026 research with four identifiers, one unpatched open-source path AWS has assigned to the customer, and the reason prompt hardening measured the wrong component.
Huntress documents the first Akira use of Safe Mode boot. The full technique chain contains no exploit at all, the encryptor starved of virtual memory and failed, and the victim is still extortable.
One million implant check-ins, more than 15 government webmail tenants watering-holed by a single script tag, and a supplier relationship the coverage flattened into one team.
Pass-ta-key, Silver and Golden: account takeover with no user interaction, forged biometric verification, and every synced key exported for resale. Why two outlets reached opposite conclusions from the same paper.
Check Point attributes the August zero-day to Lazarus. The exploit is fixed, but the delivery chain, a recruiter approach and an SEO-ranked impersonation site, is untouched and still works.
Counted from Microsoft's release document: 420 CVEs, 176 elevation of privilege, 119 in Office. Why the published totals disagree, and why severity-first triage gets this month wrong.
Initial access changed. The attack path did not. Half of ransomware victims with a credential leak saw it within 95 days of the attack, a window long enough to act in, if anyone is looking.