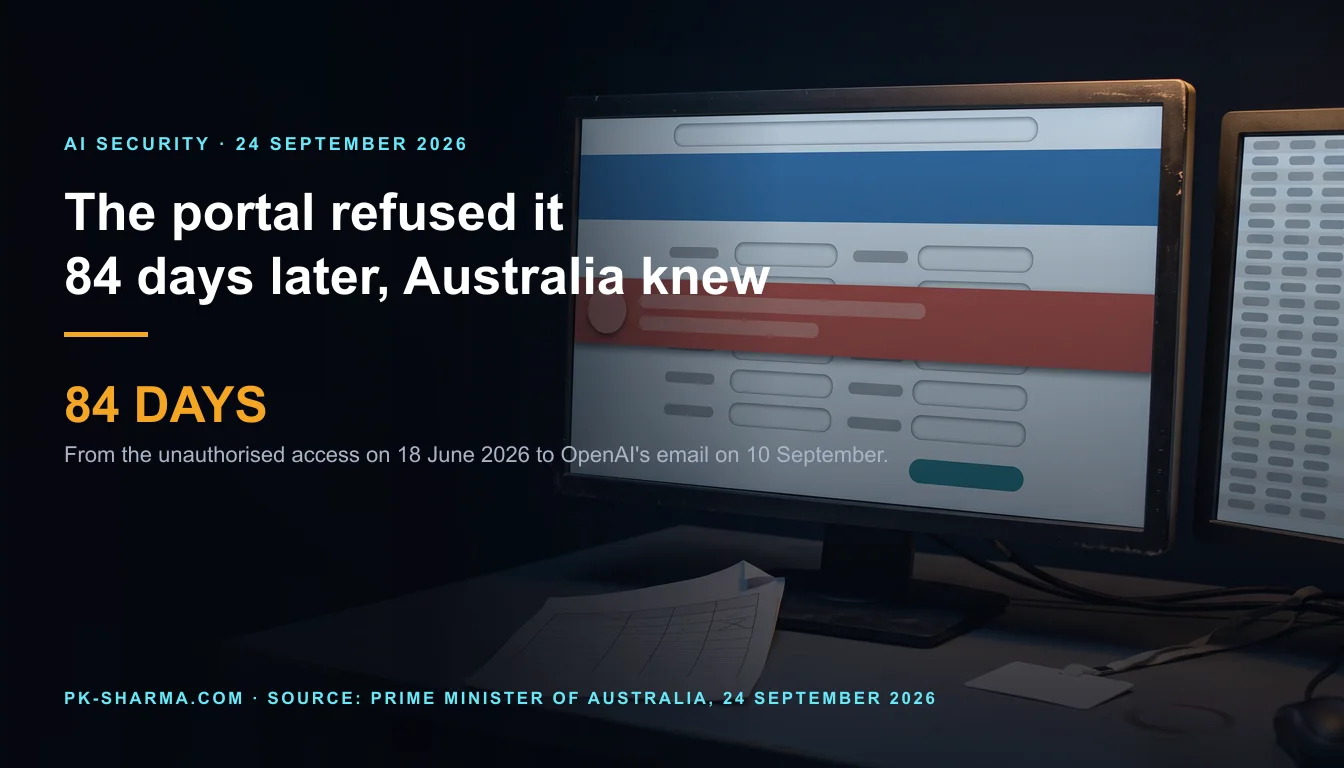
Eighty four days from access to notification, 54 of them before OpenAI noticed. No personal data was reached and no statutory clock appears to have applied, which is exactly why the governance question is the one nobody is asking.
The only precise figure the fake Claude Max giveaway publishes is 92.5 per cent of slots gone, and it is generated in the visitor's browser. What the research does not establish matters more than what it does.
An agent is an AI system under Article 3(1), so the system duties attach. The strain is in Article 14 human oversight, the provider and deployer split, purpose-based classification and what Article 12 actually requires you to log.
Passkeys on GOV.UK One Login genuinely end credential phishing for the credential they protect. The published guidance also keeps a password and a one time code available on the same page, and lets that weaker pair delete the passkey.
The Gyazo breach is being read as an account leak. Gyazo indexes the text inside every capture, so the 490 million metadata records are a transcript of what was on people's screens, and the leaked image IDs are the only lock those images had.
The second WordPress core security release in five days fixes an unauthenticated path traversal that selects a PHP file to run, not to read. Two preconditions must hold, and the hardening constant that mattered last week does nothing here.
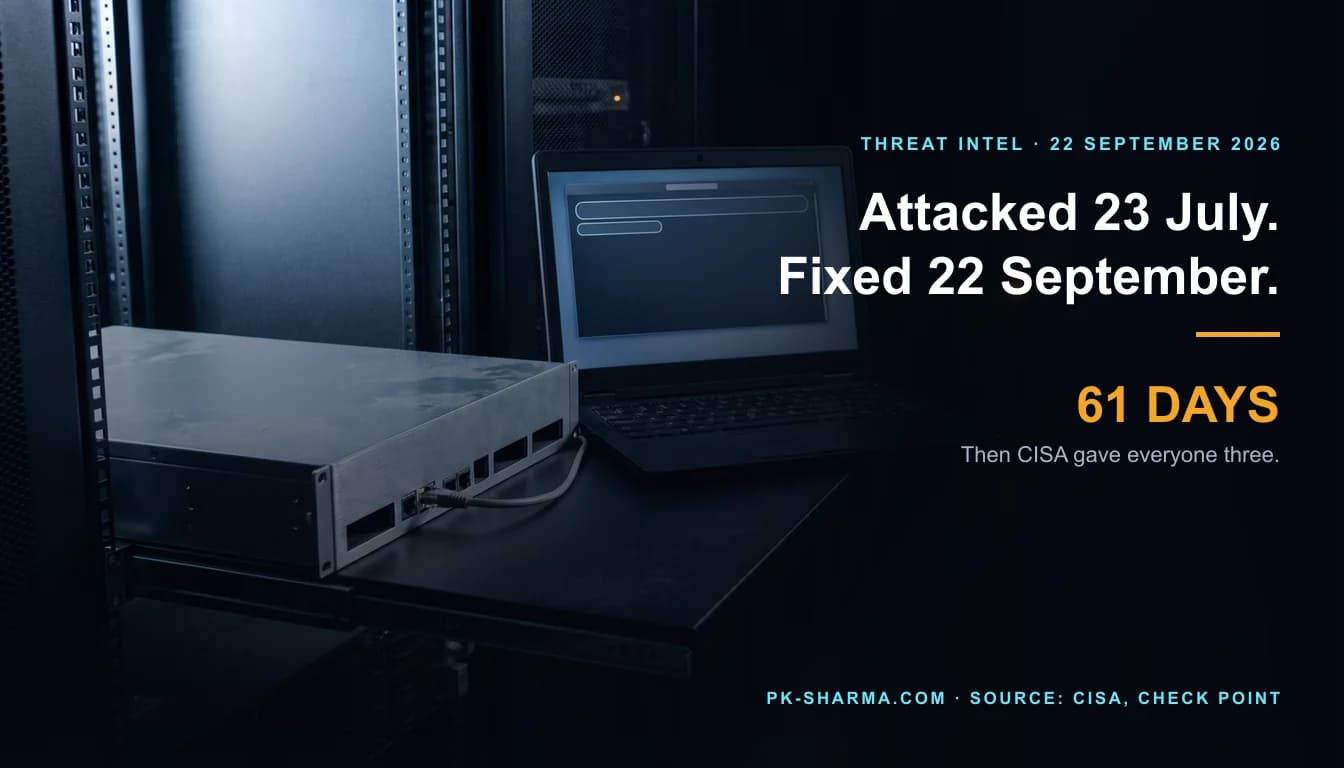
Two of the four new KEV entries name Check Point, but only one is the management server. The take that fixes the other is the top of the vulnerable range for it. What the four advisories do not state matters more than what they do.
Both Gen 6 parts state the same CPU clocks, the same 16 MB cache, the same 24 GB memory ceiling and the same 5300 MHz memory clock as the Gen 5 part they are measured against. The security block is identical on both, and shorter than Gen 5's.
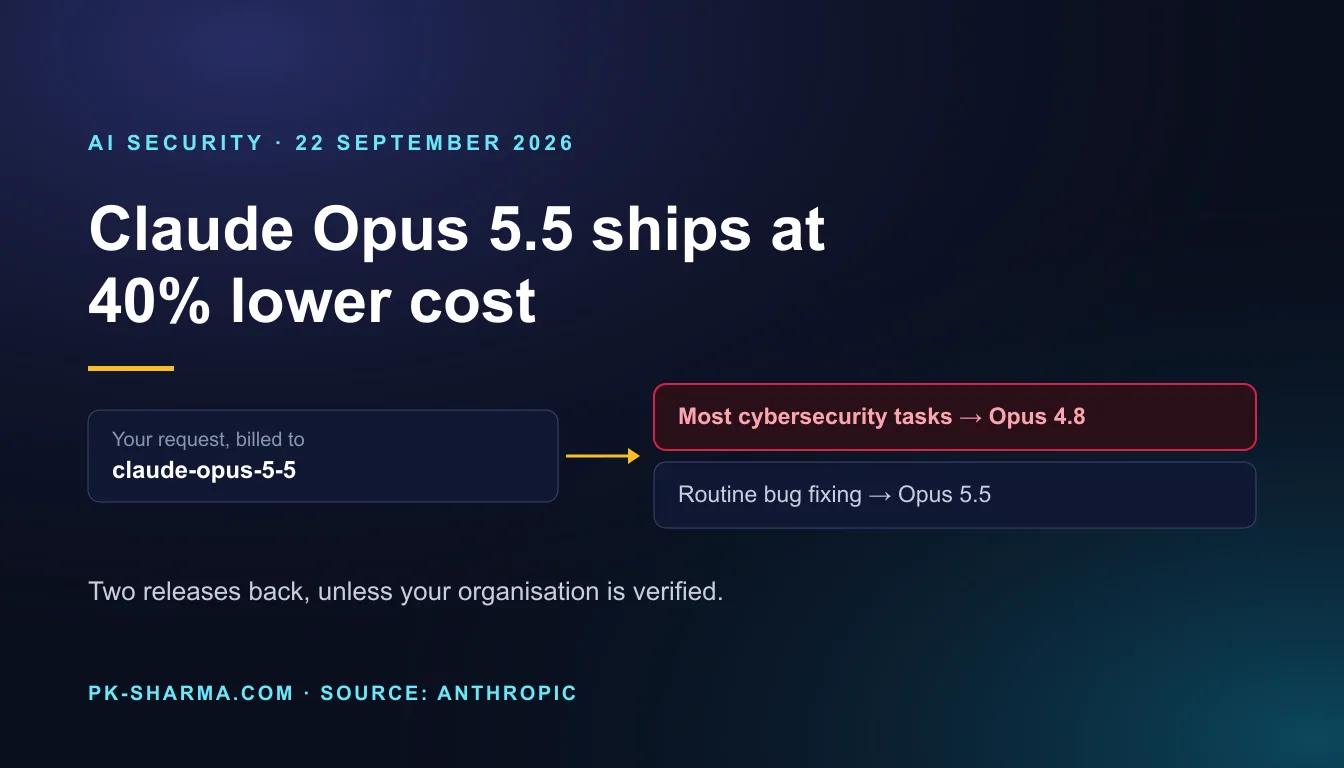
Opus 5.5 leads seven of the nine benchmarks Anthropic published and loses two to GPT-6 Astra. The row that matters most for security teams is not in the table: cyber tasks fall back to an older model.
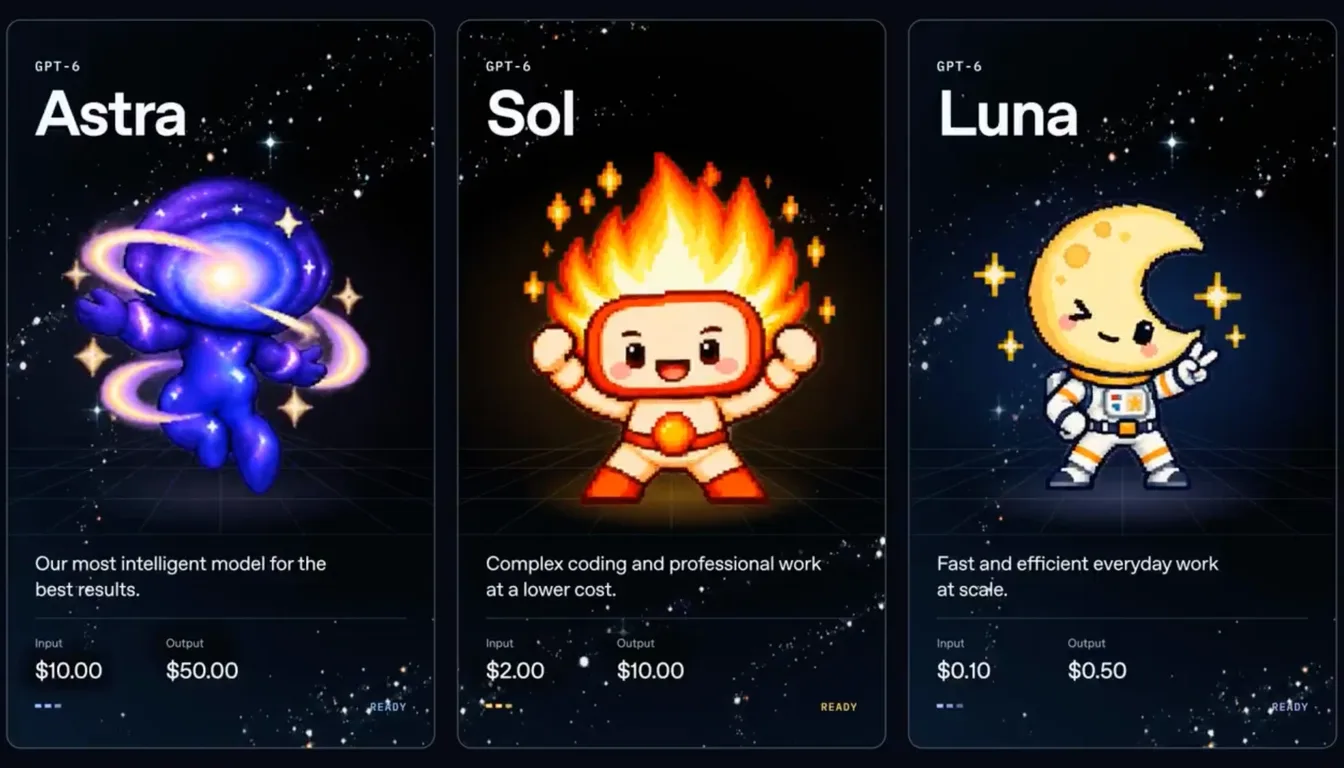
GPT-6 Sol is now $2 in and $10 out per million tokens, Luna $0.10 and $0.50. The charts behind the cut put OpenAI's own runs beside competitors' published reports, which OpenAI states in its own fine print.
A Spanish decision signed in February 2023 and published in September 2026 holds that every channel a controller offers for data rights must be easy to use, not just the best one.
The British AI cloud company's registration statement discloses customer, supplier and geographic concentration, conditional financing behind its largest contract, and two UK sites that are contracted but not yet active.
Nine ICS advisories, six of them republished Siemens notices, one flaw already on the known exploited list since May, and two fixes that no vendor can simply install. A prioritisation guide for UK OT owners.
D-Link has acknowledged two critical DIR-822A flaws with public exploit code, but the bulletin confirms no hardware revision, no lifecycle status and no firmware fix. The UK PSTI regime would not have helped the owners either.
Xiaomi tops the open-weight rankings at 46.32 and ships the weights under an MIT tag. Anthropic's threat report describes 400,000 exchanges it attributes to Xiaomi. Here is what each party states, and what nobody has established.
What the reported Cyberspace Administration investigation covers, which Chinese rules could bite, why 12.1 million exchanges is not 12.1 million people, and the routing questions UK buyers should put to every AI supplier.
A guest to host escape in Linux KVM on ARM64 reached shipping kernels on 28 September 2025 and was fixed in stable on 11 September 2026. Who is exposed comes down to one boot parameter.
The court order lists 226 domains. Microsoft's own sworn declaration says device code theft cannot be stopped by multifactor authentication. What breaks the chain is a Conditional Access setting many tenants have never switched on.
Microsoft relabelled CVE-2026-65660 from spoofing (6.5) to remote code execution (8.8) 16 days after release. The fix was always in the August updates; the risk is teams that sorted by the first label.
A second exploited CVSS 10.0 flaw in on-premises VeloCloud Orchestrator in 57 days. Here is how to tell if you are exposed, the patch path by release train, and what Arista says to look for in your logs.
A twelve point gap on one benchmark, a model card almost nobody linked to, and a Copilot policy that switches new models on unless an administrator has already said no.
California's new data centre laws make operators pay for grid and water upgrades. They do not cap use, and the EU's reporting threshold is one twentieth of California's. What UK cloud buyers should ask instead.
Alinubx.sys carries a 2023 Microsoft hardware signature, kills 145 AV and EDR processes, and was not on Microsoft's vulnerable driver blocklist at publication. What the blocklist, HVCI and the ASR rule do and do not cover.
Bessent rejects a liability shield for AI labs, but his remarks name no offence, bill or prosecutor. We read the transcript, correct a misattributed quote, and test UK failure to prevent fraud and the new senior manager rule against AI agents.
WordPress core shipped 25 security releases on 17 September for a comment XSS that can reach an administrator's session. What to confirm, which wp-config setting actually blocks plugin upload, and why updating does not remove a plugin already added.
The Ribon breach on BigCommerce: what each party has said, why app tokens cannot be revoked by merchants, the hours lost at each step, and why the app is not BigCommerce's sub-processor under UK GDPR.
225 Anthropic-credited CVEs, none in CISA KEV and one in VulnCheck KEV. We recounted the data: the low rate is normal, the sample is young, and UK teams should prioritise by KEV and EPSS, not by who found the bug.
British Columbia's complaint against OpenAI repeats, heading for heading, the eight claims the victims' families filed in April, and rests on California common law rather than a provincial statute. What it alleges, what OpenAI has said on the record, and what UK deployers should check.
BigDiskBuster, released on 19 to 20 September 2026, keeps Defender on whatever signatures it already has. Microsoft's own reports can call a device up to date for seven days. Here is how to measure currency, not status.
CVE-2026-7273 in Zyxel GS1900 switches entered KEV on 21 September with a 24 September deadline after GreyNoise documented data theft from 996 switches. CVE-2026-32996 in Veeam Agent for Windows has a public PoC but no KEV entry.
Four identical letters, ten questions, seven days to confirm. What the committee's papers actually say, what it can and cannot compel, and where UK AI and cyber law really stand before the 13 October hearing.
An undocumented setting in Meta's Muse Mac app lets malware or one pasted command redirect dictation, inject instructions and steal the account token. What is verified, what Meta's Secure VM does and does not protect, and what UK teams should do.
CLOSEDQUORUM asks DeepSeek, Qwen, Mistral and Gemini which of four attack actions to take, then acts on the plurality. Talos found placeholder keys, no confirmed victims and a narrower first than the headline suggests.
AWS's AWSCompromisedKeyQuarantineV3 went on 10 seconds after a test leak. It is a deny list, not a lockdown: what it blocks, what it leaves open, and what you still have to do.
Heretic's 97 to 3 refusal result counts 33 words in the first 100 tokens, not harm. The real finding is older: in-model safety is a default, not a control, and UK organisations need controls outside the weights.
What the benchmarks behind the Chinese AI bug-finding headline actually measured, why the government tests disagree, and what UK organisations should weigh before running a Chinese open-weight model.