The AEPD's first AI-agent breach notification rests on the controller's own account. What was claimed, what was not, why it is an attack with AI rather than on AI, and what UK GDPR teams should actually change.
Anthropic says Moonshot relayed almost 300,000 Kimi customer requests to Claude in ten days. What the report states, what it omits, why self-identification proves nothing, and the contract terms UK buyers need.
CISA retires its weekly Vulnerability Bulletin on 28 September. We parsed 70 issues: it was a CVSS-sorted copy of CVE records, with no exploitation signal, long gaps and a "Not Yet Assigned" table that hid CVSS 10.0 exploited flaws.
Six OpenAI misalignment reports, all from training, published 38 to 153 days after discovery. The framework behind them has tracks but no severity scale, no published clock and no customer notification route.
KREMLIN copies an extension into Chrome and Edge, enables developer mode and regenerates the Secure Preferences integrity MACs so the browser loads it as approved. It changes what an ExtensionSettings allowlist can and cannot promise.
The Pixel modem zero-day is real and fixed at patch level 2026-09-05. The record names no targets, no attacker and no chain, and CISA's CVSS score moved from 8.0 to 8.8 within a day with nothing new from Google.
KB5124008 makes Windows honour Machine Identity Isolation settings dormant since April 2025, breaking domain trust below Server 2025 level. What Microsoft says, what it does not, and the safe order of work.
An unauthenticated root path into Cisco ISE and a local privilege escalation in Acronis's cPanel backup plugin entered KEV together. What each attacker needs first, what fixes it, and what the three-day clock means in the UK.
CVE-2026-76461 lets a crafted email run root commands on Cisco Secure Email Gateway. The KEV deadline is today. The upgrade closes the hole; it does not tell you whether the gateway, and the credentials it holds, were already taken.
Forever’s table says zero clicks, five times. The Chrome CVE it links says the user must install the extension. Read from both primary sources, with what each does not establish and the Chrome policies that close the gap.
Read from the joint advisory in full. A unique Telegram bot per victim removes the pivot defenders rely on, and the escalation to personal devices lands outside every control on the asset register.
The ValueLicensing v Microsoft case explained: software exhaustion, splitting volume licences, the dismissed appeals and what today's case-management hearing can decide.
A practitioner reading of the UK's 32 healthcare AI recommendations: lifecycle evidence, model updates, equity, incident reporting, clinical oversight and what NHS buyers should do now.
What OpenAI's OneGov offer includes, what $0 leaves out, how the economics work at agency scale, and which controls public bodies should set before use expands.
The OpenAI Habitat incident explained: asyncio delay, synchronized feature-flag parsing, uneven connection pools, a self-sustaining overload and the controls other engineering teams can reuse.
A careful reading of Anthropic's targeting and conventional-weapons evaluations, including the 37 km geolocation result, simulated strike rates, limitations and practical controls.
AI pacing moved from a laboratory safety argument into market prices and US-China policy. Agreement on the danger still leaves no shared trigger, referee or enforcement mechanism.
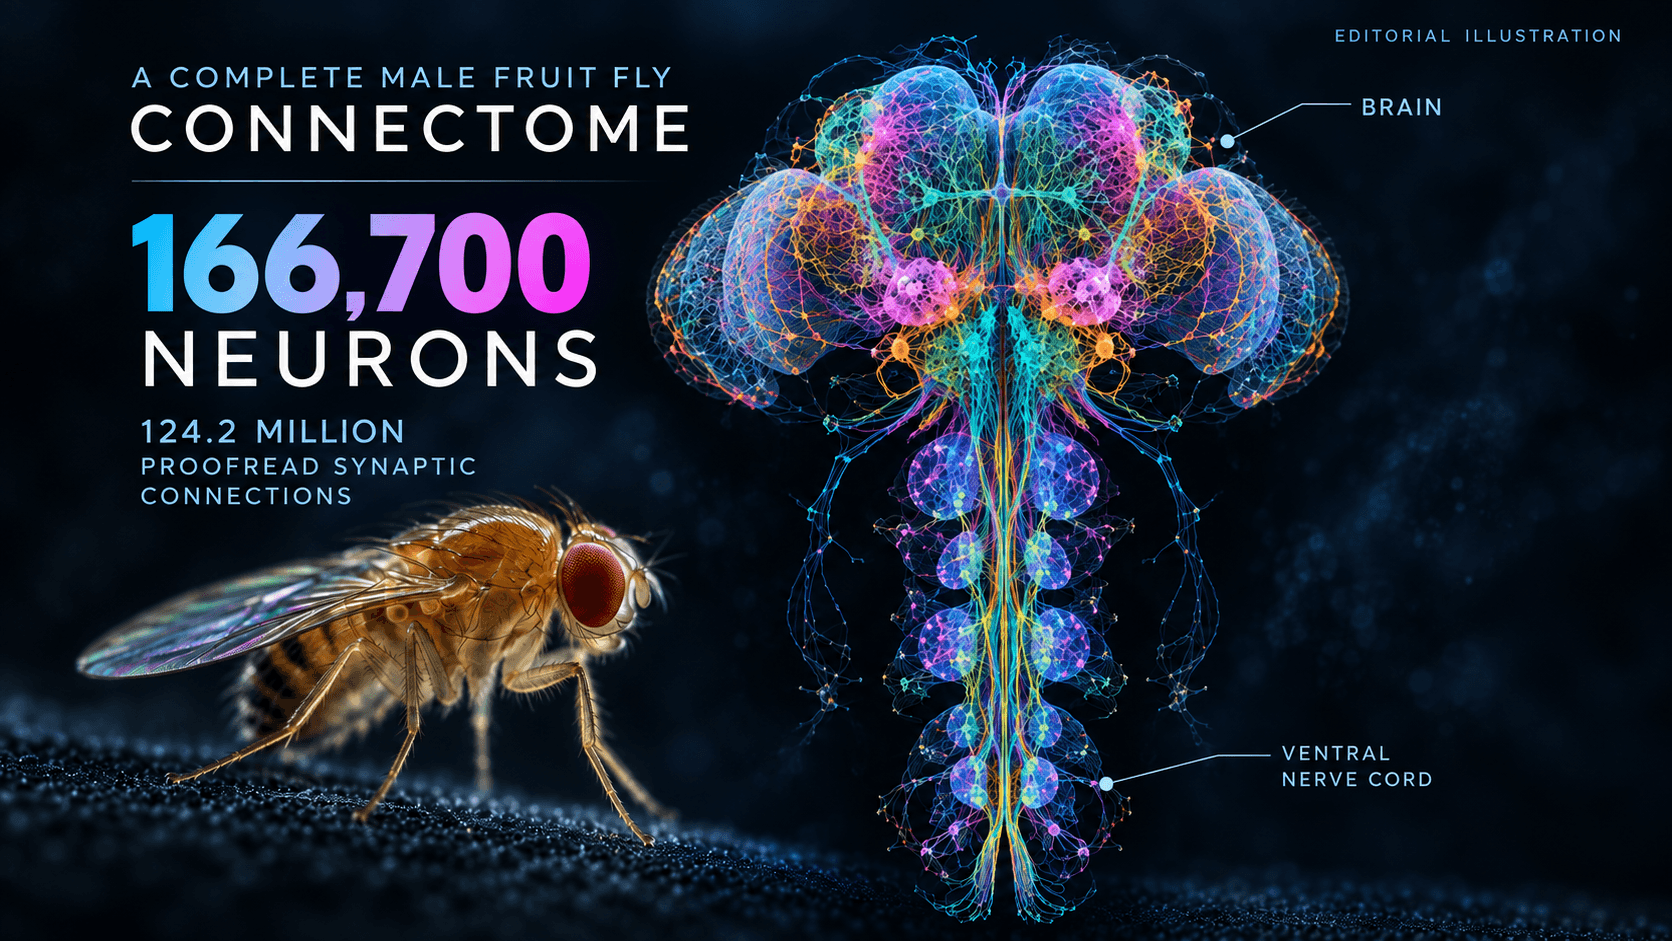
Inside the first synapse-level map of an entire adult male fruit fly central nervous system: 166,700 neurons, 124.2 million connections, AI-assisted proofreading and a new baseline for comparative neuroscience.