The dates behind the BeyondTrust Remote Support zero-day, what the record does not establish (victims, Privileged Remote Access, the patch), nine labels read against the primaries, four UK clocks, and ordered checklists for a service desk, an MSP and a CISO. Defender level only.
Three OpenAI reports of 15 October read in full: what each says a model did, the 57 to 91 days before discovery, what is stated and not stated, UK law and where it stops, and ordered checklists for labs, enterprises and public bodies. Defender level only.
What Anthropic's 15 October post on METR and other evaluators establishes, what changed on 16 October, who pays whom, what the White House Accord requires, how the bank analogy maps onto UK law, and what a UK buyer can ask.
A source-led timeline, the operational split between filing and service, district-by-district orders, and the facts still missing about the BAE Systems incident.
How the fake yyay package used a valid source archive as cover, what the .install script changed, what is confirmed about removal, and practical checks for Arch users.
What SPACE actually provides, how its control and command paths differ, the reported red-team results, local deployment requirements and security questions for adopters.
An evidence-led comparison of GitHub AI Scan and agentic autofix: coverage, branch limits, merge blocking, prerequisites, billing and a practical rollout plan.
A precise before-and-after comparison, affected versions, NTLM event IDs 4024 and 4025, a scoped temporary exception and the migration path for Wi-Fi, Ethernet and VPN.
What happened, which Remote Support versions need BT26-05-RS, the observed SAWFLY and BARECLAW tradecraft, and where defenders should look when on-device logs have been erased.
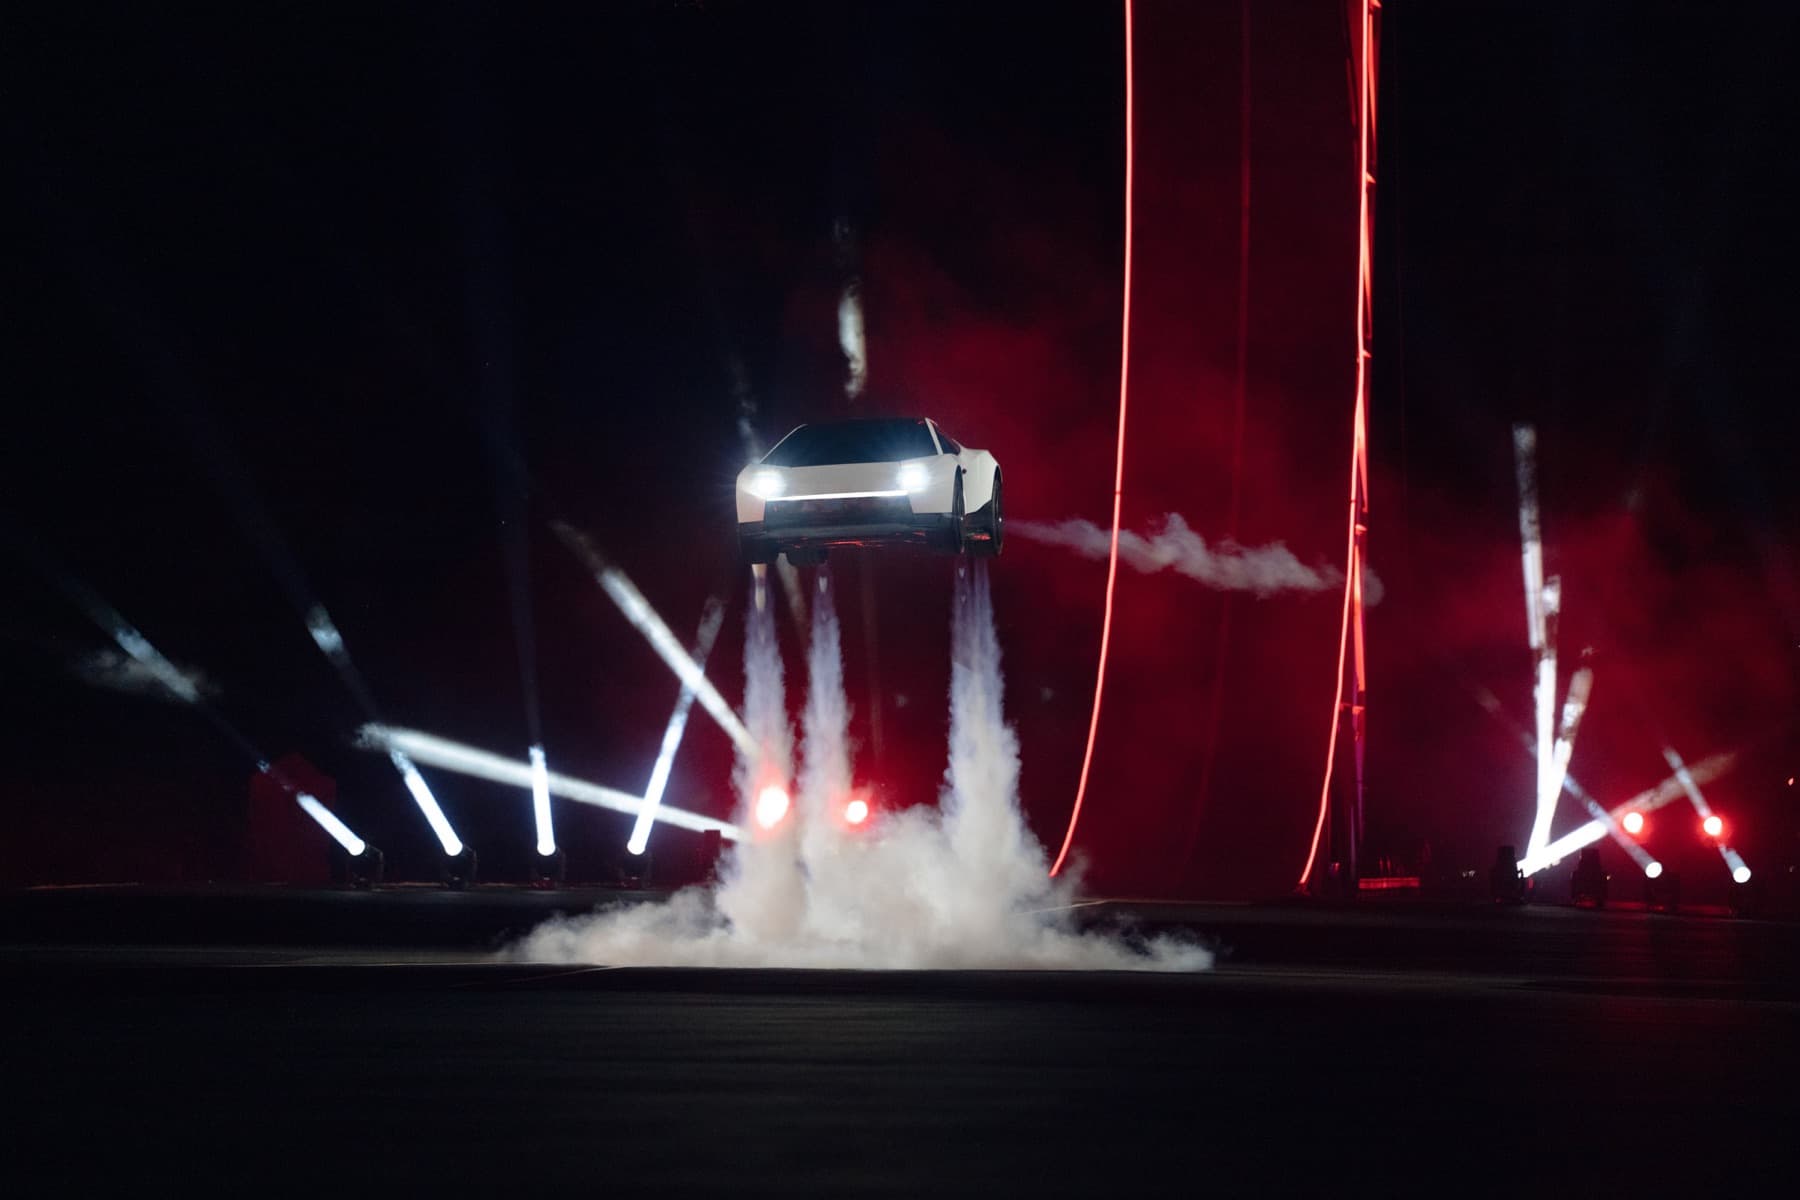
Tesla’s new Roadster flew and flipped in a controlled demonstration. We examine the three versions, Tesla’s performance claims, and the UK reservation terms.
What Symantec's report establishes about Aoki and AI assistant credentials, what it leaves out, the dated record, vendor statements on storage, lifetime and revocation, what UK guidance covers, and ordered checklists. Defender level only.
What Citizen Lab's AdFection report and Confiant's post establish, what they leave out, why the 45 devices and the 441,954,291 impressions cannot be divided, what the ad platforms said, what UK guidance covers and where it stops, and three ordered checklists. Defender level only.
What the Drupal Security Team's advisory and release notes state and do not state about CVE-2026-108097, the arithmetic behind 28.5 per cent, the May exploitation precedent, UK controls and where they stop, and a ranked checklist for three kinds of owner. Defender level only.
What Check Point, LiteLLM, CVE.org, PyPI, CISA and independent researchers say about two LiteLLM gateway flaws: the dates, the versions, who needs what access, what exploitation is reported, UK controls and a ranked checklist. Defender level only.
What changed between versions 1.1 and 1.2 of the NCSC's TLS guidance, how many recommendations carry a date or a test, how far the 2028, 2031 and 2035 milestones are, which groups are on by default, what the UK instruments say, and a ranked checklist.
What the Bill, its amendment list, Hansard and the Government's three 12 October texts establish about AI in the Cyber Security and Resilience Bill, what they leave out, the calendar in days, which department owns it, what binds UK organisations now, and a ranked checklist.
What the Legal Aid Agency's 14 October 2026 update states about records back to 1978, what it leaves out, the arithmetic behind the moving start date, why old records were online, what UK law and policy say, and a ranked checklist. Defender level only.
What Anthropic's 14 October 2026 post establishes about election use of Claude and what it leaves out: the arithmetic behind 0.002%, the 99% beside 85% on the same cards, where UK rules stop for chatbots, and checklists for election teams, communications leads and companies.
What the eight state filings plead about children, what they do not establish, where OpenAI's own pages agree and differ, what UK rules cover a chatbot children use, and a checklist for a school, a parent-facing organisation and a company.
What the ICO's reprimand and enforcement notice to the Met establish about the Auror platform, what they leave out, the dates and deadlines worked out, which UK regime governs police and retailer flows, and ordered checklists for a force DPO, a retailer and a vendor.
What Unit 42's PEERSTITCH report states and leaves out, the fix dates for four Fortinet flaws, why patching the FortiManager does not return stolen keys, what the NCSC, Cyber Essentials and the ICO say, and a ranked checklist. Defender level only.
What HiddenLayer's two pages print for Jev, what they leave out, the arithmetic on the one count they give, an independent preprint on the same version, TypeSafe's claims against its own documentation, what UK guidance says, and a ranked checklist. Defender level only.
Noma's SneakPeek dates computed from its blog and press release, which disagree on the first fix; what Anthropic's changelog and advisories say, which versions are fixed, whether auto-update applies, UK controls and an ordered checklist.
What Palo Alto's advisory, CISA's entry and the NCSC's pages establish about CVE-2026-0322: a 3-day window against Cyber Essentials' 14, which PAN-OS builds are fixed, ten open questions, UK controls and an ordered checklist. Defender level only.
What the DOJ releases and the 58-page indictment state about the 40-plus Texas residences, the 14 charged, the $3 million and the 70-plus companies, where five news stories count differently, what UK law asks of an employer hiring remote developers, and an ordered checklist.
What XBOW's pages, Google's release notes, rules page and public tracker, and OpenAI's model pages establish about a six-day Chrome chain, what they leave out, the arithmetic, UK patch clocks and the Computer Misuse Act as read, and a ranked checklist.