Yesterday the advisory gave defenders nothing to search for. Today there are request, response and file indicators, all of them from two firms selling protection. The vendor, the CISA KEV catalogue and the NVD record still say nothing happened.
The TrustSink technique does not extract passwords from Entra. It asks users for them a second time, on a full page a third party draws inside a trusted sign-in, and Entra validates only the token that comes back.
Microsoft says it typically publishes definitions three times a day, and its device health report treats a signature build as current for seven days. A blocked machine can therefore sit about twenty releases behind and still read as protected.
The token inside a GitLab issue by email address does not expire, covers every project the account can reach, and is exempt from IP restrictions. Seven properties, six documentation pages, and one copy button.
The only precise figure the fake Claude Max giveaway publishes is 92.5 per cent of slots gone, and it is generated in the visitor's browser. What the research does not establish matters more than what it does.
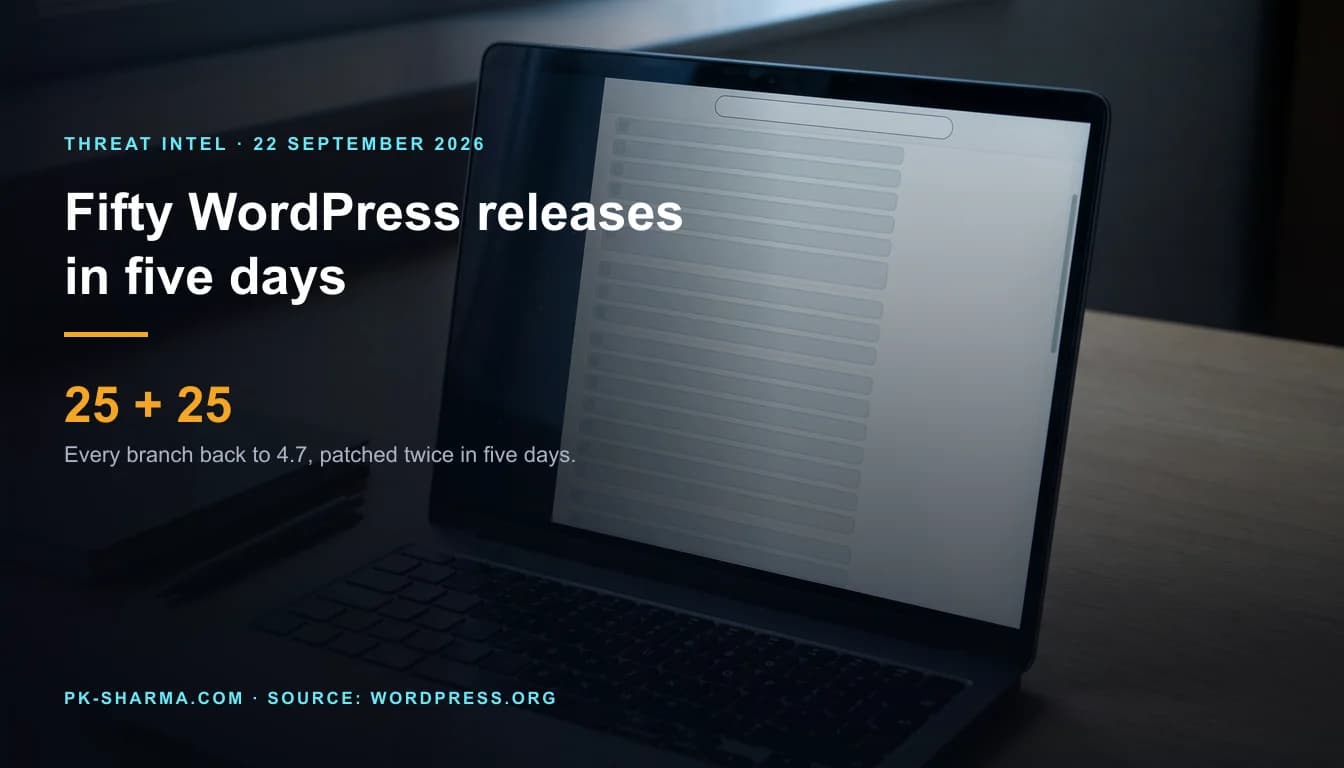
The second WordPress core security release in five days fixes an unauthenticated path traversal that selects a PHP file to run, not to read. Two preconditions must hold, and the hardening constant that mattered last week does nothing here.
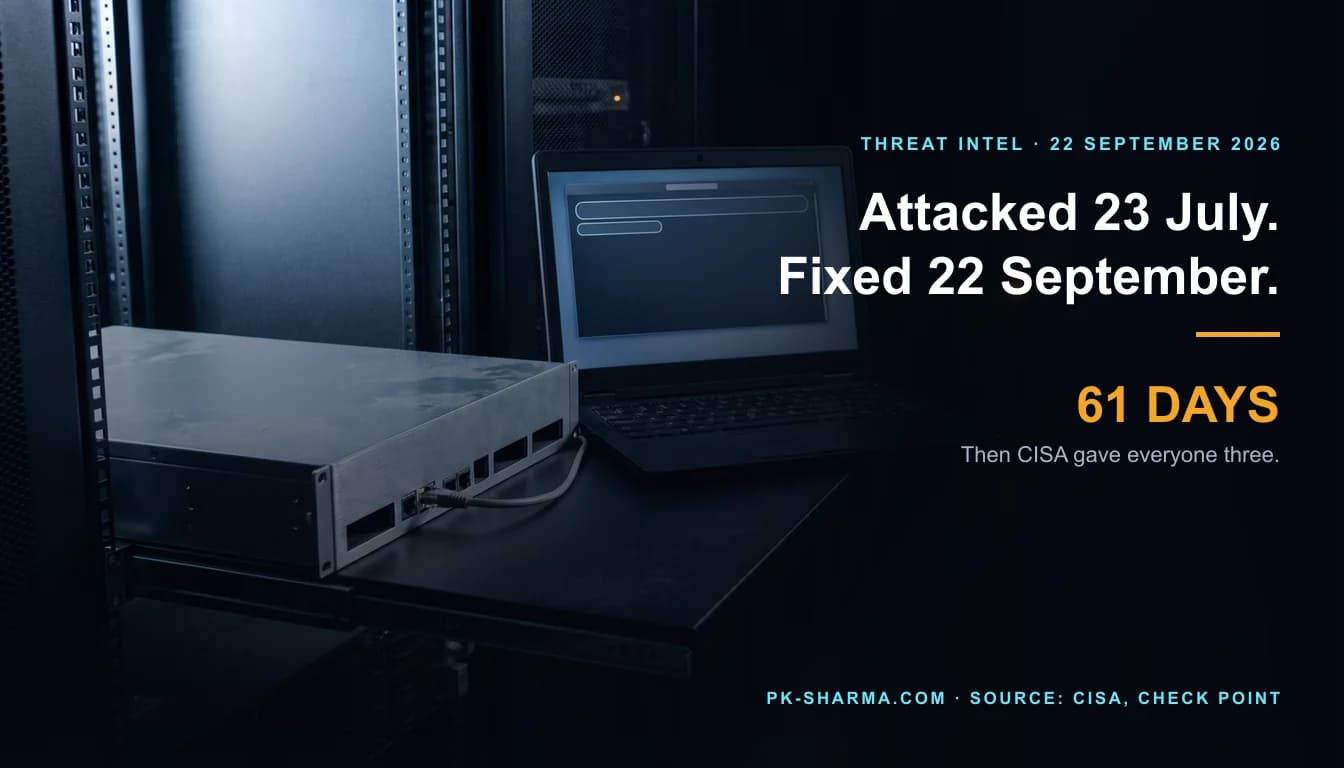
Two of the four new KEV entries name Check Point, but only one is the management server. The take that fixes the other is the top of the vulnerable range for it. What the four advisories do not state matters more than what they do.
Nine ICS advisories, six of them republished Siemens notices, one flaw already on the known exploited list since May, and two fixes that no vendor can simply install. A prioritisation guide for UK OT owners.
D-Link has acknowledged two critical DIR-822A flaws with public exploit code, but the bulletin confirms no hardware revision, no lifecycle status and no firmware fix. The UK PSTI regime would not have helped the owners either.
A guest to host escape in Linux KVM on ARM64 reached shipping kernels on 28 September 2025 and was fixed in stable on 11 September 2026. Who is exposed comes down to one boot parameter.
Microsoft relabelled CVE-2026-65660 from spoofing (6.5) to remote code execution (8.8) 16 days after release. The fix was always in the August updates; the risk is teams that sorted by the first label.
A second exploited CVSS 10.0 flaw in on-premises VeloCloud Orchestrator in 57 days. Here is how to tell if you are exposed, the patch path by release train, and what Arista says to look for in your logs.