The 9.9-rated flaw is about an authenticated flow configuration crossing a server-side boundary, and only self-hosted AI Gateways require the published upgrades.
The overlooked issue is the boundary between retrieving public data and probing a site for alternative behaviour. Request counts, failed tests and attribution need separate labels.
The accessibility control is valuable, but users and responders need to distinguish the Android version, Device protection and a separate 12-month forensic log.
The operational hazard is not only the IBE file-write flaw. Two official version lists disagree and Fortinet's fixed releases are still marked upcoming.
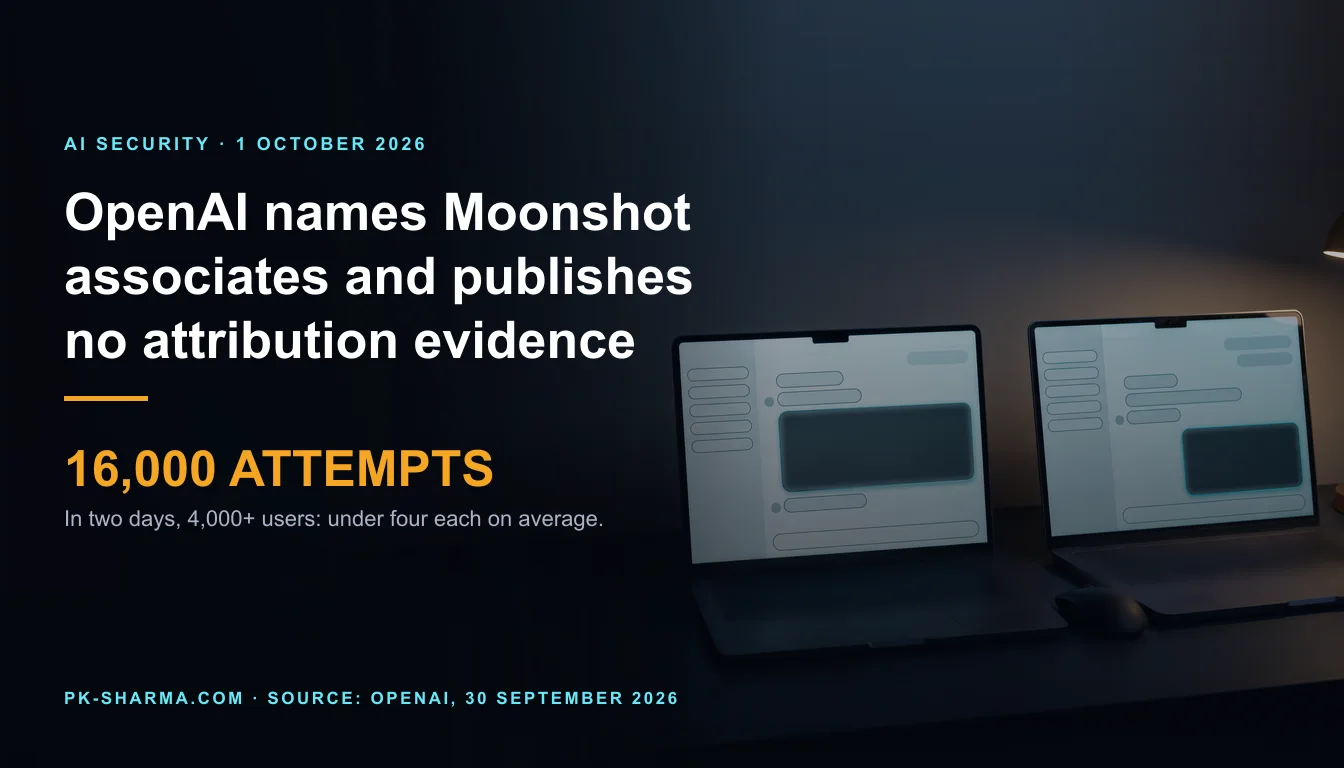
The spike was 16,000 attempts from over 4,000 users, under four each on average. What that does and does not establish, why a terms-of-service violation is not a breach, and what UK providers and buyers should check about extraction at the API layer.
Three provisional arrests, five servers, five domains and 110 TB, in a case led from Hamburg with one arrest in the UK. The counts do not match, and no release describes how victims will be told or what happens to files already published.
The 10.0 flaw has a CVE, a score and a fixed version. The flaw Kiteworks said it found during the shutdown has none that any record attaches to it, and no advisory in the batch says whether it is there.
All three attacker sender addresses in Proofpoint's July list are consumer webmail. A reading of its 1 October report on TA419: what it states, what it leaves out, why MFA and DMARC miss the chain, and an ordered checklist for UK organisations.