The complete 16-ID inventory, what Google's retirement wording means, where self-deployment differs from MaaS, and the tests to run before routing production traffic elsewhere.
Voxtral Small Transcribe 3 records 2.1% error in Artificial Analysis testing. We check the six Mistral prices, live-session limits and a conflict in TTS language documentation.
The 21 October launch joins structured-data prediction to agent tooling. We separate the four Kumo tasks, earlier model dates, licence differences and the control needed between a prediction and an action.
The 333 measured SSH redirects, the 377 policy matches, the Ebury case on one operator's servers and the exact point at which a host-key warning matters.
A validly signed remote command crossed the trust boundary into connected WordPress sites. Key revocation and removal of earlier site changes are separate tasks.
The eight Oracle Trusted Answer Search fixes, who can reach each flaw, why the two 9.9 scores do not mean unauthenticated access, and what version 26.1 operators should verify before patching.
OpenCode patched a Windows and WSL MCP OAuth command-injection path. The HTTPS guard alone did not stop the demonstrated payload; the browser-opener update did.
Mozilla found eight recoverable eMudhra intermediate keys. Firefox blocked them; root distrust now puts about 30,000 certificates into migration, according to eMudhra.
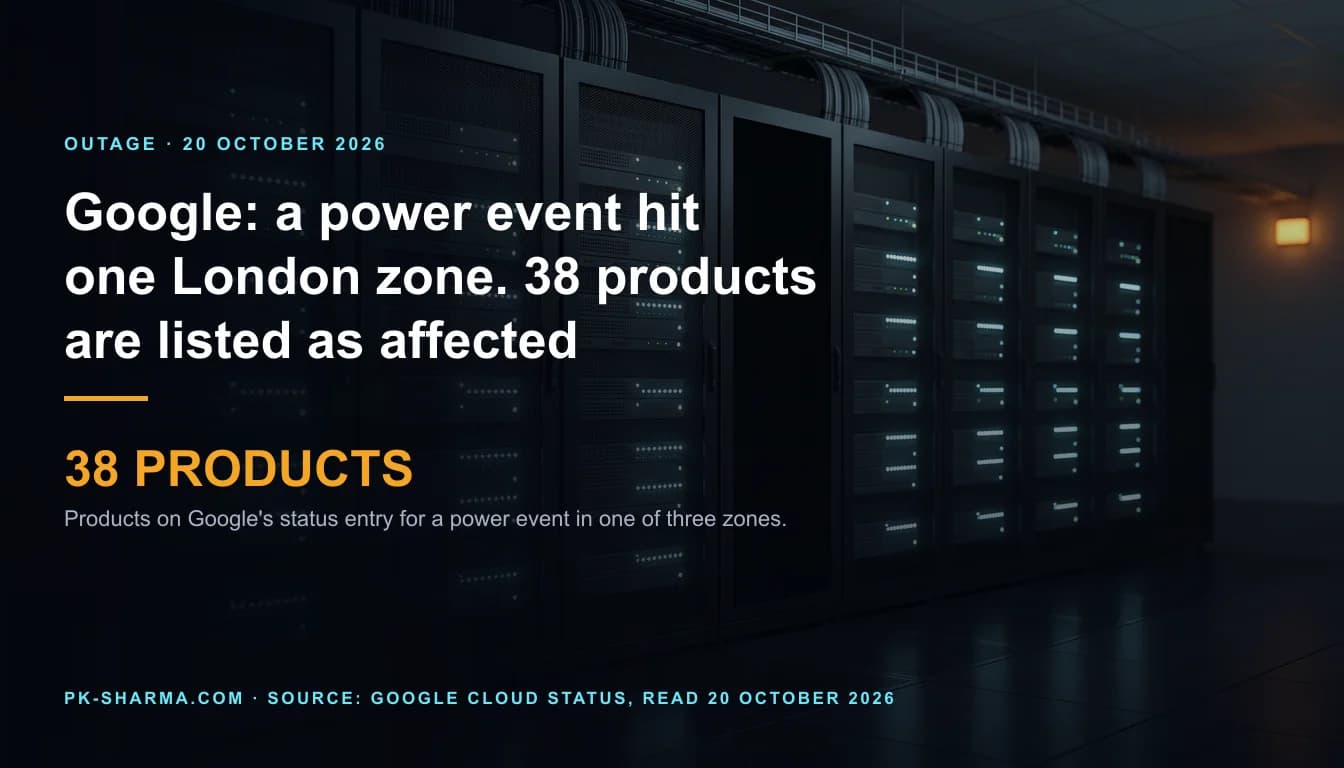
What Google's status entries say, minute by minute, what its documentation and SLAs promise when one zone fails, who said what in the UK, and what the PRA, FCA, ICO and Treasury regimes require. A developing incident, time stamped.
What Bullhorn's status page, FAQ and known limitations page state and do not state about its cyber incident, the credential changes, and what UK controllers and processors must do under the ICO and NCSC texts. Time stamped 20 October 2026.
What the NCSC's new AI chapter asks, counted from the pages read on 20 October 2026: seven problems and 33 strands, which have a published UK answer, which words it leaves undefined, what it does not state, the UK routes to engage, and a ranked checklist.
What the public issue, GitHub's release records, the Homebrew tap and OVHcloud's statements show: which files were swapped, which install routes were exposed, what immutable releases do and do not lock, what UK guidance says, and a ranked checklist. Defender level only.
What Google, ManageEngine and AOMEI say about the Backupper tampering, the intervals computed from the dates, the labels that did the work of controls, what UK guidance covers and where it stops, and a ranked checklist. Defender level only.
What Siemens's advisory, blog and CVE records state about CVE-2026-110936, the four days before exploitation was noted, two scores, what Romulus is, what UK guidance reads, and a ranked defender checklist. Defender level only.
What 510.3 GB of MIT-licensed weights need to run: memory by format against NVIDIA hardware, a 890-byte-per-token cache that only DeepSeek's own stack is stated to reach, independent numbers, where hosted prompts go, UK controls and a ranked checklist.
What the second-stage count of 94 repositories and 66 owners measures, what it does not, who says GitHub blocked the first stage, what VS Code and the NCSC document, and an ordered checklist. Defender level only.
The labels on five NGINX flaws (nginx.org medium, F5 CVSS 4.0 critical for three), what each flaw needs, which press claims the records support, what the distribution trackers showed on 19 October, and the UK 5 day and 14 day clocks.
What Rank Math's notice, the CVE record and Patchstack's entry say about the PRO plugin incident, the intervals computed from them, what the notice leaves out, what a customer cannot check, the UK guidance and a ranked checklist. Defender level only.
What Plex's release notes, the CVE records, CISA and the two researchers' pages establish about Plex2Shell as of 19 October: the dates to scale, four scores that miss the chain, the build that is actually fixed, what UK guidance requires, and a ranked checklist. Defender level only.
A computed diff of MITRE's version 19.2 and 20.0 STIX data: nine new Enterprise entries, six detection strategies, SecurityWeek's claims checked, the water and Mexico campaigns against their cited sources, how NCSC pages use ATT&CK, and a ranked checklist.