Guide
What is NIS2?
Who NIS2 catches, what Article 21 actually demands, the 24 hour reporting clock, and why organisations outside its scope are being pulled in through their customers.
NIS2 is Directive (EU) 2022/2555, the European Union's cyber security law for organisations that matter to the functioning of society and the economy. Member States had to write it into national law by 17 October 2024. Two things about it are less well understood than they should be. Its supply chain obligation reaches organisations that are not themselves in scope, including plenty in the United Kingdom, through contracts with customers who are. And in four Member States there is still no national law to comply with, because the Commission has taken them to court for failing to produce one.
Last reviewed:
Who it catches, and how the test works
NIS2 replaced the original 2016 NIS Directive and widened it considerably. Scope is decided by two questions asked together: what sector you operate in, and how big you are.
The sectors are listed in two annexes. Annex I covers what the directive calls sectors of high criticality: energy, transport, banking, financial market infrastructure, health, drinking water, waste water, digital infrastructure, ICT service management, public administration and space. Annex II covers other critical sectors: postal and courier services, waste management, chemicals, food, manufacturing of certain products, digital providers and research.
The size test then applies. In general you are caught if you are at least a medium-sized enterprise under Commission Recommendation 2003/361/EC, which means 50 or more staff, or annual turnover and balance sheet total both above 10 million euros.
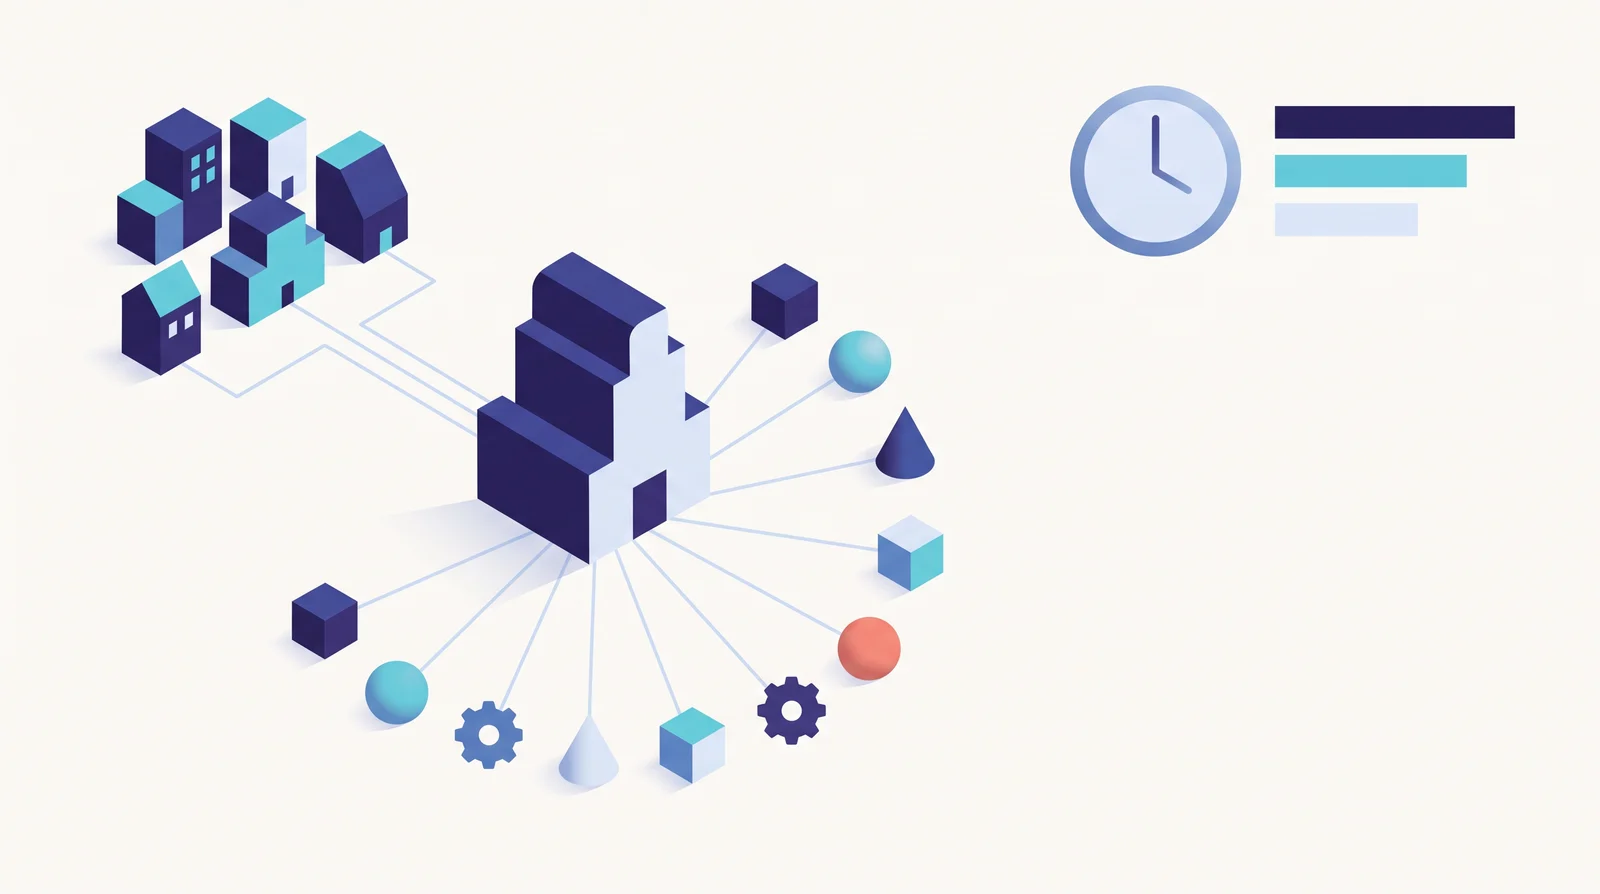
- 1Annex I and II sectors Energy, transport, health, water, digital and more
- 2The in-scope entity Medium-sized or larger, in a listed sector
- 3Direct suppliers Article 21(2)(d) makes their security your obligation
- 4The reporting clock 24 hours, 72 hours, one month
Two refinements matter. Some entities are in scope regardless of size, including certain DNS service providers, top-level domain registries and trust service providers. And Member States may bring smaller organisations in where they play a key role for society, the economy or a particular sector. This is why the directive alone cannot answer the question: the national law is the one that binds you, and it may be wider.
The part that catches organisations that are not in scope
This is the least understood provision in the directive and the one most likely to reach a reader of this site.
Article 21(2)(d) requires in-scope entities to adopt measures covering "supply chain security, including security-related aspects concerning the relationships between each entity and its direct suppliers or service providers".
An essential entity cannot discharge that obligation by hoping its suppliers are secure. It discharges it by imposing requirements on them contractually and checking. The result is that NIS2 propagates down supply chains as commercial terms, and it does so across borders, because the directive does not care where a supplier is established.
What Article 21 actually requires
The directive names ten measures. They are deliberately outcome-based rather than prescriptive, which is why they map cleanly onto an ISO 27001 management system if one already exists.
The ten measures in Article 21(2)
| Article 21(2) | The measure | What evidence looks like |
|---|---|---|
| (a) | Policies on risk analysis and information system security | A risk assessment with owners, dates and decisions |
| (b) | Incident handling | A tested procedure, not a document nobody has opened |
| (c) | Business continuity, backup management, disaster recovery, crisis management | A restore that has actually been performed and timed |
| (d) | Supply chain security, including direct suppliers and service providers | A supplier register, tiering, and contract terms |
| (e) | Security in acquisition, development and maintenance, including vulnerability handling | Patch timelines and a disclosure route |
| (f) | Policies to assess the effectiveness of the measures | Evidence somebody checked whether the controls work |
| (g) | Basic cyber hygiene and cyber security training | Completion records, not an intranet page |
| (h) | Cryptography and, where appropriate, encryption | A stated position on what is encrypted and why |
| (i) | Human resources security, access control, asset management | Joiners and leavers records, an asset inventory |
| (j) | Multi-factor authentication, secured communications | MFA coverage figures, including administrators |
Nothing there is exotic. What changes under NIS2 is that these become legal obligations with a supervisory authority attached, rather than good practice an organisation adopts at its own pace.
Essential or important, and why the label matters less than people expect
Every in-scope entity is classified as either essential or important. A great deal of anxiety attaches to which one you are, and most of it is misdirected, because the obligations under Article 21 and Article 23 are identical for both. What differs is how you are supervised and what it costs when you get it wrong.
Essential entities
- Larger organisations in the Annex I sectors of high criticality, plus certain entities regardless of size.
- Supervised proactively: inspections, audits and information requests can happen with no incident and no suspicion.
- Fines up to 10 million euros or 2% of total worldwide annual turnover, whichever is higher.
- Expect to be asked to demonstrate compliance rather than to assert it.
Important entities
- The remaining in-scope entities, largely the Annex II sectors and smaller Annex I organisations.
- Supervised reactively: authorities act on evidence that something is wrong, rather than on a schedule.
- Fines up to 7 million euros or 1.4% of total worldwide annual turnover, whichever is higher.
- The obligations are the same. The difference is when somebody comes to check.
Two consequences follow from that. Building a programme that aims at "important entity" standards because you believe you fall on that side is building to the same requirement with less evidence, which is a poor trade even if the classification turns out to be right. And the classification is made under national law rather than by you, so it can change without your doing anything.
The useful framing is that essential and important describes the regulator's posture, not the standard of care.
What counts as a significant incident
The reporting duty is triggered by a significant incident, and Article 23(3) defines it with two alternative limbs. An incident is significant if either holds.
Article 23(3), the two limbs
(a) it has caused or is capable of causing severe operational disruption of the services or financial loss for the entity concerned

(b) it has affected or is capable of affecting other natural or legal persons by causing considerable material or non-material damage
- 01
(a) it has caused or is capable of causing…: Harm to you. Note capable of causing: a near miss that could have taken the service down qualifies, whether or not it did. - 02
(b) it has affected or is capable of affec…: Harm to others. This is the limb that catches incidents where your own operations were fine but customers, patients or citizens were exposed.
The phrase doing the work in both is capable of causing. The test is not whether damage occurred; it is whether the incident could have produced it. An organisation that reports only realised harm is applying a narrower test than the directive sets, and will under-report.
That matters because under-reporting is itself an infringement, and it is one that becomes visible in hindsight, when an authority reviews an incident you handled quietly and asks why no early warning was filed.
The reporting clock
Article 23 sets a staged timetable that begins the moment you become aware of a significant incident, which is earlier than the moment you have understood it.
What Article 23 requires, and when
Within 24 hours
Early warning
State whether the incident is suspected to be caused by unlawful or malicious acts, and whether it could have cross-border impact. Little more is expected this early.
Within 72 hours
Incident notification
Update the early warning and provide an initial assessment: severity, impact, and any indicators of compromise available.
On request
Intermediate report
Status updates, where the CSIRT or competent authority asks for them.
Within one month
Final report
A detailed description, the type of threat and likely root cause, mitigation applied, and any cross-border impact.
The 24 hour stage is the one organisations fail, and they fail it for a predictable reason: they wait until they know what happened. The early warning is not a diagnosis and the directive does not ask for one. It asks whether this looks malicious and whether it might cross a border.
Management liability, which is what changes the conversation
Article 20 is short and consequential. Management bodies must approve the risk-management measures, oversee their implementation, and can be held liable for infringements. Separately, members of management bodies are required to follow training, and entities are encouraged to offer similar training to staff.
€10m
or 2% of worldwide turnover
Essential entities, whichever is higher
€7m
or 1.4% of worldwide turnover
Important entities, whichever is higher
24h
to the first report
From awareness, not from diagnosis
Art 20
management can be liable
And must follow training
The practical effect is that the board paper changes. A director who has approved measures they do not understand has satisfied the letter of Article 20 and none of its purpose, and the training obligation exists precisely to close that gap.
Where the law actually is, which is not where you would expect
The directive required transposition by 17 October 2024. That did not happen, and the gap between the deadline and reality is now unusually well documented, because the Commission has been publishing each escalation.
Transposition, and the enforcement that followed
17 Oct 2024
Transposition deadline
The date by which every Member State had to have NIS2 in national law.
28 Nov 2024
Formal notices to 23 Member States
The Commission opened infringement procedures, giving two months to respond.
May 2025
Reasoned opinions to 19
The second stage of infringement, requiring transposition or facing sanctions.
8 Jul 2026
Four referred to the Court of Justice
Ireland, Spain, France and the Netherlands, with a request for a lump sum and daily penalties until transposition is notified.
For anyone operating across Europe this has a concrete consequence. The obligations are not identical from country to country and in some of them they are not yet law at all. A group compliance programme built on the directive alone will be wrong in both directions: too narrow where a Member State went further, and premature where no national instrument exists.
Where Member States have transposed, several have gone beyond the directive. Registration requirements, sector definitions and reporting portals differ, and the entity classification that determines your supervision regime is made nationally.
Registration, which is a duty rather than a formality
NIS2 works from lists. Article 3(3) required Member States to establish a list of essential and important entities, and of entities providing domain name registration services, by 17 April 2025, reviewed at least every two years. Article 3(4) puts the burden of populating it on entities themselves: you submit your name, address and current contact details including email addresses, IP ranges and telephone numbers, your sector and subsector where relevant, and the Member States in which you provide in-scope services.
Changes must be notified without delay and in any event within two weeks.
Two things follow that catch people out. Registration is self-assessed, so nobody tells you that you are in scope; concluding you are and saying so is your obligation, and failing to register is an infringement in its own right rather than a missing formality. And the IP range requirement means the submission is not purely administrative: it asks what you actually operate, which is a question a surprising number of organisations cannot answer quickly.
How it overlaps with everything else you are already doing
Almost nobody meets NIS2 from a standing start, and the question that actually arises is what the existing work already covers.
ISO 27001 is the closest fit and the most useful place to start. The ten measures in Article 21(2) map onto an ISO 27001 management system almost clause for clause, because both are built around risk assessment, documented controls and evidence that somebody checks whether they work. Certification is not compliance with NIS2 and no supervisory authority treats it as such, but an organisation with a working ISMS has the machinery and mostly needs to extend its scope and its supplier work. An organisation without one is building that machinery for the first time under a legal deadline, which is the harder version.
DORA covers financial entities and is a regulation rather than a directive, so it applies directly and identically across the EU with no national variation. Where both could apply, DORA generally takes precedence as the more specific regime. That distinction matters practically: a bank does not get to choose the softer framework, and a group with both regulated and unregulated arms may be running two regimes at once.
The UK regime is separate. The NIS Regulations 2018 remain in force and the Cyber Security and Resilience Bill is the vehicle for updating them. A UK organisation with EU operations is therefore managing two distinct sets of obligations, and the supply chain provision means it may also be meeting a third set contractually.
GDPR sits alongside rather than underneath. A single incident can require notification to a data protection authority within 72 hours under GDPR and an early warning within 24 hours under NIS2, to different regulators, on different clocks, with different tests. Organisations that discover this during an incident discover it too late, which is why the reporting path is the first thing to fix.
What to do about it
A defensible order of work
- 1
Establish whether you are in scope, per country
weeks 1 to 2
Sector against Annex I and II, size against the medium-enterprise test, then the national law in each country you operate in. Record the reasoning, including for entities you conclude are out.
- 2
Ask your EU customers what they are passing down
weeks 1 to 2
If you are not in scope directly, this is where your obligations actually come from, and the answer is in your contracts rather than in the directive.
- 3
Map what exists against the ten measures
weeks 3 to 6
Most organisations have more than they think and can evidence less than they have. The gap is usually evidence rather than control.
- 4
Fix the reporting path before anything else
weeks 3 to 4
24 hours is short. Know who declares an incident, who writes the early warning, and which authority receives it, in each country.
- 5
Put it in front of the board, in writing
week 6
Article 20 makes approval and oversight a named duty. An approval that is not minuted is difficult to evidence later.
Where to go next
The regulatory scope checker on this site works through the sector and size tests for NIS2 alongside DORA and the UK legislation, and tells you which of them reach you rather than describing all three.
If the ten measures in Article 21 look familiar, that is because they map closely onto an ISO 27001 management system, and the guide to that standard sets out what certification actually involves.
If the supply chain provision is the part that affects you, the practical work is a supplier register with tiering and evidence, which is where a compliance assurance engagement usually starts.
Common questions
›Does NIS2 apply to my organisation?
It applies if you operate in one of the sectors listed in Annex I or Annex II of the directive and you are at least a medium-sized enterprise, meaning 50 or more staff, or annual turnover and balance sheet total above 10 million euros. Member States may also bring in smaller organisations that play a key role for society or a particular sector, so the national law is the final word rather than the directive alone.
›What is the difference between essential and important entities?
The obligations are the same; the supervision and the penalties are not. Essential entities face proactive supervision, including inspections that can happen without any incident, and administrative fines up to 10 million euros or 2% of total worldwide annual turnover, whichever is higher. Important entities are supervised reactively, after evidence of a problem, and face fines up to 7 million euros or 1.4%.
›Does NIS2 apply to UK companies?
Not directly, since the United Kingdom is outside the EU. It reaches UK organisations through Article 21(2)(d), which requires in-scope entities to manage the security of their direct suppliers and service providers. That obligation is passed down in contracts, so a UK supplier to an EU essential entity meets NIS2 requirements as a commercial term rather than as law.
›What are the NIS2 reporting deadlines?
Three stages under Article 23. An early warning within 24 hours of becoming aware of a significant incident. A fuller incident notification within 72 hours, with an initial assessment of severity and impact. A final report no later than one month after that notification. An intermediate report may also be requested at any point by the CSIRT or competent authority.
›Can directors be held personally liable under NIS2?
Article 20 requires management bodies to approve the cyber security risk-management measures, oversee their implementation, and states they can be held liable for infringements. It also obliges members of management bodies to follow training. This is the provision that changes the conversation in most boardrooms, because it makes cyber security risk a personal exposure rather than only an organisational one.
›Is NIS2 in force yet?
The transposition deadline passed on 17 October 2024, but it is national law that binds you rather than the directive itself. The Commission opened infringement proceedings against 23 Member States in November 2024, issued reasoned opinions to 19 in May 2025, and on 8 July 2026 referred Ireland, Spain, France and the Netherlands to the Court of Justice with a request for financial penalties. Check the status in each country you operate in.
Where to go next